Kubescape: New Features, Improvements, and Future Developments
Explore Kubescape's latest updates, improvements, and future plans for enhanced Kubernetes security and compliance management.
KubeClarity - Bringing Clarity to Kubernetes Artifacts Security
Discover how KubeClarity enhances security for Kubernetes artifacts, providing comprehensive visibility and protection for your cloud-native applications.
Bypassing Falco - How to Compromise a Cluster without Tripping the SOC
Explore techniques to bypass Falco's default ruleset, enabling stealthy cluster compromise. Learn 9 bypass classes for target enumeration, privilege escalation, and lateral movement without alerting security teams.
Notary v2 - Deep Dive and Open Issues
Explore Notary v2's status, open issues, and future work in this deep dive. Learn about formats, standardization, and security challenges in this community-driven project for improved registry operations.
CRI-O - Secure, Performant, and Boring as Ever
Explore CRI-O's recent improvements in security, performance, and stability for Kubernetes container runtime. Learn about CRI version transitions, container exec probe optimizations, and enhanced security features.
Threat Hunting at Scale - Auditing Thousands of Clusters With Falco and Fluent
Explore large-scale threat hunting using Falco and Fluent for auditing thousands of Kubernetes clusters, covering data pipelines, monitoring, log processing, and challenges.
Cloud Native Live: Workload Misconfiguration - The #1 Security Threat When Using Kubernetes
Explore workload misconfiguration, the primary security threat in Kubernetes environments, and learn effective strategies to mitigate risks and enhance cloud-native security.
Secure Supply Chains with Tekton Chains - CNCF
Learn about Tekton Chains for secure software supply chains, including installation, configuration, and verification of provenance documents.
Cloud Native Live - Locking Down Your Cluster
Explore strategies for enhancing Kubernetes cluster security, including best practices, tools, and techniques to protect against vulnerabilities and unauthorized access.
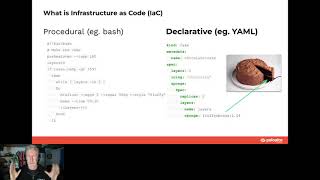
Desktop to Deployment: Kubernetes Security with Checkov
Explore K8s security from desktop to deployment using Checkov. Learn about OS Top 10, CI monitoring, customization, and admission controllers for robust cloud-native security practices.
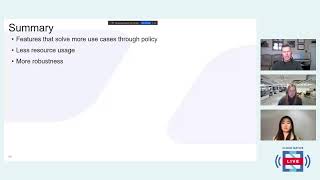
Cloud Native Live: What's New with Kyverno
Explore Kyverno's latest features for cloud-native policy management, including architecture updates, new policy structures, and critical enhancements for improved validation and organizational strategies.
Harbor - Enterprise Cloud Native Artifact Registry
Explore advanced features of Harbor, an open-source registry for cloud-native artifacts. Learn about image signatures, cloud management, unified Helm and container handling, and high-availability deployments.
Tweezering Kubernetes Resources - Operating on Operators
Explore Kubernetes Operators' security risks, threat modeling, and best practices for secure implementation. Learn to assess third-party Operators and conduct effective code reviews for enhanced cluster safety.
Three Surprising Kubernetes Networking Features and How to Defend Against Them
Explore surprising Kubernetes networking vulnerabilities and learn effective defense strategies to protect your clusters from potential attacks and compromises.
A Treasure Map of Hacking and Defending Kubernetes
Comprehensive guide to Kubernetes security: threat modeling, attack demonstrations, defense strategies, and advanced topics like workload identity and runtime hardening for robust cluster protection.
The Hitchhiker's Guide to Pod Security
Explore Pod Security admission in Kubernetes, its key concepts, and practical implementation. Learn how to enforce secure defaults for workloads using this new security-focused API.
Kubernetes Repositories and Registries Scanning with Kubescape
Explore Kubescape's capabilities for scanning Kubernetes repositories and registries, enhancing security and compliance in cloud-native environments.
Trampoline Pods: Node to Admin Privilege Escalation in Popular Kubernetes Platforms
Explore Trampoline Pods: powerful pods that can enable cluster takeover if compromised. Learn about detection, exploitation, and mitigation strategies for this critical Kubernetes security vulnerability.
gVisor and Falco - Strengthening Kubernetes and Container Security with Visibility
Explore container sandboxing with gVisor and enhance security monitoring using Falco, improving Kubernetes protection without compromising visibility.
Securing GitOps Supply Chain with Sigstore and Kyverno
Learn to secure GitOps supply chain by signing and verifying container images using Sigstore and Kyverno, eliminating security risks and ensuring only trusted images are deployed in Kubernetes clusters.
Best Practices for Calico Installation in Cloud Native Environments
Learn essential best practices for installing Calico, the popular open-source networking and security solution for Kubernetes clusters, to ensure optimal performance and reliability.