Reproducible Builds with BuildKit for Software Supply Chain Security
Learn how BuildKit enables reproducible builds to enhance software supply chain security, ensuring verifiable and trustworthy Docker images through bit-for-bit identical reproduction from source code.
Leveraging Sigstore Capabilities in a Local Environment
Explore Lockheed Martin's integration of Sigstore for secure, auditable software development. Learn about internal Kubernetes deployments, certificate authorities, and streamlined GitLab pipelines for enhanced security.
Mastering Web Security - Myths, Strategies and Best Practices
Debunking web security myths and exploring effective defense strategies. Experts share practical tips, valuable resources, and emphasize organizational commitment for robust application security.
Driving the Need for Identity, Authentication, and Encryption in Containerized Environments
Explore encryption, identity verification, and workload attestation in multi-service environments. Learn to implement TLS with Istio and cert-manager for robust identity management and secure communication.
SLSA: A Security Paradigm for Software Supply Chain Integrity
Explore SLSA levels, software supply chain security basics, and tools like Cosign to enhance artifact integrity and benefit your organization.
Navigating the Quantum Readiness Journey: Securing Kubernetes with Quantum-Resistant Cryptography
Explore quantum-resistant cryptography for Kubernetes security. Hands-on insights into mTLS, x.509 certs, and container signing. Learn standardization progress and empower yourself to conduct tailored experiments.
One Port to Serve Them All - Google GCP Cloud Shell Abuse
Uncovers security vulnerabilities in GCP Cloud Shell, demonstrating how attackers can exploit a public-facing port to access internal services and bypass authentication, potentially leading to data leaks and network attacks.
Enforceable Supply Chain Security Policy with OPA Gatekeeper and Ratify
Enhance container supply chain security using OPA Gatekeeper and Ratify. Learn to enforce policies, verify images, and establish trust in deployments through practical demonstrations and safeguarding techniques.
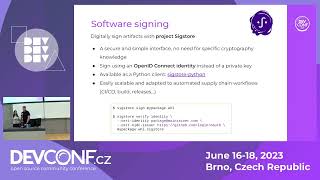
Securing Python Projects Supply Chain
Explore best practices and tools for securing Python projects' supply chain, from development to distribution. Learn about cryptographic signatures, SBOMs, and SLSA attestations.

Anchore Engine: DevSecOps Tool for Inspection, Analysis, and Certification of Infrastructure
Explore Anchore Engine for inspecting, analyzing, and certifying infrastructure, enhancing security in application development and QA processes.
DARCC - The 5 Layers of Modern App Security
Explore the DARCC layers of modern app security: Dependency, Access-Control, Runtime, Configuration, and Container. Learn best practices for securing your software supply chain and enforcing policies.
How to Start with DevSecOps on Kubernetes
Explore container security implications and strategies for Kubernetes ecosystems. Learn essential controls and best practices to secure containerized workloads in production environments.
Power of AI: DevSecOps and Cloud Artifact Signing Explored - Sessions 1 and 2
Explore AI's impact on DevSecOps and cloud artifact signing. Learn how AI enhances security automation, vulnerability scanning, and threat detection. Discover tools for ensuring trust and integrity in cloud environments.
Motivating Developers to Engage in DevSecOps - Hands-on Docker Security
Dive into DevSecOps with hands-on Docker activities, learning to identify and prevent vulnerabilities while strengthening your software security skills.
Exploiting and Fixing Vulnerabilities - A Gamified Approach
Discover how gamification and CTFs make application security tangible for developers in cloud-native environments, addressing risks across code, dependencies, containers, and clusters.
Enforcing Organization Policies with Enterprise Contract
Learn to enforce organizational policies on container images using Enterprise Contract, leveraging Sigstore signatures and in-toto attestations within the Tekton ecosystem.
Policy-Driven Supply Chain Security with Enterprise Contract
Explore Enterprise Contract for enforcing software supply chain security and compliance. Learn to verify container images, signatures, and attestations using customizable policies.
Security Concerns in Every Stage of the Software Supply Chain
Explore security concerns throughout the software supply chain, from development to deployment. Learn strategies to mitigate risks and enhance overall security posture in DevOps practices.
Forensic Analysis of Container Checkpoints
Explore forensic container checkpointing in Kubernetes, learning tools and methods to analyze checkpoints and extract crucial information for uncovering potential malicious activity.
Orchestrating Security Tools with AWS Step Functions - 2018
Automate security reviews in CI/CD pipelines using AWS Step Functions. Learn to deploy serverless systems for integrating security tools like static analysis and container scanning into developer workflows.
Cloud Native Security Exposed: A Layered Approach to Cloud Security
Explore a layered approach to cloud native security, covering threat vectors, application lifecycle, and securing compute and container layers for robust protection.