Hands-on Hacking Kubernetes and Ways to Prevent It
Hands-on workshop exploring Kubernetes vulnerabilities and prevention strategies. Demonstrates remote code execution exploit and teaches mitigation techniques for enhanced container security.
Unpacking Open Source Security in Public Repositories and Registries
Explore security risks in popular open-source projects and public registries. Learn about common misconfigurations, vulnerabilities, and best practices to safeguard your systems when using public resources.
Get Your Security Priorities Straight - Identifying Workloads Under Real Threat with Context
Discover a security prioritization system for Kubernetes workloads based on the MITRE framework, helping differentiate real threats from potential ones in various contexts.
From the Cluster to the Cloud: Lateral Movements in Kubernetes
Explore techniques for lateral movement from Kubernetes containers to cloud resources, covering RBAC misconfigurations, authentication methods, and real-world incidents. Learn prevention and detection strategies.
Windows HostProcess Containers for Configuration and Beyond
Explore Windows HostProcess Containers for efficient Kubernetes cluster management, including CNI implementation, debugging, and on-demand monitoring. Learn practical examples and novel approaches.
How SIG Release Cooks Trustworthy Artifacts From Raw Source Code - Kubernetes Build Process
Explore how Kubernetes SIG Release transforms source code into trusted artifacts, focusing on SLSA compliance, community-controlled infrastructure, and expanded artifact signing.
Finding the Needles in a Haystack - Identifying Suspicious Behaviors with eBPF
Explore how AWS uses eBPF to identify security risks in Kubernetes, including malicious activities and communication with known threats. Learn advantages, challenges, and practical applications.
Deploying Pod Security Policies Using Kyverno - A New Approach
Explore a new approach to deploying Pod Security Policies using Kyverno, addressing the challenges of Kubernetes security and offering a flexible solution for implementing robust pod security measures.

Secure and Debuggable: Debugging Slim, Scratch and Distroless Kubernetes Containers
Explore debugging techniques for optimized Kubernetes containers using Ephemeral Containers. Learn to balance security and troubleshooting in slim, scratch, and distroless environments.
Kubernetes Benchmark Report 2023 - What's Working and What's Not
Explore key findings from the 2023 Kubernetes Benchmark Report, covering reliability, security, and efficiency in cloud-native environments.
How to Build a Kubernetes Admission Controller from Scratch - Tutorial
Learn to build a Kubernetes admission controller from scratch, exploring fundamentals, installation, and Python implementation. Gain hands-on experience in enhancing cluster security and policy enforcement.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
Modifying the Immutable: Attaching Artifacts to OCI Images
Explore how to attach metadata like attestations, signatures, and SBOMs to OCI images without altering their immutable digest. Learn about standardization, implementation, and potential challenges.
Securing Kubernetes
Explore Kubernetes security strategies and best practices to protect your containerized applications and infrastructure in this informative session.
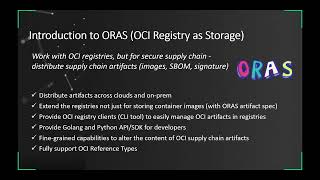
Secure Container Supply Chain with Notation, ORAS, and Ratify
Explore tools for securing container supply chains: Notation for signing artifacts, ORAS for distributing OCI artifacts, and Ratify for verifying container images.
Kubescape Roadmap - Future Developments in Kubernetes Security
Explore the future of Kubernetes security with Kubescape's development plans and upcoming features in this informative CNCF presentation.
Creating Security Policies and Controls for Kubernetes Using ChatGPT
Explore how to leverage ChatGPT for creating robust security policies and controls in Kubernetes environments, enhancing your cloud-native security practices.
Secret Management in Kubernetes: Using Secret Store CSI Driver
Explore secure secret management in Kubernetes using Secret Store CSI Driver. Learn its architecture, multi-credential provider support, and see code examples for robust security implementation.
Containerization 102 - Security, Optimization and Speed
Explore advanced containerization techniques focusing on security, optimization, and performance enhancement for cloud-native applications and infrastructure.
The Hacker's Guide to Kubernetes - Exploiting Vulnerabilities and Best Practices
Interactive demos showcasing live Kubernetes hacking, exploring OWASP Top 10 vulnerabilities and exploits. Learn to identify and mitigate security risks in k8s clusters, containers, and components.
Kubernetes Quick Wins and Migration Best Practices - RingCentral Example
Discover RingCentral's Kubernetes migration journey, focusing on security, scale, and reliability. Learn practical steps, key projects, and best practices for a successful transition to cloud-native infrastructure.