Who's Verifying Your Signatures? Approaching Private Container Image Signing
Explore container image signing for private use, comparing open-source and internal challenges. Learn about leading frameworks and their scalability for secure software delivery.
Sigstore - How We Learned to Stop Trusting Registries and Love Signatures
Explore InfluxData's journey in implementing container image signing for their SaaS offering, covering the process, challenges, and technical details from DevOps and security perspectives.
Reducing the Sticker Price of Kubernetes Security
Hands-on techniques and open-source tools for enhancing Kubernetes security, including image verification, Pod Security Standards, and SecComp profiles to prevent vulnerability exploits.
Day in the Life of a Base Image - The Evolution of Vulnerabilities in Popular Containers
Explore the evolution of vulnerabilities in popular container images, understand security challenges, and learn practical steps to manage and prevent issues in your development process.
Image Signing and Runtime Verification at Scale - Datadog's Journey
Explore Datadog's innovative approach to image signing and runtime verification, addressing software supply chain security challenges in complex, large-scale environments.
Security Controls for Safe Chaos Experimentation
Explore security considerations in chaos engineering, including authentication, fault-blacklisting, runtime security, policy integration, and secrets management. Learn about new features in LitmusChaos 3.0 beta.
Guardians of the Runtime - Leveraging Behavioral Analysis and Policies for Kubernetes Security
Explore innovative Kubernetes security using behavioral analysis in CI testing and native policies. Learn hands-on practices for implementation and enforcement to protect against latest threats.
Malicious Compliance: Reflections on Trusting Container Scanners
Explore creative ways to bypass container image analysis and admission control detection, revealing limitations of validation tools and improving security policy creation.
Practical Challenges with Pod Security Admission
Explore challenges in implementing Pod Security Admission, including handling privileged workloads and applying the principle of least privilege. Learn strategies for securing Kubernetes environments.
Hacking and Defending Kubernetes Clusters - Live Demonstration
Live demonstration of Kubernetes cluster attacks and defenses, exploring vulnerabilities, mitigation strategies, and practical security techniques for effective threat modeling and protection.
Securing the Container Supply Chain with Notary
Explore Notary v2's advanced capabilities for securing software supply chains, including core functionalities, enterprise scenarios, and ecosystem integrations.
Kubernetes Security Response Committee: Introduction and Deep Dive
Explore the Kubernetes Security Response Committee's role, vulnerability lifecycle, and key findings from the 2022 security audit. Learn about reporting processes and community impact.
Running Not Root Made Easy in Kubernetes
Explore challenges and solutions for running Kubernetes workloads without root privileges, focusing on KubeVirt's transition and broader applications for securing non-root applications.
Kubernetes Defensive Monitoring with Prometheus
Explore innovative uses of Prometheus for defensive monitoring in Kubernetes, complementing traditional security tools. Learn practical examples and ready-to-use strategies for enhancing your cluster's security posture.
Cluster Grey Zone - Risks in Managed Cluster Middleware
Explore security risks in Managed Cluster Middleware for cloud-based Kubernetes services. Learn about potential vulnerabilities, threat surfaces, and how to adjust your K8s threat model accordingly.
Prevent Embarrassing Cluster Takeovers - Detecting and Mitigating Configuration Risks
Discover how to secure Kubernetes clusters against common misconfigurations and vulnerabilities using Kubeaudit, an open-source scanner that detects and mitigates risks without hindering developer productivity.
Experience with Hard Multi-Tenancy in Kubernetes Using Kata Containers
Explore Databricks' implementation of hard multi-tenancy in Kubernetes using Kata Containers, addressing challenges, trade-offs, and cloud provider heterogeneity for secure serverless platforms.
Least Privilege Containers: Keeping a Bad Day from Getting Worse
Explore strategies for reducing container privileges, enhancing security through unprivileged users and minimal images, and implementing design changes to segment permissions and prevent future vulnerabilities.
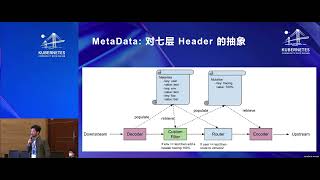
K8s Multi-Cluster Multi-Protocol Security with Aeraki - Session 7
Explore multi-cluster and multi-protocol security in Kubernetes with Aeraki, focusing on advanced techniques for robust and scalable cloud-native environments.
Kubernetes Security Implementation Landscape
Explore Kubernetes security implementation strategies and best practices with expert Zhang Jintao, gaining insights to enhance your cloud-native infrastructure protection.
Container Patching: Making It Less Gross Than the Seattle Gum Wall
Explore strategies for efficient container patching, including prevention, detection, fixing, and monitoring. Learn about opensource tools and best practices to streamline the process and meet security requirements.