Flux at the Point of Change - Using Kubernetes Golang SDK and Flux API to Automatically Fix and Deploy CVEs - Lecture
Explore automated CVE remediation in Kubernetes using Client-Go SDK and Flux API. Learn to enhance security across enterprise applications and golden images.
Securing Kubernetes - Best Practices and Effective Strategies
Explore best practices for securing Kubernetes deployments, covering control plane protection, RBAC, network policies, security contexts, and container image security.
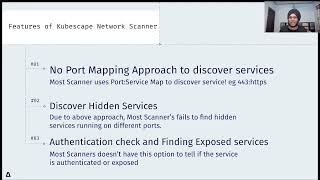
Harness the Power of Kubernetes Network Scanning for Improved Security Posture
Discover how Kubernetes network scanning enhances security posture, providing insights and strategies to protect your cloud-native infrastructure effectively.
Container and Kubernetes Security Policy Design - 10 Critical Best Practices
Explore 10 crucial best practices for designing robust security policies in container and Kubernetes environments, enhancing protection and mitigating risks.
Container Security: Supply Chain, Authorization, and Runtime Protection
Explore container security: supply chain integrity, deployment authorization, and runtime protection. Experts discuss in-toto, TUF, Open Policy Agent, and container escape prevention.
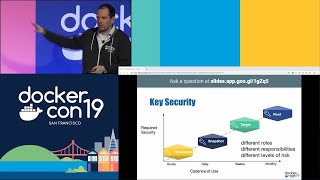
Using Docker Content Trust with Kubernetes Admission Controllers to Secure Runtime
Enhance container security by implementing image signing in CI/CD pipelines and restricting Kubernetes deployments to verified images using TUF/Notary and admission controllers.
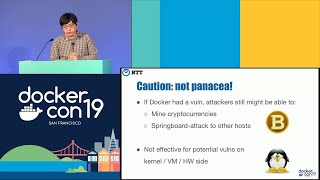
Hardening Docker Daemon with Rootless Mode
Explore Docker's Rootless mode for enhanced security and non-root usage. Learn implementation details, benefits, and future enhancements from the feature's creator.
Challenges in Enterprise Containers-as-a-Service Implementation - Beyond Container Execution
Explore challenges beyond container deployment: Day 2 operations, security, scaling, CI/CD, hybrid cloud strategies, and enhancing team experience for enterprise Container-as-a-Service success.
Don't Have a Meltdown - Practical Steps for Defending Your Apps
Practical strategies to protect applications from security vulnerabilities like Meltdown, with actionable steps for robust defense and risk mitigation.
Creating Effective Docker Images
Learn best practices for building efficient, secure Docker images, optimizing size and performance for faster deployments and reduced resource usage.
Container-Relevant Upstream Kernel Developments for Linux
Explore recent Linux kernel developments enhancing container functionality, including namespaced capabilities, LSM stacking, and user-id shifting filesystems. Understand their significance and potential impact.
Modern App Security with Docker Containers - Panel Discussion
Explore how Docker Containers revolutionize app security, enabling immutable infrastructure, faster patching, and secure software supply chain management for enterprises.
Secure Kubernetes from Dev to Prod with Docker Enterprise Edition
Learn advanced multi-tenant access controls and secure image management for Kubernetes deployments, enhancing security throughout the application lifecycle with Docker Enterprise Edition.
Enabling High Assurance and Sensitive Container Workloads with Encrypted Images
Explore encrypted container images to protect sensitive code and data, enforce security policies, and control execution environments for high-assurance workloads in enterprise settings.
Automating the DoD Container Hardening Pipeline
Explore DoD's automated container hardening pipeline, reducing vulnerabilities by up to 95% while maintaining functionality. Learn methodologies for instrumenting, testing, and optimizing containers to meet strict security standards.
Verifiable End-to-End Secure OCI Native Machines
Explore a secure toolchain for verifiable workloads using signed OCI images, ensuring tamper-proof boot processes and authenticated communication with hosts.
A Checklist for Security from Container to Kubernetes - An End-to-End Overview
Comprehensive overview of container and Kubernetes security, covering lifecycle, supply chain, infrastructure, features, and potential attacks. Practical insights for robust cloud-native security implementation.
What We Learned Dissecting the World's Most Popular Containers
Explore insights from analyzing popular containers, covering size, complexity, package landscape, and security vulnerabilities to enhance container management and optimization strategies.
Improving Container Security with System Call Interception
Explore advanced container security using system call interception, focusing on unprivileged containers, selective action monitoring, and practical applications in LXD.
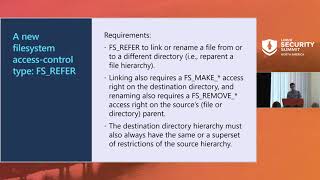
Landlock Update: File Reparenting and Network Rules Support
Explore Landlock's latest updates: file reparenting improvements and new network access controls for enhanced app and container security in Linux systems.
Enforcing a Secure Supply Chain on Kubernetes
Explore implementing and enforcing a secure supply chain in Kubernetes using open-source projects, including Sigstore keyless workflow and signature verification policies.