Integrations 101
Comprehensive guide to Snyk integrations, covering IDE setup, CLI usage, Git onboarding, Jira integration, and reporting. Ideal for new users and administrators seeking to enhance security in their development pipeline.
Securing Managed Kubernetes Clusters
Explore Kubernetes security for managed cloud clusters, understanding threat models and gaining actionable recommendations for secure workload deployment in this comprehensive overview.
Kubernetes Ingress-Nginx Security from Beginner to Expert - 2019
Learn to secure Kubernetes applications using Nginx-Ingress Controller, covering various configuration techniques to protect against vulnerabilities and enhance overall cloud security.

How to Reduce Risk & Liability with Kubernetes + Lens Autopilot
Discover how to enhance Kubernetes cluster security, gain full observability, and streamline DevOps with Lens and Lens Autopilot. Learn best practices and see live demos of these powerful tools in action.
Getting Started with Kubernetes
Learn Kubernetes fundamentals, its role in cloud-native infrastructure, and career implications. Explore containers, microservices, and practical applications with expert Nigel Poulton in this comprehensive introduction.
Resilient DevOps Practices with Code to Cloud Automation
Discover GitHub Actions for Azure to create resilient code-to-cloud workflows, implement governance with Azure Policies, and enhance container security through automated scanning.
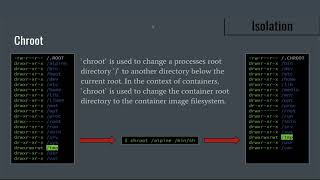
Introduction to Docker Hacking
Explore Docker container security, including namespaces, cgroups, and vulnerabilities. Learn hacking techniques and best practices for securing containerized environments.
Digging Into Container Image Layers for Sneaky Vulnerabilities
Explore techniques to identify and mitigate hidden vulnerabilities in container image layers, focusing on Java-based images and using tools like Trivy and dive for in-depth analysis.
Threat Modeling Kubernetes - A Lightspeed Introduction
Discover threat modeling for Kubernetes: Learn to identify risks, understand adversarial techniques, and implement preventive measures to enhance cloud-native system security and delivery velocity.
Flux Security Deep Dive: Authorization, Multitenancy, and GitOps
Explore Flux v2's security aspects, authorization model, multitenancy, and configuration options for platform admins. Learn about GitOps, tenant onboarding, and Flux's roadmap for 2022.
Securing Kubernetes Manifests with Sigstore and Kyverno
Learn to secure Kubernetes resources using Sigstore for signing YAML definitions and Kyverno for verification during admission controls, with real-world use cases for tamper-prevention and approval workflows.
Kubernetes Security and Governance Made Easy Using Otomi
Discover how Otomi simplifies Kubernetes security and governance, leveraging open-source projects to enhance container and network security policies through an intuitive web interface, reducing misconfigurations and attack surfaces.
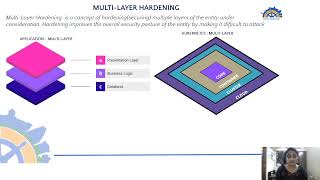
Multi-Layer Hardening in Kubernetes - DevSecOps Practices and Tools
Explore DevSecOps practices and tools for enhancing Kubernetes security, including multi-layer hardening techniques, industry standards, and a unified DevSecOps pipeline approach.
Generating Security Policies with eBPF - Hands-on Walkthrough
Explore eBPF-based solutions for capturing security events and generating policies. Learn to leverage tools like seccomp, Inspektor Gadget, and Tetragon for comprehensive system protection.
Building Images for the Secure Supply Chain
Techniques and tools for building secure container images, including distroless philosophy, updating dependencies, using apko for reproducibility, and signing with Sigstore.
Migrating From PodSecurityPolicy - Challenges and Alternatives
Explore the migration from PodSecurityPolicy to Pod Security admission controller in Kubernetes v1.25. Learn challenges, alternatives, and strategies for a safe and confident cluster upgrade.
GitOps with Flux and OCI Registries
Explore GitOps using Flux with OCI registries for continuous deployment. Learn to deploy, sign, and verify workloads, and understand the architecture behind Flux OCI as a source.
Introducing the OWASP Top Ten for Kubernetes
Explore OWASP's Top Ten Kubernetes risks, learn about common security issues, and discover strategies to enhance your containerized infrastructure's protection.
Hands-on Workshop: Batten Down the Hatches - A Cluster Security Journey
Hands-on workshop guiding security engineers through a Kubernetes cluster security audit. Learn inventory, assessment, least privilege enforcement, and compliance in a real-world environment.
The Eye of Falco: Detecting Container Escape Techniques with Linux Capabilities
Explore container security vulnerabilities and learn how Falco can detect and respond to container escape techniques based on Linux capabilities, with real-world CVE examples.
DockerSlim and Kyverno - Enhancing Kubernetes Workload Security
Explore how DockerSlim and Kyverno enhance Kubernetes workload security through container image minification, automated AppArmor and SecComp profiles, and simplified cluster security management.