Understanding the Attack Surface and Attack Resilience of Project Spartan's New EdgeHTML Rendering Engine
Explore EdgeHTML's attack surface, compare it with MSHTML, and analyze exploit mitigations in Windows 10's new rendering engine for enhanced web security understanding.
Blindspots
Robert Hansen shares insights on overlooked areas in web application and browser security, challenging industry professionals to broaden their thinking and address critical blindspots.
Pavlovian Security - How To Change the Way Your Users Respond When the Bell Rings
Learn to influence user behavior for better security through Pavlovian techniques. Explore motivations, failures, and practical strategies to raise awareness and create secure habits in your organization.
EmPoWeb - Empowering Web Applications with Browser Extensions
Explores security risks of browser extension APIs, revealing how web apps can exploit them to bypass SOP, access sensitive user data, and perform privileged actions on users' devices.
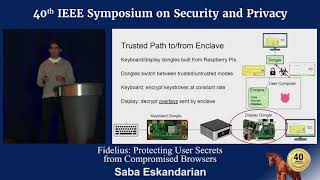
Fidelius - Protecting User Secrets from Compromised Browsers
Innovative architecture using trusted hardware enclaves to protect sensitive user data during web browsing, even in fully compromised environments. Offers secure form data, JavaScript, XMLHttpRequests, and storage solutions.
Crippling HTTPS with Unholy PAC
Explore how malicious Proxy AutoConfiguration can compromise HTTPS security, leak sensitive data, and enable cross-platform attacks, even on secure networks and browsers.
The Leaky Web - Automated Discovery of Cross-Site Information Leaks in Browsers and the Web
Explore automated techniques for identifying cross-site information leaks in web browsers, enhancing understanding of web security vulnerabilities and potential mitigation strategies.
WebSpec - Towards Machine-Checked Analysis of Browser Security Mechanisms
Explore machine-checked analysis of browser security mechanisms, focusing on WebSpec's approach to enhancing web security through formal verification and automated reasoning techniques.
Building Layers of Defense with Spring Security
Comprehensive guide to implementing multi-layered security in Spring applications, covering authentication, authorization, protection against common web vulnerabilities, and custom security configurations.
Hack In The Studio - Fireside Chat
Fireside chat with cybersecurity experts Stefano Zanero and Marco Balduzzi, discussing their research, experiences, and insights in malware analysis, cyberphysical security, and emerging threats in the digital landscape.
Don't Get Owned by Your Dependencies
Explore innovative techniques for mitigating memory safety vulnerabilities in third-party C libraries, focusing on Firefox's lightweight in-memory sandboxing approach and the RLBox framework for efficient, secure application development.
The Most Secure Browser? Pwning Chrome from 2016 to 2019
Explore Chrome browser security vulnerabilities and exploitation techniques from 2016 to 2019, presented by researchers who successfully pwned Nexus 6P in Mobile Pwn2Own 2016.
Spook.js - Attacking Chrome Strict Site Isolation via Speculative Execution
Explore a novel attack on Chrome's Strict Site Isolation, leveraging speculative execution to bypass security measures and potentially compromise user data.
Runtime Analysis of Vulnerabilities and Generation of Exploits
Runtime analysis tool for detecting vulnerabilities and generating exploits. Leverages program execution to identify dataflows, usable for both offensive and defensive purposes. Includes live demonstrations and open-source release.
Diving Into IE 10’s Enhanced Protected Mode Sandbox
Explore IE 10's Enhanced Protected Mode Sandbox, its security features, and potential vulnerabilities in this in-depth technical analysis.
Million Browser Botnet
Explore how online advertising networks can be exploited to create massive browser botnets, enabling DDoS attacks, spam campaigns, and password cracking without malware or zero-day vulnerabilities.
Attacking the WebAssembly Compiler of WebKit
Explore vulnerabilities in WebKit's WebAssembly compiler, focusing on recent updates and new features. Learn about potential security risks and attack surfaces in browser implementations.
Checking Passwords on Leaky Computers - A Side Channel Analysis of Chrome's Password Leak Detect Protocol
Explore side-channel vulnerabilities in Chrome's password leak detection, revealing potential risks to user privacy and security through microarchitectural attacks on cryptographic implementations.
Incident Response on macOS
Learn essential techniques for incident response on macOS, covering forensic collection, login items, kernel extensions, startup items, and more. Gain practical insights for effective Mac security management.
All Your Browsers Are Belong to Me
Explore browser control techniques and innovative web development strategies in this engaging JSConf presentation by James Coglan.

Keeping Secrets with JavaScript - An Introduction to the WebCrypto API
Explore the Web Cryptography API, its implementation, and potential for browser-based encryption. Learn about NaCl-inspired API and the future of web security.