Fixing XSS with Content Security Policy
Learn how Content Security Policy (CSP) can prevent XSS attacks, understand its versions, browser support, and implementation strategies for web applications. Gain insights on balancing CSP with traditional security measures.

The First 200 Milliseconds of HTTPS
Explore the intricate process of HTTPS connections, from certificates to cipher suites. Gain insights into the hidden mechanisms that ensure secure web browsing and understand potential vulnerabilities.
Native Messaging for Strictly Confined Browsers
Explore native messaging implementation for Firefox snap, including WebExtensions portal and browser changes. Demonstration of functionality with extensions and future plans for other browsers.
Roadblocks for Content Security Policy (CSP) Implementation - Developer Challenges and Solutions
Explore challenges in implementing Content Security Policy (CSP) for web security, including complexity, legacy code, and browser support. Learn strategies to overcome obstacles and enhance CSP deployment.
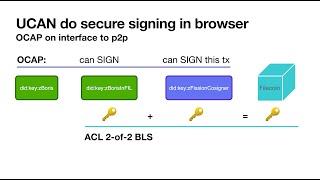
Secure Key Management in the Browser with UCAN - Fission Platform Overview
Explore secure key management in browsers using UCAN, WebCrypto API, and DIDs. Learn about Fission's platform and plans for Filecoin integration without browser extensions.

Fake CAPTCHA Malware Analysis
Explore the deceptive tactics of malware disguised as CAPTCHA, uncovering its distribution methods and analyzing its impact on cybersecurity.
Escaping Modern Web-Based App Sandboxes - Site Isolation Vulnerabilities
Explore Chrome's site isolation vulnerabilities in web-based apps, revealing how attackers can bypass security measures to execute malicious actions and compromise user data.
The Mark of the Web - Understanding Internet Security Zones
Explore the Mark of the Web security feature, its impact on file downloads, and how it affects system protection and user experience in Windows operating systems.
Towards Better Semantics Exploration for Browser Fuzzing
Explore innovative browser fuzzing techniques using production-context sensitive grammars for enhanced semantic coverage and bug detection in Chrome, Safari, and Firefox.
Back to the Roots - Finding the Origin of CSP Security Bugs
Explore the root causes of Content Security Policy bugs in web browsers, their lifecycle, and insights for both attackers and defenders using automated analysis tools.
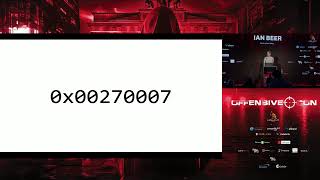
Blasting Past WebP - Exploring Image Format Vulnerabilities
Explore advanced techniques for bypassing WebP image format security measures, uncovering vulnerabilities and potential exploits in web applications.
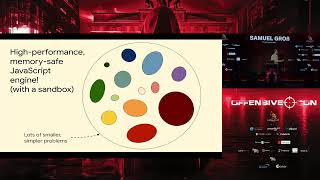
The V8 Heap Sandbox - Understanding JavaScript Engine Security
Explore V8 engine's heap sandbox implementation, its security implications, and potential vulnerabilities in Chrome's JavaScript engine.
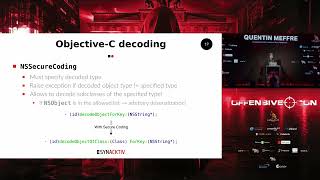
Escaping the Safari Sandbox: A Tour of Webkit IPC
Explore Webkit IPC vulnerabilities and techniques for escaping the Safari sandbox, gaining insights into browser security and exploitation.
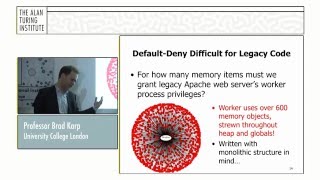
Safeguarding Users’ Sensitive Data in the Cloud and the Browser
Explore techniques for protecting sensitive data in cloud and browser environments, focusing on least privilege principle and preventing information leakage even during successful attacks.
Sneaky Extensions - Bypassing MV3 Security in Browser Extensions
Discover how browser extensions can exploit security vulnerabilities in MV3, including webcam hijacking, credential theft, and arbitrary code execution, while learning protective measures against these threats.
How to Use ZAP and ZAP HUD for Web Application Testing - LevelUp 0x04
Learn to use ZAP for web app testing and explore its new Heads Up Display feature, bringing powerful functionality directly into your browser for enhanced security analysis.
Misconfigured CORS and Web Application Security Challenges
Explore CORS misconfiguration vulnerabilities and the challenges of implementing advanced browser security features, with insights on balancing security and operational complexity.
WebRTC Security - How Secure Is P2P Browser Communication?
Explore the security implications of peer-to-peer browser communication through WebRTC, examining potential vulnerabilities and best practices for secure implementation.
Million Browser Botnet - Creating a JavaScript-Driven Browser Botnet for DDoS Attacks
Explore how online advertising networks can be exploited to create massive browser botnets for various malicious activities, including DDoS attacks and password cracking, without leaving traces.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Geeking Out with WebAssembly and Kubernetes Using ContainerD Shims
Explore WebAssembly integration with Kubernetes using ContainerD shims, covering features, risks, and practical demonstrations for cloud-native development.