Web Security: Broken by Default?
Explore web security challenges, focusing on browser vulnerabilities and emerging standards to address these issues. Learn how developers can enhance application security beyond code fixes.
Don't Get Owned by Dependencies - How Firefox Uses WebAssembly for Protection
Explore Firefox's innovative use of WebAssembly to create lightweight sandboxes for third-party C libraries, enhancing security against memory vulnerabilities and zero-day attacks.

Identity in Browsers, Single-Page Apps, and JWT Access Tokens - OAuth Happy Hour
Live Q&A session exploring OAuth and OpenID Connect, covering browser-based apps, JWT tokens, and recent developments in identity protocols. Experts discuss specifications and answer audience questions.
The Future of Cookies
Explore the evolving landscape of web cookies, their impact on privacy, and recent browser changes affecting their functionality. Learn about challenges and future trends in cookie usage.
What Can Traditional Web App Security Learn From Browser Wallet Extensions?
Explore innovative security insights from browser wallet extensions, offering fresh perspectives to enhance traditional web application protection strategies.
All That Glitters Isn't Chrome - Hunting for Suspicious Browser Extensions
Explore techniques for identifying and analyzing suspicious browser extensions, focusing on Chrome, to enhance cybersecurity awareness and protection strategies.
Your Chakra Is Not Aligned
Exploring Microsoft Chakra's JavaScript engine implementation, its vulnerabilities, and techniques for identifying bugs in new ECMAScript engines to enhance browser security.
Servo - Designing and Implementing a Parallel Browser
Explore Servo, an experimental browser engine designed for multi-core hardware, focusing on parallelization and security through Rust. Learn about its goals, design, and potential impact on web browsing.

From Zero to Zero Day
Journey from coding challenges to discovering a critical Edge browser vulnerability, with insights on JIT type confusion and browser exploitation.
Breaking Microsoft Edge Extensions Security Policies
Uncover vulnerabilities in Microsoft Edge extensions, exploring permission bypasses, data theft, and security policy breaches. Learn about browser extension security and its impact on user privacy.
Penetration Testing Considered Harmful
Critique of penetration testing practices, exploring limitations, misconceptions, and potential harm in cybersecurity. Proposes alternative approaches and challenges industry norms.
Exploiting Unknown Browsers and Objects
Discover hidden browser vulnerabilities with the Hackability Inspector, a new offensive toolkit for security researchers to explore and exploit unknown entities in embedded browsers.
Temporal - Code-Origin Policy - Towards a Formal User Privacy Protection for the Web
Explore a novel approach to web privacy protection through code-origin monitoring, offering customizable user safeguards and formal assurance mechanisms for JavaScript execution.
The "Web/Local" Boundary Is Fuzzy - A Security Study of Chrome's Process-based Sandboxing
Explore Chrome's process-based sandboxing, its security implications, and potential vulnerabilities in web browser architecture. Learn about attacks exploiting the fuzzy web/local boundary.
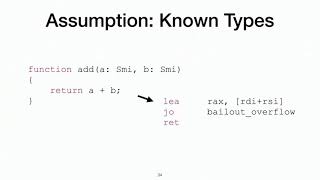
Attacking Client-Side JIT Compilers
Explore JIT compiler security in JavaScript engines, focusing on challenges, solutions, and potential vulnerabilities. Learn about optimization techniques and their impact on browser exploitation.
Cache Side Channel Attack - Exploitability and Countermeasures
Explore dangerous cache attacks, their characteristics, and real-world applications. Learn about exploitability, countermeasures, and key takeaways for protecting against these privacy-violating threats.
Chrome Security Secret Sauce
Explore Chrome's security features, threats, and protective measures. Learn about browser exploits, phishing, SSL attacks, and defense strategies from Google's "Security Princess".
Exploiting CSP in WebKit to Break Authentication and Authorization
Uncover a critical WebKit vulnerability that compromises authentication and authorization in web applications, exposing weaknesses in browser security features and their implementation.
Cutting Edge - Microsoft Browser Security — From People Who Owned It
Deep dive into Microsoft Edge security architecture, exploring sandbox initialization, browser broker implementation, and renderer security isolation.
The Power of Pair - One Template that Reveals 100+ UAF IE Vulnerabilities
Discover a unique fuzzing strategy that revealed over 100 IE use-after-free vulnerabilities. Learn about the vulnerability hunting system and techniques used to find critical browser security flaws.
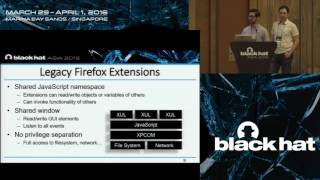
Automated Detection of Firefox Extension-Reuse Vulnerabilities
Discover a novel extension-reuse vulnerability in Firefox and learn about CROSSFIRE, a static analyzer that detects these vulnerabilities and generates exploit templates for rapid proof-of-concept creation.