API Security Fundamentals - Understanding Modern API Threats and Protection
Dive into API security challenges and solutions with Filip Verloy, exploring why APIs are becoming prime attack vectors and how traditional security measures fall short in protecting modern applications.
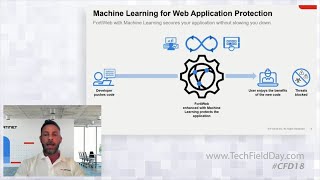
Reinventing Application Lifecycle Security Through Automation and AI
Discover how AI and automation revolutionize application security practices, enhancing SOC workflows and reducing false positives while maximizing operational efficiency in cloud environments.
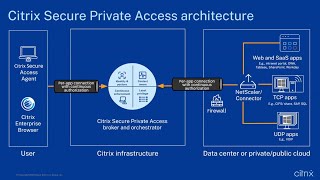
Citrix Secure Private Access - Zero Trust Architecture and Secure Application Access
Discover how Citrix's zero trust architecture enables secure application access across any infrastructure, supporting flexible deployment options for seamless user experience and device compatibility.
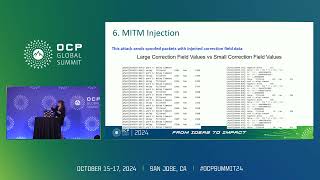
Cybersecurity Vulnerabilities in Precision Time Protocol - Attacks and Mitigations
Explore critical cybersecurity vulnerabilities in IEEE 1588's Precision Time Protocol through experimental findings, including spoofing, DoS attacks, data injection, and covert channels, with proposed mitigation strategies.
Understanding CSRF and SSRF Web Security Vulnerabilities - Demo and Examples
Explore CSRF and SSRF web security vulnerabilities through practical demonstrations, understanding attack mechanisms, key differences, and essential prevention strategies for robust application security.
Hunting for macOS Application Logic Bugs - Local Privilege Escalation Vulnerabilities
Discover critical macOS security vulnerabilities and privilege escalation bugs affecting major software products, with practical exploitation techniques and defensive strategies for improved visibility.
Empowering Developers to Embrace Security
Discover how to foster collaboration between security and development teams, enabling developers to make secure decisions from the start and build more robust applications.
Top Ways to Hack Your Company and How to Defend Against Them - 2024
Discover prevalent cybersecurity vulnerabilities and defense strategies through real penetration testing insights, focusing on authentication flaws, network poisoning, and emerging threats in modern security landscapes.
Building a Secure CI/CD Pipeline - Beyond Security Tools Integration
Discover effective strategies for optimizing security tools in CI/CD pipelines, moving beyond basic implementation to achieve meaningful security improvements and practical outcomes.
ELECTRONizing MacOS Privacy - A New Weapon in Red Teaming Armory
Discover how to bypass MacOS privacy controls through Electron apps, exploring TCC vulnerabilities and gaining insights into red teaming techniques for enhanced security testing and defense strategies.
Prototype Pollution Leading to Remote Code Execution in NodeJS
Delve into prototype pollution vulnerabilities in Node.js, exploring how they enable remote code execution, analyzing real-world exploits, and understanding recent security mitigations.
Maturing Your Application Security Program - A Practical Guide to Next Steps
Discover practical steps to advance your AppSec program through three maturity levels, with actionable strategies for immediate security posture improvement based on experience with 400+ companies.
Lessons Learned from Building and Defending LLM Applications
Gain insights into real-world challenges and practical strategies for developing secure LLM applications, exploring vulnerabilities, defense mechanisms, and best practices for robust AI systems.
Towards Secure MicroPython on Morello - Work in Progress
Explore porting MicroPython to Arm Morello, examining hardware capabilities' impact on embedded runtime security and outlining potential improvements for MicroPython's security.
LLM SecOps - Securing Large Language Model Applications
Explore LLM SecOps: from understanding and building LLM applications to addressing security challenges and implementing practical safeguards for robust AI-driven systems.
Securing the Cloud: Multi-Layered Protection for Enterprises
Explore multi-layered cloud security strategies for enterprises, covering network, application, data encryption, access management, and advanced threat detection. Gain insights on best practices and future trends.
Security at Scale: Achieving Security with Multiple Deployments per Day
Aprenda a implementar seguridad escalable en el ciclo de desarrollo de software, enfocándose en diseño, código, construcción, despliegue y monitoreo para equipos de ingeniería de plataformas.
AppSec for Everyone
Explore key components and best practices for building robust application security programs, focusing on rapid implementation for organizations new to app development.
Cover Your Apps: The Three Pillars of Application Security
Explore the three foundational pillars of Application Security (AppSec) to enhance your software development practices and create safer solutions.
Defending Cloud Native Apps Against the Serverless Top 10
Explore serverless security risks, map OWASP Top 10 to app layers, and learn practical defense strategies using open-source tools for cloud-native applications.
Snyk Free DevSecOps Tools and Resources
Explore Snyk's free DevSecOps tools for identifying and addressing vulnerabilities in your code, regardless of programming language. Learn to enhance application security with powerful resources.