Using Seccomp to Limit the Kernel Attack Surface
Explore seccomp for Linux kernel security: limit system calls, write BPF programs, and understand its applications in Docker, browsers, and more. Gain practical insights into this powerful security tool.
Securing Your Dependencies
Learn strategies to protect your applications by identifying and mitigating security vulnerabilities in third-party dependencies, enhancing your build pipeline for improved software security.
The Boring Security Talk
Explore often-overlooked security aspects in application and infrastructure, including package dependencies, CI/CD tools, email systems, and hostname resolution. Learn to protect against subtle vulnerabilities.
Using Service Meshes and Kubernetes to Solve Service-to-Service Communications
Explore Service Mesh concepts, Istio deployment, and enhancing microservice reliability, security, and visibility in large-scale Kubernetes environments.
Modern Web Application Bugs
Explore modern web vulnerabilities, including XXE, deserialization attacks, template injection, SSRF, and subdomain takeover. Learn detection and prevention techniques for emerging security threats.
Serverless and App Service Security on Azure
Practical tips for securing Azure Functions and App Service apps, including integration with other services in microservices architecture. Covers essential security measures for serverless and PaaS deployments.
The Future of AppSec is Cloud-Native
Explore cloud-native technologies' impact on application security, transforming DevSecOps from blocker to enabler. Learn tools and processes for enhanced visibility, vulnerability discovery, and feedback loops.
Modern Web Vulnerabilities 2020
Explore modern web vulnerabilities, including insecure deserialization, SSRF, ESI injection, prototype pollution, and HTTP request smuggling, with demos and prevention strategies.
The OWASP Top Ten Proactive Controls 2018
Explore critical security techniques for web application development, including secure coding practices, data protection, and access control, as outlined in the OWASP Top Ten Proactive Controls 2018.
Least Privilege: Security Gain without Developer Pain
Automated approach to implement least privilege security without impacting developer productivity. Combines data gathering and policy adjustment to remove unused permissions across applications.
Securing Tomcat: Key Considerations and Best Practices
Learn key security considerations, features, and best practices for securing Tomcat, a widely-used Java-based web server and servlet container.
Application Security Considerations in the Casino Industry - Ransomware and Vulnerability Analysis
Explore casino industry cybersecurity challenges through real-world ransomware attacks, focusing on application vulnerabilities, system compromises, and defensive strategies in gaming operations.
Let Me Show You How React Applications Get Hacked in the Real-World
Explore real-world React application vulnerabilities and learn how to prevent cross-site scripting attacks through secure coding practices and proper API usage.
How to Effect Change in the Epistemological Wasteland of App Security
Explore modern approaches to application security, moving beyond developer training to integrate security testing into agile development and DevOps practices for more effective and sustainable results.
Secure AI Orchestration: Mitigating Model-centric Attacks with Flyte
Discover how to protect AI systems from model-centric attacks, focusing on code injection and LLM vulnerabilities, while implementing security measures using Flyte orchestration and open-source tools.
Exploring Security Vulnerabilities in Flutter Mobile Applications
Discover critical security vulnerabilities in Flutter apps through reverse engineering techniques, focusing on hardcoded credentials and using tools like B(l)utter to analyze and protect mobile applications.
Secure Code, Safe Future: Mastering Security in Critical Software Development
Discover practical secure coding techniques and strategies for developing robust software, including vulnerability management, SBOM implementation, and hands-on security practices for critical infrastructure projects.
Securing the Unseen: Defending Against Open Source Software Supply Chain Attacks
Discover practical strategies to protect applications from supply chain attacks targeting open source dependencies, with real examples and actionable defense measures.
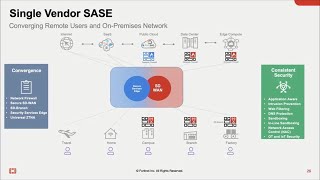
Fortinet SD-WAN and SASE - Securing Remote User Access to Applications
Discover how to implement secure remote access and consistent policies for hybrid work environments using universal ZTNA, secure private access, and SD-WAN foundations.
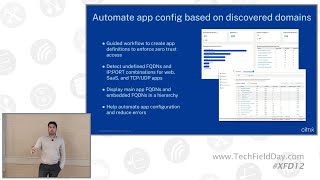
Citrix Secure Private Access - Zero Trust Network Administration Demo
Discover how to implement zero trust access through Citrix Secure Private Access, from initial setup to policy configuration and troubleshooting for IT administrators.
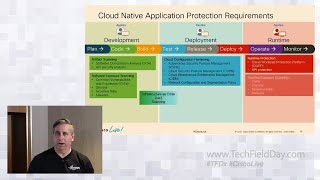
Cloud Native Application Protection Platform (CNAPP) - Understanding Security for Modern Applications
Discover how to protect cloud native applications with Cisco's CNAPP platform, exploring security threats, vulnerability assessments, and defense strategies for modern microservice architectures.