ASP.NET Core Meets OWASP Top 10
Explore ASP.NET Core's security features through the lens of OWASP Top 10, covering authentication, data protection, access control, and more for robust web application security.
Securing Your M&A Activity with Cybersecurity Due Diligence
Learn to conduct cybersecurity due diligence for M&A activities, including program components, metrics for informed decisions, and strategies for both buy and sell sides to protect and evaluate effectively.
How to Protect Your Enterprise Data - Tools and Tips
Comprehensive guide to enterprise data protection, covering various environments and compliance strategies. Learn holistic approaches to safeguard sensitive information across networks, cloud, and applications.
Crypto 101 - An Intro to Real World Crypto
Explore real-world cryptography essentials, including ciphers, elliptic curve cryptography, hashing functions, and secure password storage techniques for practical implementation.
From the OWASP Top Ten to the OWASP ASVS
Comprehensive guide to web application security, exploring OWASP standards beyond Top Ten lists. Learn about ASVS, its 180+ requirements, and how to implement a robust application security program.
From the OWASP Top Ten to the OWASP ASVS
Comprehensive guide to application security, moving beyond OWASP Top Ten to ASVS for robust security practices. Explores 180+ requirements for defining and implementing secure software development.
Command and KubeCTL - Real-World Kubernetes Security for Pentesters
Explore Kubernetes security challenges, attack techniques, and practical advice for pentesters and security practitioners in containerized environments.
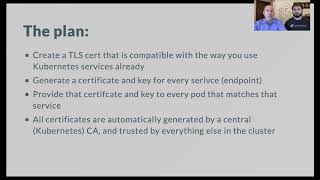
Achieving Mutual TLS - Secure Pod-to-Pod Communication Without the Hassle
Explore secure pod-to-pod communication using Mutual TLS, focusing on certificate management, implementation in Golang and Java applications, and integration with Kubernetes for streamlined security.
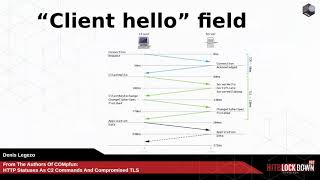
HTTP Statuses as C2 Commands and Compromised TLS
Explore innovative malware techniques using HTTP statuses as C2 commands and compromising TLS encryption. Learn about COMPFun's evolution and its impact on cybersecurity.
Zen - A Complex Campaign of Harmful Android Apps
Explore Android malware techniques, from repackaging apps to sophisticated rooting trojans. Learn about click fraud, exploit bundling, and persistence mechanisms used by malicious actors.
Web Applications Bug Hunting - Fundamentals
Explore web application security fundamentals, attack vectors, and tools for bug hunting. Learn key concepts to kickstart your career in application security.
Hacking with a Heads Up Display
Explore OWASP ZAP's Heads Up Display, a browser-integrated security testing tool designed to make security testing more accessible and user-friendly for developers, QA, and hackers.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
Automated Human Vulnerability Scanning With AVA
Explore automated human vulnerability scanning with AVA, a tool for mapping people's connectivity, testing security threats, and measuring behavior to address human security risks.
Bringing a Machete to the Amazon
Explore AWS security challenges, vulnerabilities, and solutions. Learn assessment techniques and tools to protect your cloud infrastructure and applications.
The Tactical Application Security Program - Getting Stuff Done
Aprenda a implementar um programa de segurança tático e eficaz, focando em avaliações ágeis, resposta a incidentes e gerenciamento de bugs. Descubra por que abordagens táticas podem ser mais efetivas que estratégias de longo prazo.
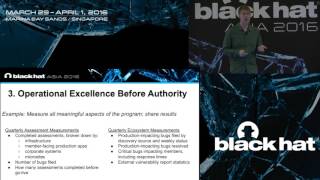
The Tactical Application Security Program - Getting Stuff Done
Practical approach to application security: lightweight team, agile methods, and operational excellence. Covers assessments, bug handling, and private bug bounty programs, with actionable advice for managers and practitioners.
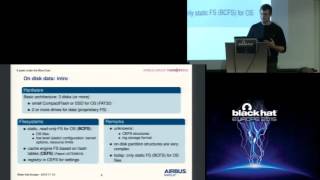
A Peek Under the Blue Coat
Detailed analysis of Blue Coat ProxySG systems, exploring OS mechanisms, file system internals, and security features. Insights for IT professionals managing web traffic proxying and filtering.
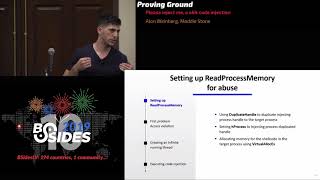
Please Inject Me - A x64 Code Injection
Explore advanced x64 code injection techniques, focusing on practical implementation and security implications in modern Windows systems.
Web Application Security Crossfire
Explore web application security challenges and solutions through expert insights in this panel discussion from Black Hat USA 2004.
OWASP Top Ten Proactive Controls
Explore essential software security controls for developers, covering authentication, access control, validation, encoding, and more. Learn to build robust, secure applications.