Hacking into Your Containers, and How to Stop It
Explore container security vulnerabilities and learn proactive DevSecOps practices to protect your deployments. Live hack demonstration and practical steps for hardening clusters against attacks.
Don't Have a Meltdown - Practical Steps for Defending Your Applications
Practical steps to defend applications against common attacks, covering authentication, injection, updates, sensitive data, and configuration. Learn to mitigate key security risks in containerized environments.

Docker Container Security
Learn to create a secure software supply chain using Docker Enterprise, focusing on image signing, scanning, and automated policies for compliant application development.
Five Keys to Building an Application Security Program in the Age of DevOps
Discover strategies for integrating security into DevOps practices, balancing risk management with rapid development, and implementing automated security measures for more secure code delivery.
Fraud Detection and Real-time Trust Decisions
Explore fraud detection techniques in online commerce, from traditional attacks to real-time marketplace challenges. Learn about combating fraud and its parallels with network security.
Fad or Future - Getting Past the Bug Bounty Hype
Panel discussion on bug bounty programs: insights, challenges, and best practices from experienced program managers. Covers ROI, hunter interactions, and lessons learned for effective implementation and management.
Return of the Insecure Brazilian Voting Machines
Análise detalhada da segurança do software de votação brasileiro, baseada em resultados de um desafio de hacking restrito organizado pela autoridade eleitoral nacional.
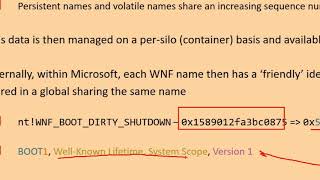
Windows Notification Facility - Peeling the Onion of the Most Undocumented Kernel Attack Surface Yet
Explore the undocumented Windows Notification Facility, its architecture, and potential security implications. Learn about state names, data publishing, and consuming, as well as attack vectors and defensive strategies.
Hey Google, Activate Spyware! - When Google Assistant Uses a Vulnerability as a Feature
Explore Android vulnerabilities allowing unauthorized camera control, revealing security flaws in Google Assistant and discussing implications for user privacy and smartphone security.
Preloading Insecurity in Your Electron
Explore vulnerabilities in Electron-based apps, focusing on BrowserWindow preload as an attack surface. Learn how XSS can lead to RCE and discover security implications for developers.
Ransomware Unlocked
Comprehensive overview of ransomware, including history, current attacks, hacker groups, and defense strategies. Explores cyber security frameworks and principles for effective recovery and protection.
Exploiting XPC in AntiVirus Software
Explore vulnerabilities in macOS antivirus software through XPC exploitation, uncovering security flaws and providing guidance for developers to create secure XPC services.
Rage Against the IDOR's - Using Machine Learning Models to Detect and Stop Authorization Bypass Vulnerabilities
Explore ML techniques to detect and prevent authorization bypass vulnerabilities in web applications, focusing on successful attacks and minimizing false positives.
Introducing the ASVS 4.0
Explore OWASP ASVS 4.0 updates, new controls, and industry applications. Learn about modern web app security, architecture changes, and a novel attack technique.
Attacking the Data Before the Decision
Explore AI's impact on stock market manipulation, machine learning models, and data security in financial trading systems.
How I Learned Docker Security the Hard Way - So You Don’t Have To
Practical insights on securing Docker containers, from architecture to incident response. Learn threat modeling, attacker techniques, and best practices for DevOps security.
Coding Secure Code - Best Practices, Advice for Writing Secure Code
Discover best practices for writing secure code, focusing on business-driven approaches, understanding your model, and integrating security seamlessly into development processes.
Cheaper by the Dozen - Application Security on a Limited Budget
Discover cost-effective application security strategies using open-source tools. Learn to implement OWASP projects, assess risks, and create a robust security program tailored to your organization's needs and budget constraints.
Container Security at the Speed of CI/CD
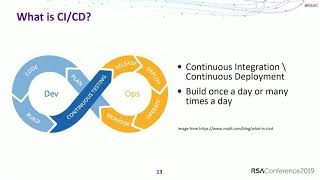
Explore container security challenges and learn to implement an automated solution that integrates with CI/CD pipelines, addressing application, code, web server, and host security.
Same Thing We Do Every Few Minutes, Pinky - Try to Take Over All Your Subdomains!
Explore subdomain takeover vulnerabilities and learn prevention strategies, including education, detection, and hardening techniques, based on Starbucks' experience and solutions.
When Application Security - The Wrong Way - Is the Right Thing for Your Organization
Discover innovative approaches to application security, including a "credit score" system, an exclusive security champions program, and improved scanning techniques for large-scale IT environments.