Down the Rabbit Hole - A Journey Towards a Weakness in Chrome and a New Hacking Technique
Explore a journey from CRLF injection to discovering Chrome vulnerabilities and a new XSS-like technique called Frontjacking, bypassing existing web security defenses.
0Day Up Your Sleeve - Attacking macOS Environments
Comprehensive guide to macOS security vulnerabilities, including live demonstration of 0-day exploit, post-exploitation techniques, and hardening recommendations for Mac infrastructures.
AppSec’s Future and the Rise of the Chief Product Security Officer
Explore the evolution of application security and the emerging role of Chief Product Security Officers in addressing modern digital infrastructure challenges.
DevSecOps State of the Union
Comprehensive overview of DevSecOps trends, best practices, and tools, distilling insights from industry experts and mature security programs for practical implementation.
Security Learns to Sprint - DevSecOps
Explore how DevOps can revolutionize application security by integrating it into daily development and operations workflows, enabling faster and more secure software delivery.
Caught My WebApp Cheating on Me
Exploring techniques to detect and prevent client-side injections and tampering in web applications, ensuring integrity and security of code executed in the browser.
How to 10X Your Company's Security - Without a Series D
Discover actionable strategies to dramatically enhance your company's security posture without significant financial investment. Learn from distilled insights and lessons from DevSecOps and modern AppSec experts.
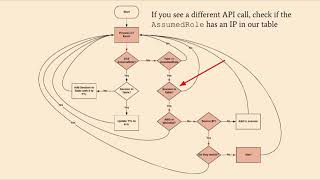
DevSecOps State of the Union
Comprehensive overview of DevSecOps best practices, tools, and methodologies. Distills insights from industry leaders to help AppSec teams improve security integration, automation, and culture.
How to Build an Application Security Program
Practical insights on creating and improving application security programs, drawing from 20 years of experience across various sectors. Covers successful strategies and pitfalls to avoid.
Hey Google, Activate Spyware! When Google Assistant Uses a Vulnerability as a Feature
Uncover Android vulnerabilities allowing remote control of photos, videos, and location data without user knowledge. Learn how researchers chained weaknesses to create a rogue spy application.
The Power of Guardrails - How to Slash Your Risk of XSS in Half
Discover how secure code defaults can significantly reduce XSS vulnerabilities and elevate overall security. Learn strategies to implement effective guardrails and minimize recurring security risks.
An Evolving Era of Botnet Empires
Explore the evolution of botnet empires, their lifecycle, functions, and detection methods. Learn about famous botnets, takedown attempts, and manual analysis techniques.
Why Security-as-a-Feature Will Never Happen
Explore why secure coding remains elusive, examining cultural issues, industry challenges, and potential solutions for integrating security into software development practices.
Serverless Infections - Malware Just Found a New Home
Explore serverless architecture vulnerabilities and learn how malware can exploit AWS Lambda functions, with insights on prevention and security best practices.
Federated Login CSRF
Explore federated login CSRF vulnerabilities in OpenID Connect and OAuth 2.0, examining attack scenarios, risks, and mitigation strategies for secure identity linking in web applications.
Fixing Broken Enterprise Threat Models with OWASP Efforts - Commissioning AppSec Professionals for Real Change
Explore how OWASP projects can revolutionize enterprise threat modeling, addressing compliance issues, undefined attack surfaces, and risk distortions to create measurable security impact.
Pushing Left Like A Boss - Application Security Foundations
Discover application security foundations and learn to 'push left' in the software development lifecycle. Explore strategies from vulnerability scanning to red team exercises for a proactive approach to security.
Creating an AppSec Pipeline With Containers in a Week - How We Failed and Succeeded
Explore the journey of implementing an AppSec pipeline using Docker containers, addressing challenges, solutions, and best practices for effective security integration in development workflows.
Practical Static Analysis for Continuous Application Security
Explore practical static analysis techniques for continuous application security, from simple grep to custom tools, enhancing software development lifecycle with targeted security checks.
Using Language-Theoretics and Runtime Visibility to Align AppSec with DevOps
Explore LANGSEC methodology and RASP tools for aligning AppSec with DevOps, enhancing runtime security visibility, and addressing vulnerabilities beyond traditional techniques.
Cleaning Your Applications' Dirty Laundry with Scumblr
Learn about Scumblr, an open-source tool for application security at scale. Discover how Netflix uses it for vulnerability management, risk tracking, and automating security tasks in a dynamic cloud environment.