Unprivileged Access Control in AppArmor
Explore AppArmor's extension for unprivileged access control, including challenges, changes, and API development for enhanced application security and sandboxing capabilities.
KubeArmor: Cloud-Native Runtime Security Enforcement
Explore KubeArmor: a runtime security system for cloud-native environments. Learn how it restricts pod, container, and node behavior using Linux security modules and generates rich alerts with eBPF.
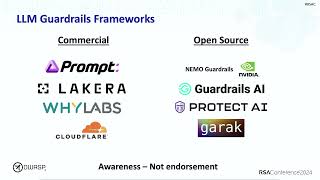
Securing AI Apps with the OWASP Top Ten for Large Language Models
Explore strategies to mitigate risks in generative AI using OWASP Top 10 for LLMs. Learn best practices for building secure and responsible AI applications in your environment.
Code Security Reinvented: Navigating the Era of AI
Explore AI's role in enhancing code security through GitHub Copilot, featuring practical demos and best practices for leveraging global security knowledge in software development.
Streamlining Falco Operations in Production with Falcoctl
Explore Falcoctl's capabilities for streamlining Falco operations in production environments, enhancing security and efficiency in cloud-native systems.
Memory Armor for SPIRE - Fortifying with Confidential Containers
Explore enhancing SPIRE security with Confidential Containers, protecting sensitive data in memory from potential attacks and adding an extra layer of defense to your cloud-native infrastructure.
Sandboxing in Linux with Zero Lines of Code
Explore Linux seccomp for process sandboxing without coding. Learn fine-grained controls, performance benefits, and approaches to easily secure applications in any programming language.
Security Showdown: The Overconfident Operator vs the Nefarious Ne'er-Do-Well
Playful demo showcasing cloud-native security concepts through characters Ozzie and Nova, exploring vulnerabilities and proactive measures for robust cluster protection.
Encrypted File System for Rust and Android Applications - Rust Zürisee 2023
Explore encrypted file systems for Rust/Android apps, focusing on multi-key secret handling, virtual file systems, and device synchronization. Learn about application-level encryption and native integration.
Enhanced Security for Multi-Tenant Architectures: Key Components and Best Practices
Explore Zero-Trust architecture for securing multi-tenant Kubernetes clusters. Learn best practices, access control, network isolation, and runtime security to fortify against threats and breaches.
Leveraging AI to Better Understand Your Environment - ODFP315
Explore how AI enhances MXDR services, providing deeper insights into organizational ecosystems, enabling proactive security measures, and optimizing Microsoft Defender for improved threat prevention.
Deep Dive into Open Policy Administration Layer (OPAL) - Authorization in Software
Explore advanced authorization with OPAL, covering the shift from RBAC to ABAC, policy-based systems, and decoupling authorization from code for improved security and efficiency.
Securing AI and LLM-based Applications: Best Practices
Explore security challenges in AI and LLM applications, learn attack scenarios, and discover best practices for mitigating risks and maintaining application integrity.
Secure LLM App Deployments - Strategies and Tactics
Discover strategies for enhancing LLM security using red-teaming techniques and Giskard's tools for automatic vulnerability detection in Generative AI applications.

LVBS and Advanced Kernel Integrity
Explore advanced Linux Virtualization based Security (LVBS) features for enhanced kernel integrity. Learn about hardening techniques to protect against unauthorized modifications, even in compromised environments.
From Text to Flaws: Vulnerabilities in Applications with Generative AI and LLMs
Explore vulnerabilities in generative AI applications, understand LLM functionality, and learn practical countermeasures to protect your AI-powered software from potential attacks.
Security Technology Arms Race 2021 - Medal Event
Explore the evolving security landscape, examining offensive and defensive strategies, technological breakthroughs, and future trends in cybersecurity. Gain insights into the ongoing arms race between attackers and defenders.
Adventures in Building a CAN Bus Sniffer
Explore the process of building a CAN Bus Sniffer, from prototyping to assembly. Learn hardware development tips, documentation preparation, and small-batch ordering for your first device.
Guardians of GitHub
Explore GitHub security practices and learn to protect your repositories from common vulnerabilities with insights from industry experts.
Securing and Trusting Third-Party Javascripts in Your Web App
Learn techniques to secure and trust third-party JavaScript in web applications, enhancing overall security and mitigating potential vulnerabilities.
How to Harden Your Electron App
Learn techniques to enhance security in Electron apps, focusing on threat modeling, separation of concerns, and best practices. Discover insights from building a secure password manager using this framework.