The Software Security Testing Lifecycle - A Framework for Effective Security Testing
Comprehensive framework for integrating security testing throughout development, empowering teams to identify threats early and validate controls effectively.
Bridging GDPR from Application to Cloud - 2018
Explore strategies to ensure GDPR compliance across applications and cloud infrastructure, addressing common challenges and implementing best practices for effective data protection.
Securing Legacy Applications: Tips and Tricks for Refactoring
Discover and fix security issues in legacy applications with practical tips and tricks. Learn to identify common vulnerabilities and refactor code for enhanced security.
Realizing Software Security Maturity - The Growing Pains and Gains
Explore the challenges and opportunities of implementing a comprehensive application security program using the Software Assurance Maturity Model (SAMM) to guide success beyond basic OWASP Top 10 compliance.
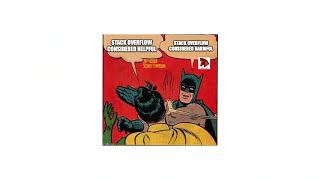
Stack Overflow: A Story of Two Security Tales - Enhancing Software Security
Exploring Stack Overflow's dual impact on software security: potential vulnerabilities and effective solutions. Highlights research findings and proposes design tweaks to enhance secure development practices.
Security Instrumentation - The Future of Software Security
Explore security instrumentation as a revolutionary approach to enhance software security, offering dynamic capabilities like intrusion detection, SBOM reporting, and runtime protection without code changes.
Security Code Analysis is for Everyone - 2019
Learn proactive approaches to identify and fix software vulnerabilities using Security Code Analysis, addressing complex applications and diverse development environments.
Living in AppSec - Promised, Fantasy, or Wonderland? - 2019
Explore GitHub's AppSec practices, successes, and ongoing challenges in creating an ideal security environment for application development.
Modern Approaches to Application Security - Purple Team Strategies
Explore modern application security combining offense, defense, automation, and continuous learning for developers. Learn how 'Purple Team' approaches can create more effective and affordable security models.
The End of the AppSec Team - Future of Application Security
Explore the future of application security, challenging traditional team structures and proposing innovative approaches to address the growing demand for AppSec professionals in software development.
AppSec at a Startup - Year Zero
Learn strategies for building an effective application security program at a startup, including developer engagement, automation, and rapid security improvements for SaaS companies.
How to Put Security in DevOps - 2017
Integrating security into DevOps: overcoming obstacles, enabling automation, and reaping benefits. Learn strategies for seamless AppSec implementation in continuous delivery environments.
Using Identity to Evolve Application Security - 2017
Explore how identity-based approaches can revolutionize application security, enhancing protection against modern threats and improving user experience.
OWASP Top 10 Training - Part 3
Comprehensive exploration of OWASP Top 10 security vulnerabilities, focusing on prevention strategies and best practices for web application security.
Trusted Execution: A Deterministic Approach to AppSec for Zero-Day Threat Prevention - 2016
Explore Trusted Execution, a novel approach to application security that promises zero-day threat prevention through granular memory-level visibility and context, eliminating false positives in advanced security threats.
Mind the CSP Gap: Challenges Developing a Meaningful Content-Security-Policy
Strategies for implementing Content Security Policy (CSP) effectively, addressing challenges and phasing in a meaningful policy without disrupting engineering teams.
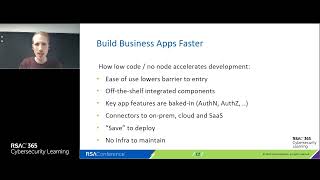
OWASP Top 10 Security Risks for Low-Code/No-Code
Explore security vulnerabilities in low-code/no-code apps, learn about the OWASP Top 10 list, and gain insights from real-world examples to enhance application security in modern development environments.
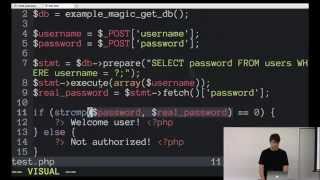
Input Sanitization - Peter Faiman
Learn essential techniques for validating user input, protecting against common vulnerabilities, and developing a security-focused mindset to safeguard your applications from malicious or unintended user actions.
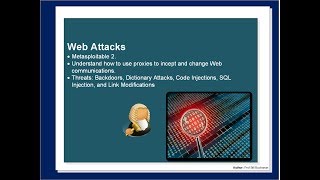
Web Attacks
Explore common web vulnerabilities and attack methods, including discovery techniques, backdoors, weak passwords, and injection attacks, to enhance your cybersecurity knowledge.
Data Loss Prevention: Databases and Web Security
Explore web vulnerabilities, SQL injection, and database security techniques to enhance your cybersecurity skills and protect against data loss.

Learn to Hack Live - Command Injection
Explore command injection vulnerabilities in web applications through live hacking demonstrations and hands-on exercises. Enhance your penetration testing and application security skills.