Microservices Security Pattern in Kubernetes - East-West Traffic
Explore sidecar patterns and policies for securing APIs and apps in Kubernetes, featuring expert insights and a live hacking demo to enhance service security and resilience.

Secure Multi-Cluster & Multi-Tenant Cloud Native Apps with Mirantis & Tetrate
Explore secure multi-cluster, multi-tenant cloud-native app management using Mirantis Container Cloud and Tetrate Service Bridge for centralized policy control and efficient deployment across various infrastructures.

Spring Security Tutorial - NEW - 2022
Learn to implement Spring Security with basic auth and JWT in this comprehensive tutorial, covering setup, authentication methods, and practical application testing.
Automating Zero-Trust for Cloud Native Applications
探索如何为云原生应用实施自动化零信任策略,包括创建策略、集成到部署流程和自动化测试,使用开源技术提高应用安全性。
Seguridad de Aplicaciones en Ubuntu - Fundamentos y Mejores Prácticas
Explora los fundamentos de seguridad en Ubuntu, desde arquitectura hasta actualizaciones, con expertos argentinos. Aprende mejores prácticas para proteger aplicaciones y fortalecer tu comprensión.
Race Conditions in Cybersecurity - The Hare and Tortoise Fable
Explora las vulnerabilidades de "race condition" en aplicaciones, su detección y explotación para manipular la lógica y evadir límites. Incluye demostraciones en vivo y ejemplos prácticos de penetration tests.
DevSecOps Endgame: Threat Modeling as a Game - Workshop
Taller interactivo sobre modelado de amenazas en DevSecOps. Aprende técnicas prácticas para identificar vulnerabilidades, evaluar riesgos y desarrollar aplicaciones más seguras de forma divertida y dinámica.
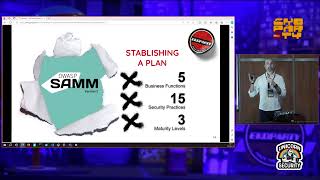
OWASP SAMM Approach: Creating Secure Applications from Scratch
Explora el Modelo de Madurez de Seguridad de Aplicaciones de OWASP (SAMM), una metodología para crear aplicaciones seguras desde la planificación hasta el mantenimiento continuo.
Identificando y Mitigando Amenazas de Seguridad en Aplicaciones Linux con Threat Modeling
Aprende a identificar y mitigar amenazas de seguridad en aplicaciones Linux mediante Threat modeling, enfocado en snaps y debs para Ubuntu y Ubuntu Core. Explora estrategias de protección y mejores prácticas.
Implementando Aplicativos em um Ambiente Seguro com Terraform, Trivy e Postee
Aprenda a implementar aplicativos de forma segura usando Terraform para automação de infraestrutura e ferramentas como Trivy e Postee para identificar e corrigir vulnerabilidades em contêineres.
[Portuguese] 30 Segundos de Senhas - Automatizando o Rotacionamento de Senhas em Ambiente Kubernetes
Automatize o rotacionamento de senhas em ambientes Kubernetes para mitigar vazamentos de credenciais de banco de dados, utilizando infraestruturas modernas e cofres de senha para controle do ciclo de vida.
Desvendando Application Security - Proteção de Software no Ciclo de Desenvolvimento
Explore o processo de segurança de aplicações para proteger software durante seu desenvolvimento. Aprenda a implementar medidas, realizar testes e monitorar ameaças para aumentar a resiliência.
Compositional Security for Reentrant Applications
Explore reentrant applications' security, focusing on locking integrity and data protection. Learn about static vs dynamic locks and effective approaches to enhance compositional security.
Serverless Top 10 Vulnerabilities by Tal Melamed
Explore serverless security vulnerabilities, their impact, and prevention techniques. Learn how traditional threats evolve in serverless environments and discover best practices for securing cloud-native applications.
Back to Basics - Application Security Practices in Smart Contract Auditing
Explore application security practices in smart contract auditing, focusing on Solidity, common vulnerabilities, security tools, and the growing market for blockchain security engineers.
Bug Bounty Hunting Methodology - Jason Haddix from Bugcrowd's LevelUp
Comprehensive web hacking methodology covering reconnaissance, scanning, and exploitation techniques for bug bounty hunters and security researchers.
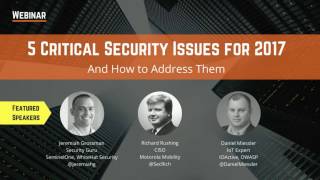
Critical Security Issues and Trends for 2017
Explore critical security trends with industry experts, covering IoT vulnerabilities, crowdsourced testing, AI impacts, and evolving threats to prepare for the cybersecurity landscape of 2017.
FAIR STRIDE - Building Business Relevant AppSec Threat Models
Integrating FAIR and STRIDE methodologies to create business-relevant application security threat models, translating technical risks into financial impacts for strategic decision-making.
Making End User AppSec Training Engaging with Building Bricks
Innovative approach to AppSec training using LEGO minifigures and custom builds to enhance retention. Covers key security concepts with creative visual metaphors for better engagement and understanding.
Climbing AppSec Mountains - How to Summit and Overcome Corporate Roadblocks
Explore strategies for overcoming corporate roadblocks in application security, focusing on early involvement in the software development lifecycle to prevent vulnerabilities and improve software quality.

Introduction to Inner-Loop Security - Shifting Left, but Better
Explore inner-loop security as the next evolution of "shift left," enabling developers to build secure-by-design products through improved methodologies and tools.