Dev Ally, Zero-Days Foe - DefCamp Cluj-Napoca 2024
Explore cutting-edge cybersecurity insights with Ali Abdollahi's presentation on developer-friendly approaches to combat zero-day vulnerabilities at DefCamp Cluj-Napoca 2024.

Writing Viruses for Fun, Not Profit
Explore virus creation techniques, including self-replication and obfuscation, to understand how they evade detection and infect systems. Learn to anticipate vulnerabilities and strengthen application security.
Everything-as-Code: Pushing the Boundaries of SAST
Explore the evolution of SAST in the "everything as code" era, examining challenges in analyzing infrastructure, contracts, and circuits, with focus on Bicep and Solidity languages.
Zero Trust Threat Modeling - Implications for Application Security
Explore zero trust's impact on application security and threat modeling. Learn new design principles, threats, and approaches for effective zero trust threat modeling in modern environments.
Scaling Content Security Policy: Enterprise Compliance and Third-Party Resource Management
Learn to implement Content Security Policy and monitor web resources at scale, addressing supply chain attacks and PCI requirements for enhanced frontend security in enterprise applications.
Attacking Developer Environments Through Drive-by Localhost Attacks
Explore drive-by localhost attacks on developer environments, uncovering vulnerabilities and defense strategies in this cybersecurity presentation from DefCamp 2023.
Finding Vulnerabilities in Your Codebase Using Open Source Tools
Explore open-source tools for identifying vulnerabilities in your codebase. Learn effective techniques to enhance software security and protect against potential threats.
AppSec Contractual Sins - Identifying and Addressing Security Issues in Contracts
Explore common AppSec contractual pitfalls and best practices for securing software development agreements in this DefCamp 2023 presentation by Canon's EMEA Information Security Manager.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security strategies for new technologies, emphasizing the importance of product security in today's cyber landscape and the need for innovative, affordable approaches.
The Past, Present, and Future of Cross-Site and Cross-Origin Request Forgery
Explore the evolution of Cross-Site Request Forgery attacks, their impact on applications, and effective defense strategies. Learn about vulnerabilities in API-based systems and best practices to prevent CSRF.

OWASP Juice Shop - An Open Source Software and Security Fairytale
Explore the evolution of OWASP Juice Shop, a pioneering hacking training platform, from its inception as a pet project to becoming an OWASP Flagship project, with insights into its future developments.
Beyond the Firewall - Ensuring OT Application Security
Explore OT application security principles, including IAM, secure development environments, secure coding for PLCs, and change detection strategies to enhance your operational technology security posture.
AppSec Tool Selection, Procurement, and Implementation Walkthrough
Comprehensive guide to selecting, procuring, and implementing Application Security tools in the SSDLC, offering strategies for successful integration and follow-through.
Day in the Life of an Ethical Hacker and Penetration Tester
Explore the daily routine of an ethical hacker, uncovering the exciting and challenging aspects of penetration testing. Gain insights into this dynamic cybersecurity career path.
Building Trusted Systems on Top of Leaky Abstractions
Exploring secure system design in complex tech stacks. Covers side-channel attacks, browser security, and trusted execution environments. Insights on building robust systems against known and unknown threats.
AppSec Wingman for Copilot in VS Code - Secure AI-Generated Code Recommendations
Discover how Veracode's AI-powered extension for VS Code enhances Copilot, offering secure code recommendations to fix vulnerabilities based on insights from scanning trillions of code lines.
Security Is Key - The Vulnerabilities of API Security
Explore API security vulnerabilities and learn essential strategies to protect your systems from potential threats in this informative talk by Joe Wrieden.
Mastering Web Security - Myths, Strategies and Best Practices
Debunking web security myths and exploring effective defense strategies. Experts share practical tips, valuable resources, and emphasize organizational commitment for robust application security.
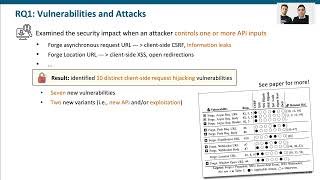
The Great Request Robbery
Explore web security vulnerabilities and attack techniques with a focus on request forgery and injection flaws in modern applications.
DevSecOps Insights and Exciting Horizons
Explore DevSecOps trends and future strategies with RSAC 2024 Program Committee members, discussing standout sessions and emerging cybersecurity approaches.
Debugging Schrodinger's App - DevSecOps Strategies
Explore quantum computing principles applied to debugging complex software systems, enhancing problem-solving skills for modern developers.