Don't Let Bug Bounty Kill Your AppSec Posture
Explore strategies to maintain a robust application security posture while leveraging bug bounty programs effectively in this insightful conference talk.
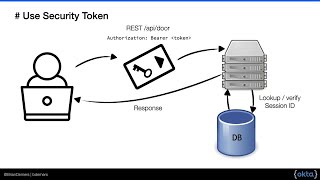
Security Tokens - Understanding JWTs, Macaroons, and PASETOs
Explore security tokens like JWTs, Macaroons, and PASETOs. Learn their benefits, usage, and potential vulnerabilities in mobile and web applications. Gain insights on choosing the right token for your project.
An Introduction to PASETO - Understanding Platform Agnostic Security Tokens
Discover PASETO tokens, a simpler and more secure alternative to JWTs. Learn how they work, their advantages, and how to implement them in your applications for improved web authentication.
Shifting Security from Right to Left
Discover how to integrate security into your development workflow using Snyk's tools in IntelliJ IDEA, enabling early detection and remediation of vulnerabilities in project dependencies.
Hands-on Introduction to Snyk - Security Scanning for Dependencies, Code, and Containers
Comprehensive introduction to Snyk, covering dependency security, code analysis, container scanning, and Kubernetes YAML scanning. Hands-on demonstration of Snyk's features for identifying and addressing vulnerabilities.
Insecurity in Information Technology - Impact on Application Security
Explore how personal insecurities and workplace dynamics impact software security. Learn strategies to improve collaboration between developers and security teams for better outcomes.
The Abridged History of Application Security
Explore the evolution of application security from the 1960s to present, highlighting improvements and inspiring security professionals with a historical perspective on industry progress.
Build More Secure Apps with OWASP SKF and ASVS on Kubernetes
Enhance app security using OWASP SKF & ASVS on Kubernetes. Learn integration, manage ASVS requirements, and explore SKF Labs. Includes demo and GitHub repo for easy deployment on EC2 or AWS.
Using API Specifications to Attack APIs
Explore API security vulnerabilities, breaches, and scanning tools. Learn to leverage API specifications for both protection and potential exploitation in this comprehensive overview.
Knowing What Risks Matter and Don't in Your Open Source
Explore key findings on open-source software risks, including usage trends, vulnerability rates, and best practices. Learn to prioritize and address critical issues in application security.
Towards Intelligent Application Security
Exploring the evolution of application security and proposing an automated approach integrating security into development and operations, aided by learning techniques and threat intelligence.
Hook, Line, and Tinker: A Dive into Phishing Campaign Sites
Explore phishing cases, learn active reconnaissance techniques, and discover how to disrupt attackers and identify security gaps with an AppSec engineer's insights and triage process.
Securing Digital Frontiers: Leveraging Keycloak for Comprehensive Application Security
Explore Red Hat's Keycloak for robust identity and access management in diverse deployment environments, ensuring application security and mitigating financial risks.
Secure Your App: DevSecOps Trusted Application Supply Chain
Explore DevSecOps principles and implement a trusted application supply chain to enhance app security and streamline development processes.
Rollout Hardcoded Secrets Detection with Minimum Effort and Maximum Impact
Learn effective strategies for detecting hardcoded secrets in your codebase, minimizing effort while maximizing impact on security and compliance.
Designing Security and Privacy - A Developer's Guide to Threat Modeling with OWASP SAMM
Learn threat modeling techniques using OWASP SAMM to enhance security and privacy in software development, empowering developers to identify and mitigate potential risks effectively.
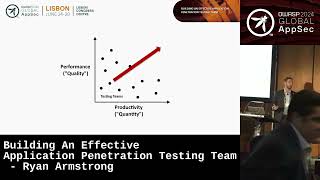
Building an Effective Application Penetration Testing Team
Discover strategies for assembling and leading a high-performing application security testing team, enhancing your organization's defense against cyber threats.
Code Red: Navigating the Minefield of Security Programming Blunders
Explore infamous security breaches, learn from programming mishaps, and gain practical strategies to enhance cybersecurity in this dynamic session on secure coding practices.
OWASP SAMM - Interactive Introduction and Update
Explore OWASP SAMM, a framework for software assurance maturity modeling, with interactive insights and updates from industry experts.
Modern Application Security vs. GenAI Applications: Is Your AppSec Ready?
Explore the intersection of modern application security and generative AI, assessing readiness for emerging challenges in the evolving tech landscape.
5 AppSec Stories and What We Can Learn From Them
Explore real-world application security incidents and extract valuable lessons to enhance your cybersecurity practices and prevent similar vulnerabilities in your own systems.