API Authentication's Poorly Implemented - Security Issues in Web APIs
Explore real-world API security issues, focusing on authentication and authorization problems across various platforms. Learn from examples ranging from online payment systems to embedded device infrastructures.
AppSec is Eating Security - The Future of Information Security
Explore the future of application security with insights on containerization, hardware security, and user-centric approaches. Learn about emerging trends and strategies for building safer digital ecosystems.
New Frameworks, Old Problems: Web Security Challenges in Modern Development
Exploring security challenges in modern web frameworks like Play! and Node.js, comparing solutions from established frameworks, and offering practical code examples to address common vulnerabilities.
Android and iPhone Risks and Solutions
Explore mobile security risks and effective solutions for Android and iPhone devices, enhancing your understanding of smartphone vulnerabilities and protection strategies.
Application Security at DevOps Speed and Portfolio Scale
Explore a revolutionary approach to application security using passive sensors for real-time visibility across an organization's portfolio, enabling proactive collaboration and value generation.
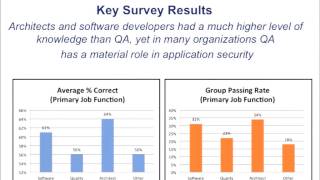
Can AppSec Training Really Make Developers Security-Smart?
Explore the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and practical application in software security programs.
Next Generation Red Teaming - Integrating Application-Centric Attacks
Explore advanced red teaming techniques integrating application-specific attack surfaces for more realistic and effective security assessments across multiple domains.
Can AppSec Training Really Make a Smarter Developer?
Explores the effectiveness of AppSec training for developers through a year-long survey, revealing surprising insights on knowledge retention and its impact on application security strategies.
The Practice and Implementation of DevSecOps
Explore DevSecOps implementation, covering SAST, DAST, IAST, training tools, and maturity models. Learn best practices for integrating security into the development lifecycle.
Developing Secure Open Source Software - Mentorship Session
Explore best practices for developing secure open source software with expert guidance on risk mitigation, vulnerability management, and collaborative security measures.
Improving Unmodified Classic Application Confinement
Explore techniques for enhancing application security through sandboxing, focusing on unmodified classic apps. Learn about policy updates, tagging, and dynamic policy composition.
Shifting Application Security Left: Practical Steps to Get There
Explore practical steps to integrate automated security testing into software delivery pipelines, enabling efficient and secure development practices for modern engineering teams.
Leveraging OpenZiti to Embed Zero Trust Directly Into Applications
Explore OpenZiti's toolset for embedding zero trust into applications, learning core tenets of zero trust environments and understanding its implementation in modern software development.
5 Open Source Security Tools All Developers Should Know About
Discover five essential open-source security tools for developers, enhancing code safety and vulnerability detection in your projects.
Designing Secure Containerized Applications for Embedded Linux Devices
Learn to design secure containerized applications for embedded Linux systems, focusing on best practices and techniques for enhanced security and efficiency.
Realities of SBOM - What Is Under the Hood of Software Bill of Materials
Explore the complexities of Software Bill of Materials (SBOM) beyond dependency files, including interdependencies, integrity, and vulnerability monitoring across the software development lifecycle.
SLSA in Action: Securing the Software Supply Chain
Live demonstration of securing software supply chain and achieving SLSA compliance using sample repo. OpenSSF SLSA group showcases tooling developed to meet SLSA 1.0 Build Specification, offering practical insights into implementation.
Supply Chain Security: From Infrastructure to Application, Code to Cloud
Explore best practices for securing the entire software supply chain, from infrastructure to application, covering code, cloud, dependencies, and deployment.
Designing Secure Containerized Applications for Embedded Linux Devices
Learn to design secure containerized applications for embedded Linux, covering container infrastructure, image security, execution security, and best practices.
Protect Your Application, Not the Network - Adding Zero Trust Superpowers to Critical Applications and Systems
Discover how to implement Zero Trust security principles to safeguard critical applications and systems, enhancing protection beyond traditional network-based approaches.
Security as Code: A DevSecOps Approach
Explore DevSecOps and Security as Code principles, focusing on SQL injection prevention and vulnerability analysis using Code2LV and data flow techniques.