OWASP Hackademic - Teaching Application Security Through Practical Challenges
Practical environment for teaching application security through realistic scenarios with known vulnerabilities. Students discover and exploit vulnerabilities, gaining hands-on experience from an attacker's perspective.
Mobile Security Attacks - A Glimpse from the Trenches
Explore emerging mobile security threats, from physical to network and application levels, with real-world attack examples and insights from experts who uncovered iOS vulnerabilities.
OWASP A9: Using Components with Known Vulnerabilities - A Year Later
Explore real-world case studies and industry trends on managing component vulnerabilities in applications, with insights on best practices and challenges in following OWASP A9 guidelines.
Dynamic Source-Sink Analysis for Java Applications - From the Ground Up
Dynamic source-sink analysis for Java applications to detect security vulnerabilities, aimed at developers for use during development, not production. Demonstrates live detection of issues like log manipulation.
Stop Chasing Vulnerabilities - Introducing Continuous Application Security
Explore continuous application security strategies using open-source tools for real-time monitoring and analytics, shifting focus from individual vulnerabilities to comprehensive portfolio-wide assurance.
Threat Modeling Made Interactive - Using Poirot for Dynamic Security Analysis
Interactive demonstration of Poirot, a tool for modeling and analyzing system security during design phase, enabling real-time threat assessment and mitigation strategies.
Hacking .NET Applications - The Black Arts of ASM Attacks
Explore new tools and techniques for attacking .NET applications in live memory, enabling easy point-and-click attacks on critical software components with basic skills and free tools.
11,000 Voices - Experts Shed Light on 4-Year Open Source and AppSec Survey
Experts discuss findings from a 4-year study on open source security practices, revealing surprising trends in policy enforcement, vulnerability tracking, and organizational preparedness for security threats like Heartbleed.
AppSec Training Program Fine-Tuning Based on Survey Data - OWASP AppSecUSA 2014
Explore data-driven insights on AppSec training effectiveness, developer awareness, and learning preferences to optimize security programs and enhance defensive coding practices.
Building Your Application Security Data Hub - The Imperative for Structured Vulnerability Information
Learn how to create an integrated application security program by breaking down silos, enabling data flow between teams and tools, and implementing metrics to measure performance and improvement.
AppSecUSA 2014 Builders Track - Friday Sessions
Explore key AppSec topics: mobile security, threat modeling, continuous security, and component vulnerabilities. Gain insights from industry experts to enhance your application security practices.
BSIMM: A Decade of Software Security Evolution - Keynote
Explore the evolution of software security over a decade, from early concepts to modern practices, highlighting the BSIMM framework for measuring and improving security initiatives in software development.
Application Security Management Strategies - OWASP AppSecUSA 2014
Explore key AppSec topics: structured vulnerability data, training programs, open source surveys, lean security for SMBs, and adaptive strategies. Gain insights from industry experts at OWASP's AppSecUSA 2014.
AppSecUSA 2014 - Breakers Track Sessions
Explore cutting-edge web and mobile security topics, including mobile attacks, use-after-free exploitation, static analysis, runtime manipulation, and top hacking techniques from AppSecUSA 2014.

Making Content Security Policy Work For You
Learn about Content Security Policy (CSP), its importance in web application defense, and practical tips for implementation from Mozilla's application security expert.
Continuous Security Testing in DevOps Environments
Explore continuous security testing in DevOps, addressing challenges and presenting an open-source framework using Behavior Driven Development for effective communication and automation.
Reflections on Scoping Trust in Modern Web Environments
Reflections on trust in the modern web environment, examining gaps in current models and exploring ways to create a more trustworthy internet ecosystem without total self-reliance.
Leveling Up an Application Security Program
David Rook shares insights on enhancing application security at Riot Games, covering assessment, implementation of controls, secure coding guidance, and maintaining a security community in a fast-paced environment.
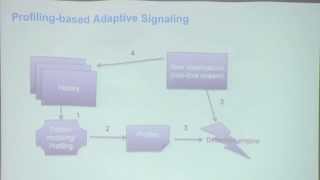
Devil in the Haystack - Application Security Through Statistical Analysis and Machine Learning
Exploring statistical and machine learning techniques for in-app security at Salesforce. Focuses on adaptive, data-driven approaches for detecting and preventing attacks and abuses on the platform.
AppSec is Eating Security
Explore the future of information security with Yahoo's CISO Alex Stamos as he discusses the evolving landscape of application security and its impact on the broader security field.
Fix the Damned Software - Improving Application Security Design
Explore strategies for building security into software development, moving beyond vulnerability discovery to secure design and implementation. Learn from industry experience and BSIMM data.