Leveling Up Your Application Security Program
Learn strategies to enhance your organization's application security program, focusing on key improvements and best practices for robust cybersecurity.
Don't Touch Me That Way - Mobile Application Security Best Practices
Explore secure mobile app development strategies and best practices to protect against common vulnerabilities and attacks in this insightful OWASP conference talk.
Using JIRA to Manage Risks and Security Champions Activities
Learn how to effectively manage risks and security champion activities using JIRA, enhancing your organization's application security practices and workflows.
Framework Security: Hugging Developers Through Self-Defending Systems - AppSecEU 2016
Explore framework security strategies, self-defending frameworks, and developer-friendly approaches to enhance application security without code changes or performance impact.
Hardening the Web Platform
Explore web platform security with Mike West's keynote on hardening techniques, challenges, and future directions for a more robust online environment.
Practical Threat Modeling with Microsoft's Threat Modeling Tool 2016
Learn practical threat modeling using Microsoft's Threat Modeling Tool 2016. Explore data flow-based techniques, risk assessment, and countermeasures for effective application security.
SAASY SPLC - Secure Application Architecture for Software Product Line Configurations
Explore secure software development lifecycle practices for SaaS applications, focusing on unique challenges and effective strategies in cloud-based environments.
Idiot Proof Is Not Enough: Make It Villain Proof - Application Security
Learn strategies to secure applications against sophisticated attackers, going beyond basic safeguards to create robust, villain-proof systems.
Grow Up AppSec - A Case Study of Maturity Models and Metrics
Explore a case study on application security maturity models and metrics, focusing on growth strategies and practical insights for improving organizational security posture.
Everything You Need to Know About Certificate Pinning - AppSecEU 2016
Comprehensive guide to certificate pinning: implementation, benefits, and potential pitfalls. Essential knowledge for enhancing mobile app security and protecting against man-in-the-middle attacks.
Implementing a Supply Chain Approach to Build and Deploy Secure Applications - AppSecEU 2016
Explore implementing a supply chain approach to build and deploy secure software, focusing on trust, standardization, and automation in the software delivery pipeline.
Opening Ceremony - AppSec EU 2015
Opening ceremony of AppSecEU 2015 in Amsterdam, featuring Martin Knobloch and Tobias Gondrom. Highlights key aspects of the conference and sets the tone for upcoming discussions on application security.
The Top 10 Web Hacks of 2014 - AppSec EU 2015
Explore the most significant web security vulnerabilities of 2014, presented by industry experts. Gain insights into attack vectors and learn essential defense strategies.
Maliciously Monetizing AppSec Features - It's All About the Money
Explore malicious monetization of AppSec features with Or Katz and Ezra Caltum. Learn about potential security vulnerabilities and their financial implications in application development.
Issues and Limitations of Third Party Security Seals
Explore limitations of third-party security seals in web applications, uncovering potential vulnerabilities and discussing implications for online security practices.
AppSec EU 2015 Closing Ceremony
Closing remarks and highlights from AppSecEU 2015 in Amsterdam, covering key takeaways and future directions in application security.
The Software, Not the Human, Is the Weakest Link
Explore how software vulnerabilities, not human error, are the primary security risk in modern systems. Learn to shift focus from blaming users to improving code security.
Agile Security Testing - Lessons Learned
Explore agile security testing strategies, challenges, and best practices for efficient integration of security in software development, based on real-world experiences and lessons learned.
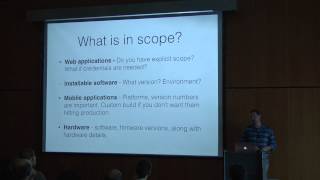
Hard Knock Lessons on Bug Bounties
Insights and lessons learned from managing bug bounty programs, covering legal aspects, scope definition, program structure, and reward strategies for effective vulnerability disclosure.
Copy Pest - A Case Study on the Clipboard, Blind Trust, and Invisible Cross-Application XSS
Explore clipboard vulnerabilities and cross-application XSS in this case study on invisible security threats and blind trust in web applications.
Security and Modern Software Deployment - AppSec EU 2015
Explore modern software deployment security challenges, including trust issues, dependencies, and repository vulnerabilities. Learn strategies to mitigate risks and enhance deployment security.