Making Security Agile in CI/CD Environments
Integrating security into agile development and CI/CD pipelines. Learn strategies to automate security processes, leverage QA tests, and utilize tools for improved productivity in application security.
Skillful, Scalable Full-Stack Security in a State of Constant Flux
Approaches to maintaining secure full-stack posture at scale in changing environments. Discusses automation vs. human testing, analytics in continuous security, and scaling with human validation and intelligence.
Advances in Secure Coding Frameworks
Explore positive advancements in application security frameworks, highlighting built-in security features that simplify secure coding for developers and improve overall software safety.
Benchmarking Application Security Across Industries
Insights from 200,000+ application assessments reveal industry-specific software security trends, vulnerabilities, and best practices. Benchmark your AppSec program against peers for improved security outcomes.

15 Years of Web Security - The Rebellious Teenage Years
Explore web security's evolution, challenges, and future trends with insights on threat modeling, vulnerability data, and emerging solutions like cyber insurance and security guarantees.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Serverless Security for DevOps and Defenders
Explore serverless architecture's impact on DevOps and security with James Wickett. Learn how this emerging technology enhances defense strategies and streamlines development processes.
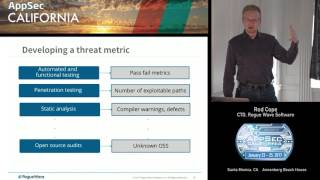
Continuous Security: Bringing Agility to the Secure Development Lifecycle
Bringing agility to secure development: Learn strategies for integrating continuous security practices into your development lifecycle, enhancing both speed and safety in software creation.
An SDLC for the DevSecOps Era
Explore an SDLC tailored for the DevSecOps era with insights on integrating security into modern development practices and organizational culture.
Why Using SMS in Authentication is Risky and Better Alternatives - AppSecUSA 2016
Explore limitations of SMS-based authentication and discover more secure alternatives using push notifications for improved user experience and enhanced security in two-factor authentication.
Containerizing Your Security Operations Center
Explore containerizing security operations for improved deployment, maintenance, and collaboration. Learn to build a cloud-based SOC using containers, enhancing visibility and streamlining security workflows.
Everything is Terrible: Building, Configuring, and Securing Software - Three Perspectives
Explore perspectives on building, configuring, and securing software from developers, operations, and security experts. Learn strategies for collaboration, empathy, and optimizing workflows across teams.
Women in Application Security - Challenges and Opportunities
Panel discussion featuring industry experts exploring challenges and opportunities for women in application security, highlighting diverse perspectives and experiences.
Continuous Acceleration: Why Continuous Everything Requires a Supply Chain Approach
Explore the need for a supply chain approach in continuous development practices, emphasizing acceleration and efficiency in modern software security and delivery processes.
Rise of the Machines - How Automated Processes Overtook the Web
Explore how automated processes have dominated web interactions, their impact on security, and strategies to protect against machine-driven threats in modern web environments.
Marshalling Pickles - How Deserializing Objects Can Ruin Your Day
Explore vulnerabilities in object serialization across languages, learn exploitation techniques for code execution, and discover protective strategies against deserialization attacks.
Building a Better Hacker to Improve Cybersecurity Defense
Explore how understanding hacker mentality bridges the gap between developers and security teams, leading to more effective cybersecurity strategies and proactive threat prevention.
Why Your AppSec Experts Are Killing You - Evolving to Continuous Application Security
Explore how to evolve into a "Continuous Application Security" organization using instrumentation-based testing, real-time feedback loops, and innovative tools for improved DevOps integration and portfolio-wide assurance.
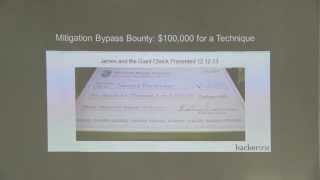
Bounties and the Software Development Life Cycle
Katie Moussouris explores bug bounties, vulnerability disclosure, and their integration into the software development lifecycle. She shares insights on organizational empathy, bounty program implementation, and improving application security.
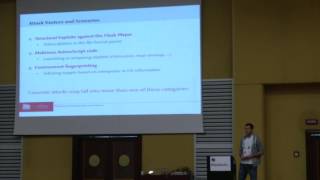
Analyzing and Detecting Flash-Based Malware
Explore techniques for analyzing and detecting Flash-based malware, enhancing your cybersecurity skills and understanding of this prevalent threat vector.
Addressing Security Requirements in Development Projects
Learn effective strategies for integrating security requirements into development projects, covering artifact creation, requirement generation, filtering, and customization.