Hacking Object Detectors Is Just Like Training Neural Networks
Explore techniques for deceiving object detectors by comparing the attack process to neural network training. Learn how applying training techniques can improve adversarial attacks on state-of-the-art systems.

Exploring Practical Vulnerabilities of Machine Learning-Based Wireless Systems
Unveils practical vulnerabilities in ML-based wireless systems through RAFA, a hardware-implemented adversarial attack platform, demonstrating significant performance drops in communication and sensing approaches.
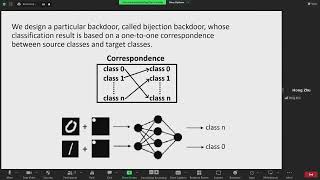
AI-Guardian - Defeating Adversarial Attacks Using Backdoors
Explore innovative techniques to counter adversarial attacks on AI systems using backdoor mechanisms, enhancing model robustness and security in critical applications.
Responsible AI for Business Leaders
Explore responsible AI practices, challenges, and Google's principles for ethical AI implementation in business. Learn strategies to mitigate risks and ensure positive outcomes in AI development.
Responsible AI for Engineers
Explore responsible AI practices, challenges, and solutions in this talk by Google's Technical Director. Learn about bias, unintended consequences, and techniques for aligning machine learning with ethical values.
Sleeping with One AI Open
Explore adversarial attacks on AI/ML systems, their real-world implications, and mitigation strategies. Learn about potential risks and security considerations in AI-driven technologies across various sectors.
Everything You Need to Know about Security Issues in Today's ML Systems
Comprehensive overview of security vulnerabilities in ML systems, covering poisoning, evasion, and inversion attacks, with focus on adversarial examples and their impact on various applications.
Defending Against Adversarial Model Attacks Using Kubeflow
Explore building robust AI pipelines against adversarial attacks using Kubeflow and LFAI Adversarial Robustness Toolbox. Learn to test ML model robustness in production with Kubeflow Serving and KNative eventing.
Information Leakage of Neural Networks
Explore information extraction attacks on machine learning models, their potential to compromise sensitive data, and strategies for mitigation. Gain insights into legal aspects and privacy-security-utility tensions.
Exploiting Voice Cloning in Adversarial Simulation - Security Testing and Defense Strategies
Explore the security vulnerabilities of voice verification systems through deep learning voice cloning techniques, including practical demonstrations, risk assessment, and defensive countermeasures.
Analyzing the Security of Machine Learning for Algorithmic Trading
Explore adversarial attacks on ML-based algorithmic trading systems, evaluating robustness and discussing realistic attack scenarios in financial markets.
Responsible AI: Challenges and Emerging Practices - Keynote
Explore challenges and emerging practices in responsible AI, including unintended consequences, model interpretability, fairness, and engineering objectives.
Analyzing and Exposing Vulnerabilities in Language Models - Session 131
Delve into advanced research on language model vulnerabilities, exploring novel adversarial attack methods and gender bias analysis while discovering practical approaches to enhance AI trustworthiness and fairness.
Deep Learning New Frontiers
Explore deep learning limitations and new frontiers, including expressivity, generalization, failure modes, uncertainty, adversarial attacks, and emerging areas like graph learning and AutoML.
Deep Learning New Frontiers
Explore deep learning limitations and new frontiers, including expressivity, generalization, adversarial attacks, uncertainty, and AutoML. Gain insights into cutting-edge developments in neural networks.
Some Pitfalls in AI
Explore common pitfalls in AI applications, including bias, adversarial attacks, ethics, and privacy concerns, to better understand the challenges and risks of autonomous decision-making systems.
Do Attackers Use Algorithms to Evade ML - An In-the-Wild Phishing Case Study
Explore phishing evasion tactics and trends, including 11 current techniques and potential use of automated adversarial attacks. Gain insights from a 5-year study on ML phish evasion competitions and real-world evasive phishing sites.
Breaking Fake Voice Detection with Speaker-Irrelative Features
Delve into advanced techniques for bypassing fake voice detection systems through Speaker-Irrelative Features, achieving over 80% success rate by manipulating background noise and mute segments.
Exploring Pillars of Trustworthy AI: Robustness and Fairness
Discover how to build robust and fair AI models by exploring vulnerabilities, implementing defense strategies, and addressing bias in machine learning systems through practical techniques.
Red Teaming Language Model Detectors with Language Models
Explore strategies to compromise LLM detectors using synonym replacement and instructional prompts, revealing vulnerabilities in text detection systems and emphasizing the need for robust safeguards.
Adversarial and Poisoning Attacks Against Speech Systems - Where to Find Them
Explore vulnerabilities in machine learning systems, focusing on poisoning and adversarial attacks. Learn strategies, defense mechanisms, and implications for AI security.