
SSRF PWNs - New Techniques and Stories
Découvrez de nouvelles techniques d'attaques SSRF, leurs impacts sur la sécurité des applications web et des exemples concrets d'exploitation, présentés par deux experts en sécurité informatique.
A Short History of the JavaScript Security Arsenal
Explore the evolution of JavaScript security tools and techniques over six years, from basic port scanners to advanced frameworks, with insights from expert Petko D. Petkov.
Zero-Day Exploits of Operation WizardOpium
Detailed analysis of zero-day exploits and watering-hole attacks in Operation WizardOpium, covering technical aspects, spreading methods, and security implications.
XSS Mitigation - The State of the Art
Comprehensive overview of XSS attacks and modern defense strategies, covering browser-based, server-side, and framework-specific mitigations for web developers and security professionals.
Building Identity for an Open Perimeter
Explore Netflix's cloud-first security approach, focusing on identity as the new perimeter through SSO, MFA, and adaptive authentication for a location-independent strategy.

Navigating Passwordless Authentication with FIDO2 & WebAuthn
Explore FIDO2 and WebAuthn standards for passwordless authentication, learn implementation strategies, and discover how to enhance security while improving user experience.
No More XSS - Deploying CSP with Nonces and Strict-Dynamic
Learn to implement Content Security Policy with nonces and strict-dynamic to prevent XSS attacks. Discover practical deployment strategies for Pinterest and Instapaper, and understand potential vulnerabilities.
Chrome Extension Risks and You
Explore Chrome extension risks, malicious examples, and Lyft's strategic approach to mitigate threats at scale. Learn effective strategies for enhancing browser security.
Two-Faces of WASM Security
Explore WebAssembly's dual nature: its potential for malicious use in sophisticated attacks and the vulnerabilities it introduces, presenting challenges for both users and web developers.
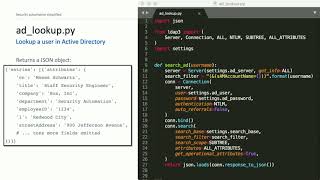
Security Automation Simplified
Practical guide to implementing security automation using existing tools and basic coding, demonstrating how to streamline SecOps processes and save time without relying on expensive products.
Offensive Javascript Techniques for Red Teamers
Explore advanced JavaScript techniques for red team operations, including browser exploitation, network reconnaissance, and crafting payloads to target internal vulnerabilities quickly and effectively.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
Pushing the Limits of Web Browsers
Explore advances in virtual machine technology and programming languages shaping web development's future, with insights from a veteran virtual machinist on JavaScript, V8, and Dart.
Visualization Driven Development
Interactive visualizations for understanding algorithms: techniques and examples using HTML, CSS, JavaScript, and D3 to supplement traditional testing and improve code comprehension.
Making an Impact from India to the Rest of the World by Building and Nurturing Women Infosec Community
Empowering women in cybersecurity: Journey of Infosecgirls community from India to global impact. Addressing challenges, fostering inclusivity, and creating opportunities for women in tech through education, mentorship, and community building.
NoJITsu - Locking Down JavaScript Engines
Explore data-only attacks on JavaScript engines and learn defensive strategies to secure JIT compilers against modern threats in web browsers and interactive applications.
Room for Escape - Scribbling Outside the Lines of Template Security
Explore vulnerabilities in Content Management Systems, focusing on template security issues and potential exploits in collaboration platforms. Learn about safe mode attacks and object data validation.
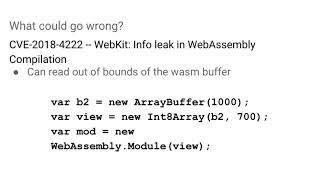
The Problems and Promise of WebAssembly
Explore WebAssembly's features, vulnerabilities, and future security concerns in this comprehensive overview, with practical examples and insights.
Breaking Parser Logic - Take Your Path Normalization Off and Pop 0days Out
Explore path normalization vulnerabilities, their impact on web security, and techniques to exploit them for bypassing access controls and achieving remote code execution.
Two-Factor Authentication, Usable or Not? - A Two-Phase Usability Study of the FIDO U2F Security Key
Explore the usability of FIDO U2F Security Keys for two-factor authentication through a comprehensive two-phase study, evaluating effectiveness and user experience.
Design Pitfalls in Commercial Mini-Programs on Android and iOS
Explore security vulnerabilities in app-in-app paradigms for Android and iOS, focusing on mini-programs' design flaws and potential risks to user privacy and data protection.