Off-Path Attacks Against PKI
Explore vulnerabilities in Certificate Authorities and learn how off-path attackers can compromise PKI security, undermining the foundation of Internet application trustworthiness.

It's a PHP Unserialization Vulnerability Jim, but Not as We Know It
Explore PHP unserialization vulnerabilities, including RCE exploits in popular web applications. Learn attack methodologies, file formats, and defense strategies.
The Hidden RCE Surfaces That Control the Droids
Uncover hidden vulnerabilities in Android OS libraries that process incoming files, potentially leading to remote code execution attacks on various system applications.
AutoSpear - Towards Automatically Bypassing and Inspecting Web Application Firewalls
Explore techniques for automatically bypassing and inspecting web application firewalls, examining vulnerabilities in WAF-as-a-service solutions and cloud security services.
Wibbly Wobbly, Timey Wimey – What's Really Inside Apple's U1 Chip
Explore Apple's U1 Ultra Wideband chip, its capabilities, and potential applications. Dive into firmware, kernel components, and user space modifications for this cutting-edge technology.
Web Timing Attacks Made Practical
Explore practical web timing attacks, improving data collection and statistical analysis for more effective penetration testing. Learn adaptive techniques and open-source tools for identifying cryptographic vulnerabilities.
Blended Web and Database Attacks on Real-Time, In-Memory Platforms
Explore innovative attack vectors on real-time, in-memory platforms, blending web and database vulnerabilities. Learn about new SQL injection techniques, server-side JavaScript exploits, and R-based attacks in SAP HANA.
Bypassing HTTP Strict Transport Security
Explore vulnerabilities in HTTP Strict Transport Security (HSTS) and learn how attackers can exploit inter-operation weaknesses to bypass this protection and launch SSLStrip attacks.
Scala Security - Examining the Play and LiftWeb Frameworks
Explore security aspects of Scala's Play and LiftWeb frameworks, including OWASP Top 10 vulnerabilities, exploitation mitigations, and a new Scala library for SSRF prevention.
Revisiting XSS Sanitization
Explore XSS vulnerabilities in popular WYSIWYG editors and learn an effective sanitization technique using minimal characters and regular expressions to prevent attacks across various contexts.
Session Identifier are for Now, Passwords are Forever - XSS-Based Abuse of Browser Password Managers
Explore XSS-based attacks on browser password managers, their vulnerabilities, and potential solutions. Learn about password field usage on popular websites and get recommendations for protection.
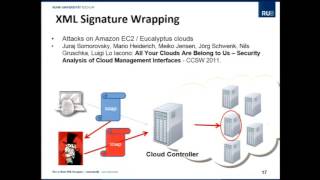
How to Break XML Encryption - Automatically
Explore automated attacks on XML Encryption, including vulnerability detection and exploitation techniques. Learn about recent developments, implementation challenges, and practical security implications.
Exploit Delivery With Steganography and Polyglots
Explore innovative exploit delivery techniques using steganography and polyglots, focusing on encoding browser exploits in image files for undetectable payload transmission.
FileCry - The New Age of XXE
Explore critical XXE vulnerabilities in enterprise software, including 0-day exploits in Java and Internet Explorer. Learn detection, exploitation, and prevention techniques.
HTTP Cookie Hijacking in the Wild - Security and Privacy Implications
Explores security vulnerabilities in websites with partial HTTPS deployment, revealing how cookie hijacking can expose sensitive user data and functionality across major online platforms.
HEIST - HTTP Encrypted Information can be Stolen Through TCP-Windows
Unveils HEIST, a browser-based attack exploiting SSL/TLS vulnerabilities without network access. Demonstrates how to leak cross-origin response sizes, enabling compression-based attacks and sensitive information extraction from popular websites.
An Inconvenient Trust - User Attitudes Toward Security and Usability Tradeoffs
Exploring user perspectives on encryption methods, balancing security and usability in digital communications. Insights from a study on key-exchange vs. key-directory models for everyday messaging.
I Know Where You've Been - Geo-Inference Attacks Via The Browser Cache
Explore geo-inference attacks via browser cache, revealing how websites can sniff users' locations. Learn about vulnerabilities in popular sites, impact on various browsers, and potential defenses against these privacy threats.
Browsers Gone Wild
Unveiling creative browser vulnerabilities and attacks, including confidentiality breaches, login detection, and exploiting HTML5 features, with live demonstrations challenging Same Origin Policy understanding.
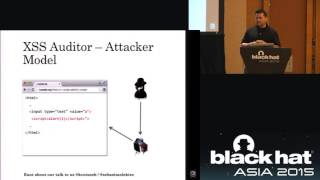
Client-Side Protection Against DOM-Based XSS Done Right
Comprehensive analysis of Chrome's XSS Auditor, revealing vulnerabilities and proposing an improved filter design using client-side taint tracking for robust DOM-XSS protection.
Untangling the DOM for More Easy-Juicy Bugs
Explore dynamic JavaScript analysis with Hookish!, an open-source Chrome extension for penetration testing. Learn to uncover DOM-based vulnerabilities and enhance web app security assessments.