Blazor - A New Framework for Browser-Based .NET Apps
Explore Blazor, a framework for building browser-based .NET apps using WebAssembly. Learn its component-based architecture, routing, DI system, and JavaScript interop to create responsive client-side UIs.
Building APIs Rapidly with Azure Functions
Learn to rapidly build scalable, OpenAPI-compliant APIs using Azure Functions. Discover how to create, extend, and maintain APIs efficiently, with practical demonstrations and comparisons to other frameworks.
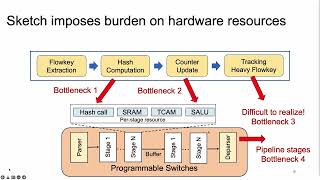
SketchLib - Enabling Efficient Sketch-based Monitoring on Programmable Switches
Explore efficient sketch-based network monitoring on programmable switches with SketchLib. Learn optimization techniques to reduce hardware resource footprint while maintaining measurement accuracy.
Three Ways DuckDuckGo Protects User Privacy While Getting Things Done - And How You Can Too
Explore DuckDuckGo's innovative privacy-protecting techniques: NGiNX proxying, SSL connection upgrades, and anonymous A/B testing. Learn how to implement these strategies in your own projects.
Designing Resilient Data Pipelines
Strategies for resilient data pipelines: observability, immutable inputs, declarative pipelines, and data validation. Reduce operational complexity, update risks, and accuracy concerns in complex systems.
Lessons Learned in Black Box Monitoring 25,000 Endpoints
Explore black box monitoring of 25,000 government endpoints, learning strategies to monitor resistant systems and improve digital services across the US government.
An Extensive Formal Security Analysis of the OpenID Financial Grade API
Comprehensive formal security analysis of OpenID Financial-grade API, uncovering vulnerabilities and proposing mitigations for this high-stakes OAuth 2.0 profile designed for Open Banking scenarios.
They Would do Better if They Worked Together - The Case of Interaction Problems Between Password Managers and Websites
Explore interaction issues between password managers and websites, uncovering challenges and potential solutions for improved digital security.
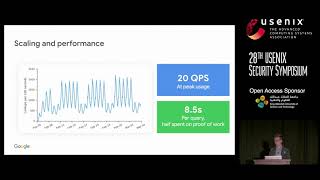
Protecting Accounts from Credential Stuffing with Password Breach Alerting
Explore a privacy-preserving protocol for detecting exposed credentials, its implementation as a cloud service, and its effectiveness in prompting users to update compromised passwords.
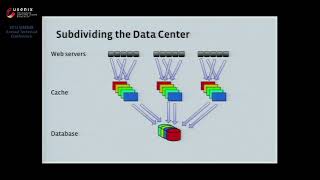
TAO - Facebook’s Distributed Data Store for the Social Graph
Explore Facebook's TAO, a distributed data store designed for efficient social graph access. Learn about its architecture, API, and how it handles billions of reads and millions of writes per second.
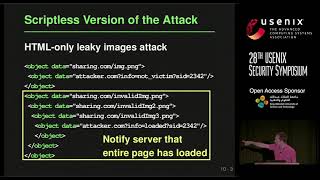
Leaky Images - Targeted Privacy Attacks in the Web
Unveils a novel privacy attack exploiting shared images on popular websites, allowing attackers to track user visits and link identities across platforms without using scripts.
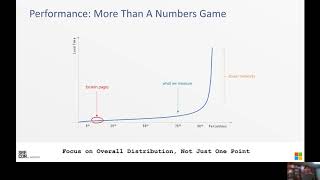
Off the Beaten Path - Moving Observability Focus from Your Service to Your Customer
Exploring customer-centric observability beyond traditional metrics, emphasizing direct engagement, user experience capture, and rethinking performance to enhance SRE practices and improve overall service quality.
HTTP/2 - The Sequel is Always Worse
Uncover HTTP/2 vulnerabilities and their impact on web security. Learn about implementation flaws, RFC imperfections, and new attack techniques targeting high-profile websites and various server infrastructures.
Practical HTTP Header Smuggling - Sneaking Past Reverse Proxies to Attack AWS and Beyond
Explore HTTP header smuggling techniques to bypass security measures, attack web applications, and exploit vulnerabilities in proxy servers and AWS services.
IPvSeeYou - Exploiting Leaked Identifiers in IPv6 for Street-Level Geolocation
Explore a data fusion attack on IPv6 home routers for precise street-level geolocation, uncovering millions of devices worldwide and discussing privacy implications.
HTTP/2 - The Sequel is Always Worse
Explore HTTP/2 vulnerabilities, implementation flaws, and RFC imperfections. Learn advanced request smuggling techniques and their impact on major platforms like Netflix and Amazon.
Glitch Chronicles - Turning WebGL Into A Hammer
Explore WebGL vulnerabilities and GPU-based Rowhammer attacks in this technical deep dive on exploiting graphics hardware for security breaches.
Mallet - Towards a Generic Intercepting Proxy
Explore Mallet, a new open-source intercepting proxy with a user-friendly interface, high performance, and extensive protocol support. Learn its advantages over existing tools and potential applications.
Neuralfuzz - Neural Networks for Fuzzing Web Apps
Explore neural network-based fuzzing for web apps, enhancing coverage and efficiency in identifying vulnerabilities through machine learning and intelligent payload generation.
CSP Oddities
Explore Content Security Policy intricacies, common pitfalls, and innovative solutions. Learn to deploy effective CSP policies and discover potential vulnerabilities in web application security.
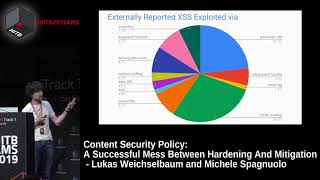
A Successful Mess Between Hardening and Mitigation
In-depth analysis of Content Security Policy for XSS prevention, exploring its effectiveness, debunking myths, and sharing real-world data on successful XSS mitigation in sensitive applications.