Beyond OWASP Top 10 by Aaron Hnatiw - Hack in Paris - 2017
Explore 5 dangerous web vulnerabilities beyond OWASP Top 10, covering exploits and mitigations for both developers and pentesters to enhance application security.
Hello, I'm Your Edge Case - ChaosWest - 36C3
Exploración de los desafíos y soluciones en el diseño de formularios digitales para datos personales, con énfasis en la inclusión y precisión para diversas identidades y experiencias.
The Forbidden Image - Security Impact of SVG on the WWW - Mario Heiderich - Hack in Paris
Explores security risks of SVG images on the web, covering potential exploits, scripting vulnerabilities, and mitigation strategies for developers and security professionals.
Unwinnable Prizes on the Internet - Roland Meertens - RC3
Exposé sur les jeux en ligne truqués offrant des prix impossibles à gagner, révélant les techniques trompeuses utilisées pour collecter les adresses e-mail des utilisateurs.
The Web Tracking Arms Race: Past, Present, and Future - USENIX Enigma 2018
Explores online tracking evolution, privacy challenges, and solutions. Discusses research findings, tool development, and recommendations for policymakers and browser vendors to enhance user privacy.
Human Computation with an Application to Passwords - Manuel Blum - USENIX Enigma - 2017
Explore secure password computation techniques using human-computable functions, transforming website names into unique passwords without memorization.
Inside "MOAR TLS" - How We Think about Encouraging External - Emily Schechter - USENIX Enigma Conference - 2017
Exploring Google's "MOAR TLS" project to promote HTTPS adoption, addressing challenges, sharing strategies, and discussing the future of web security.
Uninvited Guests on the World's Wild Web - Understanding Malicious Web Bots
Explore malicious web bots, their impact on applications, and effective countermeasures using OWASP's Automated Threat Handbook. Learn to protect against unwanted automation and improve web security.
Not All HTTPS Sites Are Equally Secure, Make Yours Safer
Explore HTTPS security enhancements, protocols, and tools to strengthen your website's encryption. Learn about free certificates and services for optimal implementation.
Interact Differently - Get More from Your Tools Through Exposed APIs
Explore how to leverage exposed APIs and plugin interfaces in software tools to enhance functionality, streamline workflows, and create custom solutions for improved efficiency and effectiveness.
Why the LinkedIn Hack Could Be Your Biggest AppSec Threat
Explore account takeover threats, their long-term impact, and effective defense strategies. Learn about hacking techniques, credential stuffing, and tools to protect against evolving cyber risks.
SSL and the Future of Authenticity
Explore SSL's role in online security, challenges with certificate authorities, and innovative approaches to authentication in the digital age.
Pwning Intranet with HTML 5
Explore HTML5's potential for intranet exploitation using BeEF framework. Learn footprinting, network discovery, port scanning, and inter-protocol exploitation techniques.
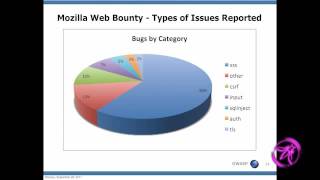
Security Evolution - Bug Bounty Programs for Web Applications
Explore the evolution of web security through bug bounty programs, focusing on Mozilla's experience, benefits, challenges, and ethical considerations.
An Introduction to ZAP - The OWASP Zed Attack Proxy
Learn to use ZAP, an open-source web application security scanner. Explore features like active scanning, fuzzing, and brute force attacks to enhance your penetration testing skills.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
Securing Modern API and Microservice Based Applications by Design
Learn to secure modern API and microservices architectures with expert insights on key concerns, architectural patterns, and actionable solutions for robust application security.
New Age Cloud Security - How to Build Secure Multi-Cloud Applications and Still Sleep Well
Learn to build secure multi-cloud applications with modern techniques. Explore industry trends, development phases, and essential components like TLS, DNS, user management, and data encryption for robust cloud security.
How to Build an Effective Malware Protection Architecture for File Uploads in Modern Web Apps
Explore a novel approach to automated malware analysis for file uploads in web apps, focusing on scalability, performance, and effective detection of malicious content.
AppSec Pipelines and Event-based Security - Moving Beyond a Traditional Security Test
Strategies for scaling AppSec programs using automation, continuous health checks, and event-based security to keep pace with rapid software development and delivery in large organizations.
Fixing XSS with Content Security Policy
Explore Content Security Policy (CSP) as a defense against XSS attacks, comparing CSP 1.0 and 2.0, and learn implementation strategies for enhanced web application security.