OWASP Top 10 Proactive Controls
Comprehensive guide to OWASP Top 10 Proactive Controls for secure software development, covering essential techniques from query parameterization to threat modeling, presented by expert Jim Manico.
Million Browser Botnet
Explore how online advertising networks can be exploited to create massive browser botnets, enabling DDoS attacks, spam campaigns, and password cracking without leaving traces. Learn about the scalability and potential risks of this attack scenario.
Riding the Magical Code Injection Rainbow
Explore advanced exploitation techniques for SQL injection, XPath injection, cross-site scripting, and shell command injection using the Magical Code Injection Rainbow framework for configurable vulnerable applications.
Authz is the New Authn - Trust Elevation with UMA and OpenID Connect
Explore standards-based trust elevation in online identity using UMA and OpenID Connect for enhanced fraud mitigation and centralized authentication policies in web access management.
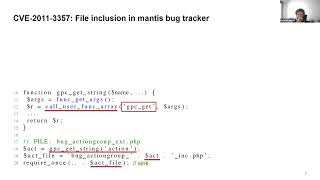
Web Developers, Beware of the Tarpits for SAST in Your Code
Explore SAST testability patterns, their impact on code security, and strategies for improving vulnerability detection in web development.
OWASP Flagship Projects - OWASP Juice Shop
Explore OWASP Juice Shop, a vulnerable web application for security training. Learn about challenges, cross-site scripting, coding exercises, and future enhancements in this comprehensive overview.
OWASP Flagship Projects - OWASP Amass
Explore OWASP Amass, a powerful tool for information gathering and external asset discovery in cybersecurity. Learn its features, data sources, and future developments.
Contact Center Authentication
Explore best practices for authenticating customers over the phone in contact centers, including research findings, common pitfalls, and innovative solutions for improved security and user experience.
Cache Me If You Can - Messing with Web Caching
Explore web caching vulnerabilities including Web Cache Deception, Edge Side Include Injections, and Web Cache Poisoning. Learn detection techniques and mitigation strategies for these emerging threats in application security.
Automated Account Takeover - The Rise of Single Request Attacks
Explore the rise of single request attacks in account takeovers, their sophistication, and effective mitigation strategies through real-world case studies and expert insights.
Remediate The Flag - Practical AppSec Training Platform
Hands-on platform for developers to find and fix security vulnerabilities in code. Offers real-time feedback, scoring, and customizable exercises to improve application security skills.
Deserialization - What, How and Why Not
Explore insecure deserialization risks, vulnerabilities, and prevention techniques through code examples and live demos, focusing on Java but applicable to other languages.
Web Application Compromise Mitigation with Crypto Anchoring - AppSecUSA
Explore crypto anchoring as a solution to protect sensitive data from breaches, paired with effective monitoring for enhanced web application security.
The Anatomy of a Secure Web Application in Java Using Spring Security and Apache Fortress
Practical guidance on implementing secure Java web applications using Spring Security and Apache Fortress. Covers authentication, authorization, and confidentiality controls with hands-on demos and code examples.
Making Security Approachable for Developers and Operators
Explore strategies to make security more accessible for developers and operators through APIs, secure-by-default platforms, and policy as code, enhancing overall security posture.
What's New in TLS 1.3
Explore TLS 1.3's security enhancements, new protocol handshakes, and 0-RTT resumption. Learn about potential deployment pitfalls and how to avoid them in this comprehensive overview of the latest TLS version.
Common REST API Security Pitfalls
Explore common REST API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security for robust, future-proof applications.
Core Rule Set for the Masses
Insights on fine-tuning ModSecurity Core Rule Set for large-scale deployments, reducing false positives, and optimizing web application firewall performance.
An Overview of API Underprotection
Explores API security challenges, threats, and emerging technologies. Covers OAuth2, API keys, mobile app security, TLS pinning, and advanced techniques like app hardening and software attestation.
The Security We Need - Designing Usable IoT Security
Explore usable IoT security design principles to create user-friendly, effective protection. Learn strategies for clear communication, secure defaults, and seamless integration of security measures.
The Insecurity Caused by Trusting Your Client-Side Storage
Explore vulnerabilities in client-side storage, including cookies and web storage, and learn exploit patterns and attack vectors to enhance web application security.