Good Bot, Bad Bot: Characterizing Automated Browsing Activity
Explore Aristeus, a system for deploying honeysites to study malicious bot behavior. Learn about bot traffic patterns, attack strategies, and the importance of understanding automated browsing activity for web security.
Everything You Always Wanted to Know About Fingerprinting Browser Extensions
Explore browser extension fingerprinting techniques, their implications for user privacy, and current browser defenses. Learn about DOM modifications, stylesheet hijacking, and web-accessible resources.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
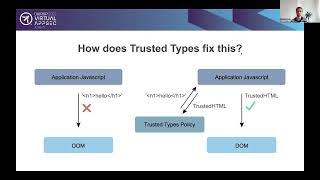
Trusted Types: A World Without XSS
Explore cutting-edge web security with Trusted Types, a powerful defense against XSS attacks. Learn implementation strategies and best practices from industry experts.
Landmines in the API Landscape
Explore potential security vulnerabilities in API development and learn strategies to mitigate risks in this insightful talk by a cybersecurity expert.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
OWASP Web Honeypot Project
Explore web application security through honeypot technology. Learn deployment strategies, data analysis, and threat intelligence gathering to enhance your cybersecurity defenses.
Common Application Security Mistakes Enabling Automated Attacks
Explore common security flaws enabling automated attacks on applications, including retail fraud and account takeovers. Learn from real-world examples and discover effective prevention strategies.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
2013 AppSec Guide and CISO Survey - Making OWASP Visible to CISOs
Insights from OWASP's 2013 AppSec Guide and CISO Survey, focusing on application security governance, risk management, and investment strategies for Chief Information Security Officers.
Introduction to Emerging JSON-Based ID and Security Protocols
Explore emerging JSON-based identity and security protocols with Brian Campbell, focusing on JOSE and its applications in modern authentication and authorization systems.
Diversity for Those Playing Life on Easy
Explore diversity challenges in open source communities, learn from personal experiences, and gain actionable insights to foster inclusivity and build stronger collaborative environments.
Agreeing to Disagree - Philanthropy and the Marketplace of Ideas
Explore the role of philanthropy in shaping public discourse and policy debates, examining criticisms and arguments for diverse viewpoints in a democratic society.
Exposing Security Flaws in Trading Technologies
Uncovers vulnerabilities in popular trading platforms, highlighting risks in electronic trading. Discusses security gaps in websites, desktop apps, and mobile apps used for stock and cryptocurrency trading.
Hard to Port - A Snapshot of the Vulnerability Landscape in 2015
Explore the 2015 vulnerability landscape through anonymized data, discussing trends, challenges, and the shift towards continuous application security and risk management.
HTTPS Everywhere: Improving Web Security and Usability
Exploring Chrome's efforts to enhance HTTPS adoption: tools for debugging, reporting mechanisms for safe rollout, and strategies to improve web security.
Design Approaches for Security Automation
Explore criteria for designing and evaluating security automation tools, including build vs. buy decisions, deployment strategies, and effective implementation for organizational needs.
Preventing Security Bugs through Software Design
Learn strategies to prevent security vulnerabilities through API and framework design, focusing on SQL injection and XSS prevention techniques used successfully at Google.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.
Modern Malvertising and Malware Web-Based Exploit Campaigns
Explore modern malvertising techniques and web-based exploit campaigns. Learn about top malware types, distribution methods, and obfuscation layers through real-world examples and technical walkthroughs.
Automating API Penetration Testing Using Fuzzapi
Explore automated API penetration testing with fuzzapi, addressing common vulnerabilities in REST APIs. Learn to integrate security testing into development pipelines for early detection and mitigation.