SPArring with the Security of Single Page Applications - MMA Hacker Training
Explore security challenges in Single Page Applications through an MMA analogy. Learn about SPA frameworks, REST APIs, WebSockets, and interconnectivity to become a "Mixed Multilayer Application Hacker".
Attack Patterns for Black-Box Security Testing - AppSecEU 2016
Explore attack patterns for black-box security testing in web applications, focusing on methodologies and strategies to identify vulnerabilities effectively.
Systematically Breaking and Fixing OpenID Connect
Explore systematic vulnerabilities and fixes in OpenID Connect, covering attack types, threat models, and countermeasures for improved authentication security.
Detecting and Managing Bot Activity More Efficiently
Explore efficient bot detection techniques, categorization methods, and response strategies to manage both beneficial and potentially harmful automated web traffic.
OWASP Security Knowledge Framework - Project Overview and Best Practices
Explore OWASP Security Knowledge Framework with project lead Glenn Ten Cate, discussing goals, milestones, and best coding practices for this essential security tool.
OWASP ZAP - More Advanced Features
Explore advanced features of OWASP ZAP, a powerful open-source web application security testing tool, with insights from Simon Bennetts at AppSecEU 2015 in Amsterdam.
The API Assessment Primer
Learn essential API security assessment techniques, including key considerations, testing steps, and best practices for protecting APIs and mobile applications from common vulnerabilities and threats.
Web Service Workers - Breaking the Web: Exploiting a Cool Feature
Explore Web Service Workers' potential to disrupt web security, examining innovative uses and potential vulnerabilities in this cutting-edge browser feature.
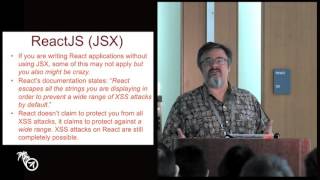
Advances in Secure Coding Frameworks
Explore positive advancements in application security frameworks, highlighting built-in security features that simplify secure coding for developers and improve overall software safety.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
OCSP Stapling in the Wild - Lecture
Explore OCSP stapling in the wild with experts Devdatta Akhawe and Emily Stark. Learn about TLS security, browser implementations, and real-world challenges in HTTPS ecosystems.
CSP - The Good, the Bad and the Ugly
Explore Content Security Policy's strengths and weaknesses in web application security, presented by Shape Security's engineering manager Ilya Nesterov at APPSEC CA 2017.
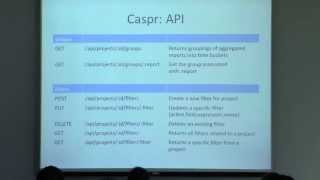
Content Security Policy Reporting and Aggregation with Caspr - OWASP AppSec California 2015
Explore Content-Security-Policy (CSP) violation reporting with Caspr, a tool for collecting and analyzing reports. Learn about CSP background, Caspr usage, and related tools for enhancing web application security.
Securing Software's Future: Why API Design Matters
Explore how API design can prevent vulnerabilities, guide developers towards secure implementations, and shape the future of software security through better development environments.
Don't Touch Me That Way - Mobile Application Security Best Practices
Explore secure mobile app development strategies and best practices to protect against common vulnerabilities and attacks in this insightful OWASP conference talk.
Hardening the Web Platform
Explore web platform security with Mike West's keynote on hardening techniques, challenges, and future directions for a more robust online environment.
Making CSP Great Again - Enhancing Content Security Policy
Explore advanced Content Security Policy techniques to enhance web application security and mitigate XSS vulnerabilities effectively.
Naxsi: A Web Application Firewall for NGINX
Explore Naxsi, an open-source web application firewall for NGINX, and learn about its features, implementation, and benefits for enhancing web application security.
Making SSL Warnings Work - Improving Security and User Experience
Explore strategies to improve SSL warnings in Chrome, focusing on reducing false positives and enhancing user understanding of security threats through clear design and communication.
PCI DSS and Secure Applications - Best Practices for Compliance
Explore best practices for developing secure applications compliant with PCI DSS requirements. Learn key practices, testing procedures, and evidence needed to meet compliance standards in payment card environments.
Security Implications of Cross-Origin Resource Sharing - HTML5 and CORS Analysis
Explore security implications of Cross-Origin Resource Sharing in HTML5, including its impact on same-origin policy, potential vulnerabilities, and mitigation strategies for web application developers.