Popular Approaches to Preventing Code Injection Attacks are Dangerously Wrong
Explores limitations of current code injection prevention methods and introduces Name Space Layout Randomization (NSLR) as a novel approach to secure Java applications against known and zero-day vulnerabilities.
Detecting CSRF Vulnerability Reliably - Programmatic Approach
Explore a programmatic approach to reliably detect CSRF vulnerabilities in web applications, overcoming common shortcomings of existing tools and improving automated security testing.
Remediating XSS in GitHub Open Source Projects - Lessons Learned
Insights on scaling XSS remediation across GitHub open source projects, focusing on risk reduction, adding security controls, and automating code modification for diverse applications.
Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
Philanthropy and Democracy: Dangerous Liaisons
Explore the complex relationship between philanthropy and democracy, examining the benefits and potential threats of big philanthropy to democratic governance and societal progress.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface, and learn to integrate security testing into CI/CD pipelines for effective DevOps practices.
HTTPS Security Headers: HSTS, TLS, HPKP, and CSP Implementation - APPSEC CA 2017
Comprehensive guide to implementing HTTPS using HSTS, TLS, HPKP, and CSP. Learn best practices for secure web communication from Salesforce security experts.
DASTProxy: Automated Security Testing Focused on Business Context
Explore DASTProxy: a tool for automated security testing that focuses on business context rather than crawling, enhancing efficiency and effectiveness in application security assessments.
Monitoring Application Attack Surface to Integrate Security into DevOps Pipelines
Explore integrating security into DevOps pipelines through application attack surface monitoring. Learn strategies from a recognized expert to enhance your organization's software security practices.
Application Security California 2017 - Keynote Address
Explore cutting-edge application security insights and strategies with industry expert Chenxi Wang in this OWASP Foundation presentation from AppSec California 2017.
Error Handling and Security Management in AI Powered Apps - Web Development With AI Episode 7
Learn to handle errors and manage security in AI-powered web apps. Covers bug fixing, input validation, protection against bad actors, and AI-specific attack prevention.
Webhooks Hookups - Abusing API Developers
Explore the security risks of Webhooks in API development, including potential vulnerabilities, real-world examples, and preventive measures. Learn about a new toolkit for auditing Webhook exposure.
Rhyming with Hacks - The Ballad of Supply Chain Attacks
Explore supply chain attacks, their anatomy, and prevention strategies. Learn about real-life examples, existing solutions, and a new DOM monitoring approach with live demonstration.
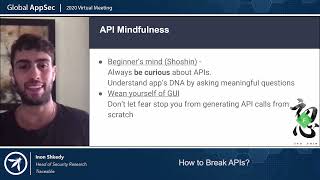
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.
What's The Future - Automation, Jobs, and the Human-Centered Economy
Explore the impact of automation on jobs and the economy, discussing strategies to leverage technology for growth and create a human-centered future.

WebAuthn - Balancing Strong Authentication, Privacy, and Convenience
Explore the balance between robust authentication, user privacy, and ease of use in WebAuthn implementation for enhanced online security.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
Stop the Looters: Method to Detect Digital Skimming Attacks
Discover a method to detect and prevent digital skimming attacks on websites, protecting sensitive customer data from theft by malicious actors like Magecart.
OWASP Top 10 Privacy Risks 2021 - Understanding and Mitigating Web Application Privacy Threats
Explore OWASP's updated Top 10 Privacy Risks for web applications, covering vulnerabilities, consent issues, and data quality. Learn countermeasures to build a more private digital future.
Passive Fingerprinting of HTTP/2 Clients
Explore HTTP/2 protocol nuances for passive client fingerprinting. Learn about implementation differences, potential use cases, and security implications in this comprehensive overview.