Core Rule Set for the Masses
Insights on fine-tuning ModSecurity Core Rule Set for large-scale deployments, reducing false positives, and optimizing web application firewall performance.
The Insecurity Caused by Trusting Your Client-Side Storage
Explore vulnerabilities in client-side storage, including cookies and web storage, and learn exploit patterns and attack vectors to enhance web application security.
Temporal - Achieving the Web Isolation Nirvana - How Far Along Are We?
Explore web isolation's evolution, current approaches, and future challenges. Learn about a client-side sandboxing solution and discuss the future of web application security.
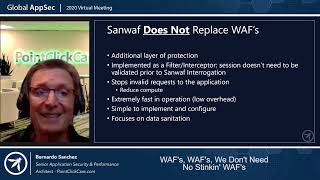
Extending WAFs at the Application Layer
Explore application-level security control with Sanwaf, an alternative to traditional WAFs. Learn its structure, datatypes, and implementation for enhanced web application protection.
Magecart 2020 - The New Face of XSS
Explore Magecart's evolution, injection techniques, and threat complexity. Learn from real-world case studies and discover strategies to prevent these sophisticated web skimming attacks.
OWASP Flagship Projects - OWASP ModSecurity Core Rule Set
Explore OWASP ModSecurity Core Rule Set: web application firewall rules, paranoia levels, and project developments for enhanced security and threat protection.
Breaking Web Applications Built On Top of Encrypted Data
Explores vulnerabilities in web applications using encrypted data, focusing on multi-key searchable encryption. Analyzes attacks against Mylar, discussing metadata risks and active threat models.
A Comprehensive Formal Security Analysis of OAuth 2.0
Comprehensive formal security analysis of OAuth 2.0, examining authorization, authentication, and session integrity properties, and discussing potential attacks and mitigations.
Practical Crypto Attacks Against Web Applications
Explore practical crypto attacks on web apps, covering ECB and CBC modes, block swapping, padding oracles, and signed cookies. Gain insights into vulnerabilities and defense strategies.
Fingerprinting Web Application Platforms by Variations in PNG Implementations
Explore PNG implementation variations across web platforms for enhanced fingerprinting techniques in security audits, overcoming traditional methods and identifying platforms even with anti-fingerprinting measures.
Preventing Authentication Bypass - A Tale of Two Researchers
Explore techniques for identifying authentication bypass vulnerabilities, learn effective researcher-company partnerships, and discover secure coding practices to prevent similar flaws in web applications.
Command Injection in F5 iRules
Explore command injection vulnerabilities in F5 iRules, focusing on syntax, exploitation techniques, and security implications for BigIP F5 products used in high-performance web traffic routing.
Injecting Security Into Web Apps With Runtime Patching And Context Learning
Explore advanced web application security techniques using Runtime Application Self Protection (RASP) to prevent code injections and other vulnerabilities through dynamic analysis and patching.
Hacking Your Cable TV Network
Explore cable TV network vulnerabilities and attacks, including analog and digital systems, IRD decoders, and management servers. Learn techniques for hijacking set-top boxes and remote shutdown.
Introduction to the OWASP ModSecurity Core Rule Set
Learn about OWASP ModSecurity Core Rule Set, a powerful open-source web application firewall. Discover key features like paranoia levels and anomaly scoring, and see its effectiveness in protecting against various attacks.
Running Away from Security - Web App Vulnerabilities and OSINT Collide
Explore web app vulnerabilities and OSINT techniques, focusing on fitness tracking apps and their potential security risks. Learn to protect your online presence and data.

Building Secure Systems in Haskell
Explore building secure web applications using Haskell's LIO and Hails framework, focusing on data privacy protection through language-level information flow control and declarative policy specification.
From the OWASP Top Ten to the OWASP ASVS
Comprehensive guide to application security, moving beyond OWASP Top Ten to ASVS for robust security practices. Explores 180+ requirements for defining and implementing secure software development.
HTTP Security Headers You Need To Have On Your Web Apps
Explore essential HTTP security headers to protect web apps from vulnerabilities. Learn implementation techniques and see live demos of their impact on site security.
Practical HTTP Header Smuggling - Sneaking Past Reverse Proxies to Attack AWS and Beyond
Explore HTTP header smuggling techniques to bypass security measures, attack web applications, and exploit vulnerabilities in proxy servers and AWS services.
Neuralfuzz - Neural Networks for Fuzzing Web Apps
Explore neural network-based fuzzing for web apps, enhancing coverage and efficiency in identifying vulnerabilities through machine learning and intelligent payload generation.