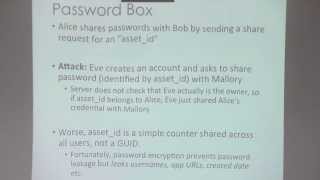
The Emperor’s New Password Manager - Security Analysis of Web-based Password Managers
Security analysis of web-based password managers, revealing vulnerabilities in features like one-time passwords and bookmarklets. Explores diverse root causes and provides guidance for improving password manager security.
AutoScaling Web Application Security in the Cloud
Explore auto-scaling web application security in cloud environments, focusing on practical examples using AWS. Learn techniques, tools, and strategies for effective security implementation in rapidly scaling applications.
Creating a Buzz - Tales of Building WordPress Honeypots at Scale
Explore the world of WordPress honeypots, their deployment at scale, and surprising insights into black-hat tactics in this intriguing cybersecurity presentation.
CSP Pitfalls and Gotchas
Explore common pitfalls and gotchas in Content Security Policy implementation, focusing on whitelist issues, SameOrigin policy, and unsafe inline practices. Learn strategies for building a robust security framework.
Developing and Managing an OWASP Project - Projects 101
Learn to create, manage, and grow an OWASP project. Explore naming, sponsorship, levels, services, and resources for successful open-source security initiatives.
Reversing Client Side JavaScript Using the Chrome Dev Tools Protocol
Explore Chrome Dev Tools protocol for JavaScript reversal, bug finding, and vulnerability detection. Learn to modify web app behavior and automate pentesting tasks using Go-based plugins.
#Eko2020 Bounty Hunters | Adrian Pedrazzoli: XSS de -1 a 0
Aprende técnicas básicas para detectar XSS, tipos, recursos necesarios y ejemplos de hallazgos en programas de Bug Bounty. Incluye recomendaciones prácticas para cazadores de recompensas.
Beyond OWASP Top 10 by Aaron Hnatiw - Hack in Paris - 2017
Explore 5 dangerous web vulnerabilities beyond OWASP Top 10, covering exploits and mitigations for both developers and pentesters to enhance application security.
Uninvited Guests on the World's Wild Web - Understanding Malicious Web Bots
Explore malicious web bots, their impact on applications, and effective countermeasures using OWASP's Automated Threat Handbook. Learn to protect against unwanted automation and improve web security.
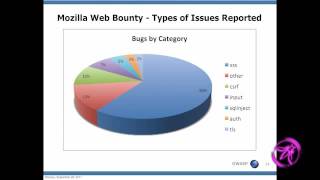
Security Evolution - Bug Bounty Programs for Web Applications
Explore the evolution of web security through bug bounty programs, focusing on Mozilla's experience, benefits, challenges, and ethical considerations.
An Introduction to ZAP - The OWASP Zed Attack Proxy
Learn to use ZAP, an open-source web application security scanner. Explore features like active scanning, fuzzing, and brute force attacks to enhance your penetration testing skills.
Implementing AppSensor in ModSecurity
Explore advanced web application security techniques using AppSensor and ModSecurity, focusing on detection points, SQL injection prevention, and innovative defense strategies.
How to Build an Effective Malware Protection Architecture for File Uploads in Modern Web Apps
Explore a novel approach to automated malware analysis for file uploads in web apps, focusing on scalability, performance, and effective detection of malicious content.
Fixing XSS with Content Security Policy
Explore Content Security Policy (CSP) as a defense against XSS attacks, comparing CSP 1.0 and 2.0, and learn implementation strategies for enhanced web application security.
Riding the Magical Code Injection Rainbow
Explore advanced exploitation techniques for SQL injection, XPath injection, cross-site scripting, and shell command injection using the Magical Code Injection Rainbow framework for configurable vulnerable applications.
OWASP Flagship Projects - OWASP Juice Shop
Explore OWASP Juice Shop, a vulnerable web application for security training. Learn about challenges, cross-site scripting, coding exercises, and future enhancements in this comprehensive overview.
OWASP Flagship Projects - OWASP Amass
Explore OWASP Amass, a powerful tool for information gathering and external asset discovery in cybersecurity. Learn its features, data sources, and future developments.
Contact Center Authentication
Explore best practices for authenticating customers over the phone in contact centers, including research findings, common pitfalls, and innovative solutions for improved security and user experience.
Deserialization - What, How and Why Not
Explore insecure deserialization risks, vulnerabilities, and prevention techniques through code examples and live demos, focusing on Java but applicable to other languages.
Web Application Compromise Mitigation with Crypto Anchoring - AppSecUSA
Explore crypto anchoring as a solution to protect sensitive data from breaches, paired with effective monitoring for enhanced web application security.
The Anatomy of a Secure Web Application in Java Using Spring Security and Apache Fortress
Practical guidance on implementing secure Java web applications using Spring Security and Apache Fortress. Covers authentication, authorization, and confidentiality controls with hands-on demos and code examples.