CSP Oddities
Explore Content Security Policy intricacies, common pitfalls, and innovative solutions. Learn to deploy effective CSP policies and discover potential vulnerabilities in web application security.

SSRF PWNs - New Techniques and Stories
Découvrez de nouvelles techniques d'attaques SSRF, leurs impacts sur la sécurité des applications web et des exemples concrets d'exploitation, présentés par deux experts en sécurité informatique.
A Short History of the JavaScript Security Arsenal
Explore the evolution of JavaScript security tools and techniques over six years, from basic port scanners to advanced frameworks, with insights from expert Petko D. Petkov.
Making an Impact from India to the Rest of the World by Building and Nurturing Women Infosec Community
Empowering women in cybersecurity: Journey of Infosecgirls community from India to global impact. Addressing challenges, fostering inclusivity, and creating opportunities for women in tech through education, mentorship, and community building.
Off-Path Attacks Against PKI
Explore vulnerabilities in Certificate Authorities and learn how off-path attackers can compromise PKI security, undermining the foundation of Internet application trustworthiness.

It's a PHP Unserialization Vulnerability Jim, but Not as We Know It
Explore PHP unserialization vulnerabilities, including RCE exploits in popular web applications. Learn attack methodologies, file formats, and defense strategies.
Web Timing Attacks Made Practical
Explore practical web timing attacks, improving data collection and statistical analysis for more effective penetration testing. Learn adaptive techniques and open-source tools for identifying cryptographic vulnerabilities.
Blended Web and Database Attacks on Real-Time, In-Memory Platforms
Explore innovative attack vectors on real-time, in-memory platforms, blending web and database vulnerabilities. Learn about new SQL injection techniques, server-side JavaScript exploits, and R-based attacks in SAP HANA.
Scala Security - Examining the Play and LiftWeb Frameworks
Explore security aspects of Scala's Play and LiftWeb frameworks, including OWASP Top 10 vulnerabilities, exploitation mitigations, and a new Scala library for SSRF prevention.
Revisiting XSS Sanitization
Explore XSS vulnerabilities in popular WYSIWYG editors and learn an effective sanitization technique using minimal characters and regular expressions to prevent attacks across various contexts.
Untangling the DOM for More Easy-Juicy Bugs
Explore dynamic JavaScript analysis with Hookish!, an open-source Chrome extension for penetration testing. Learn to uncover DOM-based vulnerabilities and enhance web app security assessments.
Exploiting XXE Vulnerabilities in File Parsing Functionality
Techniques for exploiting XXE vulnerabilities in file parsing, focusing on XML-supported formats like docx and xlsx. Includes real-world examples and introduces a tool for creating 'XXE backdoored' files.
The Challenges of Automated Web Application Scanning
Explore challenges in automated web application scanning, focusing on security vulnerabilities, detection methods, and best practices for effective vulnerability assessment.
Web Application Session Strength
Explore web application security, focusing on session management, token creation, and potential vulnerabilities. Learn strategies to protect against common threats and enhance overall application security.
Web Application Security Crossfire
Explore web application security challenges and solutions through expert insights in this panel discussion from Black Hat USA 2004.
Evasion and Detection of Web Application Attacks
Explore techniques for evading and detecting web application attacks, enhancing your cybersecurity skills and understanding of vulnerabilities in online systems.
WAF Bypass In Depth
Explore advanced techniques for bypassing Web Application Firewalls (WAFs) and demonstrating the impact of cross-site scripting vulnerabilities, even in the presence of sophisticated security measures.
Blindspots
Robert Hansen shares insights on overlooked areas in web application and browser security, challenging industry professionals to broaden their thinking and address critical blindspots.
Be Your Own Threatbuster
Learn essential security practices for web applications, understand hacker perspectives, and discover how to protect your website and customer data from potential threats.
Reversing Web Assembly
Explore techniques for reversing Web Assembly (wasm) in this offensive security talk. Learn key strategies and tools for analyzing and understanding wasm code.
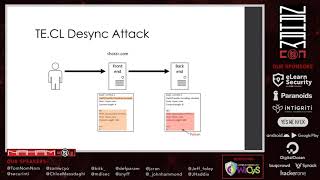
Practical Attacks Using HTTP Request Smuggling
Explore practical HTTP request smuggling attacks, including CL.TE/TE.CL desync techniques, testing methods, and real-world examples. Learn to exploit vulnerabilities for session stealing and response queue poisoning.