Automatic Detection of Inadequate Authorization Checks in Web Applications
Automatic detection of missing authorization checks in web apps using static analysis. Explores techniques, real-world applications, and provides remediation suggestions for developers.
OWASP ZAP Advanced Features for Web Application Security Testing
Explore advanced features of OWASP ZAP for web application security testing, including handling non-standard apps, client-side testing, fuzzing, scripting, and more with expert Simon Bennetts.
Warning Ahead: Security Storms Brewing in JavaScript
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 risks. Learn about emerging security threats and their impact on enterprise data and user safety.
Million Browser Botnet - Creating a JavaScript-Driven Browser Botnet for DDoS Attacks
Explore how online advertising networks can be exploited to create massive browser botnets for various malicious activities, including DDoS attacks and password cracking, without leaving traces.
OWASP Broken Web Applications - Future Developments Beyond Version 1.0
Explore OWASP's virtual machine with 25+ vulnerable web applications for security training and testing. Learn about project features and future developments in web application security.
Hack.me: A New Way to Learn Web Application Security
Explore a free, browser-based platform for practicing offensive techniques on vulnerable web applications. Learn about OWASP Top 10, CMS vulnerabilities, and latest exploits in a sandboxed environment.
OWASP Community Update - June 2014
Explore OWASP's latest initiatives, projects, and community developments in this informative session, gaining insights into web application security advancements and networking opportunities.
OWASP Global Webinar - Initiatives and Projects
Explore OWASP's global initiatives and projects, focusing on web application security. Learn about the Project Space, Global Projects Committee, and Open Source strategies for enhancing cybersecurity.
Unraveling the OWASP Wiki
Explore OWASP's wiki structure, navigation, and content management in this informative webinar. Learn to effectively contribute and utilize this valuable resource for web application security.
PHP Security Project - OWASP Global Webinar
Explore OWASP's PHP Security Project: Learn about secure PHP libraries and tools for enhancing web application security in this informative webinar.
Using the O2 Platform to Automate Application Security Knowledge and Workflows
Explore the O2 platform for automating web application security reviews, enhancing visibility, and streamlining security workflows for both experts and non-experts.
RailsGoat: Vulnerable Ruby on Rails Framework for Security Education
Explore RailsGoat, a vulnerable Ruby on Rails app designed to educate developers and security professionals on OWASP Top 10 vulnerabilities and additional security issues.
Introduction to OWASP's Zed Attack Proxy - Web Application Penetration Testing
Explore OWASP's free, open-source penetration testing tool for web applications. Learn its features, installation, and usage through hands-on demonstrations and testing of insecure web apps.
The 2013 OWASP Top 10 - Understanding Web Application Security Risks
Comprehensive overview of OWASP Top 10 2013, covering changes, risks, and mitigation strategies for web application security. Essential for developers and security professionals.
HTML5 - Security Risks and Tools in Modern Web Applications
Explore HTML5's security implications, from potential risks to innovative tools for enhanced authentication and session tracking. Learn how new features impact web application security.
OWASP Zed Attack Proxy: Latest Features and Developments - Lecture
Explore web application security with OWASP's Zed Attack Proxy. Learn key features, including Plug-n-Hack and Zest scripting, suitable for both novice and experienced penetration testers.
WASPY Awards and OWASP Jeopardy - 2013
Celebrate web application security achievements and test your knowledge in this entertaining OWASP event featuring the WASPY Awards and an interactive Jeopardy-style game.
OWASP PHP Security Project - Securing Web Applications with PHP Libraries and Tools
Explore secure PHP development with OWASP's project, featuring decoupled libraries and tools for enhanced web application security. Learn encryption, password management, and protection against common vulnerabilities.
HTML5 and JavaScript Security Vulnerabilities
Explore JavaScript vulnerabilities, including unique issues, third-party platform exploits, and HTML5 security concerns. Learn to protect against emerging web attack techniques.
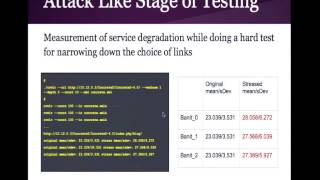
HTTP Time Bandit: Identifying and Exploiting Web Application Performance Bottlenecks
Explore a tool for identifying web application performance bottlenecks and vulnerabilities, enabling efficient DOS/DDOS attacks. Learn about data normalization, testing methods, and attack strategies.
Top Ten Proactive Web Application Controls
Learn essential proactive controls for securing web applications, focusing on key strategies to prevent vulnerabilities and enhance overall security posture.