Introducing the OWASP ModSecurity Core Rule Set 3.0 - AppSec EU 2017
Explore OWASP ModSecurity Core Rule Set 3.0: installation, key concepts, and handling false positives for effective web application firewall protection against common attacks.
AWS Survival Guide - Application Security Essentials
Discover essential strategies for securing applications in AWS environments, covering key concepts and best practices for cloud security from an experienced CTO and application security expert.
Stealth Authentication: Preventing Information Leaks in Web Application Security - APPSEC CA 2017
Explore stealth authentication techniques to enhance web application security by preventing information leaks during the authentication process.
HTTP Desync Attacks - Smashing Into The Cell Next Door
Explore HTTP desync attacks and their impact on web security, learning techniques to exploit vulnerabilities and breach neighboring systems.
Securing Node.js and JavaScript
Explore common security vulnerabilities in Node.js and JavaScript ecosystems, and learn effective strategies to protect your applications from potential attacks.
New Web Platform Security Features to Protect Modern Web Applications
Explore modern web browser security features to protect against XSS, CSRF, and clickjacking. Learn about CSP3, Trusted Types, Fetch Metadata Request Headers, CORP, and COOP for enhanced application security.
NOSQL Web Application Vulnerabilities and Mitigation
Explore NOSQL database vulnerabilities, including injection methods and CSRF, and learn mitigation strategies for enhanced security in web applications.
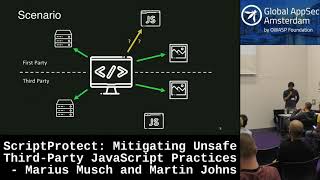
ScriptProtect: Mitigating Unsafe Third-Party JavaScript Practices
Learn techniques to mitigate security risks associated with third-party JavaScript, enhancing web application safety and protecting against potential vulnerabilities.
OWASP ESAPI - A Retrospective: The Good, the Bad, and the Ugly
Retrospective on OWASP ESAPI security library, exploring successes, failures, and challenges in developing and maintaining comprehensive web application defenses.
Web Application Honeypot Threat Intelligence - Techniques and Implementation
Explore web application honeypots for threat intelligence, using ModSecurity and OWASP Core Rule Set to capture attacker activity and protect software against emerging threats.
OWASP Application Gateway: Introduction and Usage for Secure Web Applications
Explore OWASP Application Gateway: a modern HTTP reverse proxy for secure web apps. Learn its benefits, implementation, and customization for enhanced application security.
Purple Teaming with OWASP PurpleTeam - Security Regression Testing
Explore OWASP PurpleTeam, a security regression testing tool for web apps and APIs. Learn its components, setup, and workflows for early detection of application security defects in build pipelines.
OWASP ESAPI - A Retrospective: The Good, the Bad, and the Ugly
Explore the history, successes, and challenges of OWASP ESAPI with Kevin Wall. Gain insights into this security project's evolution and lessons learned.
The History and Future of OWASP - 20 Years in Review
Explore OWASP's 20-year journey, its impact on application security, and future directions. Gain insights into the organization's success factors and vision for the next two decades.
Purple Teaming with OWASP PurpleTeam
Explore OWASP PurpleTeam: a security regression testing tool for web apps and APIs. Learn its journey, architecture, benefits, setup, and various workflows for effective implementation in build pipelines.
OWASP ZAP: Introduction to Web Application Security Testing
Explore OWASP ZAP's latest features, including automation, reporting, and out-of-band testing. Learn how this open-source tool enhances web application security through practical demonstrations and updates.
OWASP Web Security Testing Guide
Comprehensive guide for web security testing, covering methodologies and best practices to identify vulnerabilities and enhance application security.
OWASP Top 10 - Introduction to Web Application Security Risks
Comprehensive overview of OWASP Top 10, exploring critical web application security risks and effective mitigation strategies for developers and security professionals.
OWASP Security Shepherd - Introduction and Overview
Learn to identify and mitigate web application vulnerabilities with OWASP Security Shepherd, an interactive platform for hands-on cybersecurity training and skill development.
OWASP Foundation Opening Remarks
Andrew van der Stock delivers opening remarks, setting the stage for an OWASP Foundation event and highlighting key topics in web application security and open-source collaboration.
OWASP Security Shepherd - Mobile and Web Security Awareness and Education
Explore web and mobile app security risks through interactive lessons and challenges. Improve penetration testing skills and understand vulnerabilities using OWASP Security Shepherd's comprehensive platform.