Security Does Not Need to Be Fun - Ignoring OWASP to Have a Terrible Time
Explore OWASP's free tools and resources for designing and implementing secure web applications, addressing common security challenges in the software development lifecycle.
OWASP Cheatsheets Project
Comprehensive guide to web application security best practices, covering key areas like input validation, authentication, and secure coding techniques.
OWASP ZAP Project: Introduction to Web Application Security Testing
Learn to use OWASP ZAP, a powerful open-source web application security scanner. Discover its features, capabilities, and best practices for identifying vulnerabilities in web applications.
What's New in CRS4 - An Update from the OWASP CRS Project
Explore the latest updates and enhancements in CRS4, the OWASP Core Rule Set project, with insights on improved web application security and threat mitigation strategies.
15 Years of OWASP Top 10 - Has the Cloud Made a Difference?
Explore the evolution of web application security over 15 years, examining the impact of cloud computing on OWASP Top 10 vulnerabilities and current cybersecurity challenges.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Testability Patterns for Web Applications - A New OWASP Project
Explore testability patterns for web applications in this OWASP project presentation, focusing on enhancing security testing effectiveness and efficiency.
Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
Server-Side Prototype Pollution: Detection and Exploitation Techniques - OWASP AppSec Dublin
Explore server-side prototype pollution vulnerabilities, detection techniques, and prevention strategies in web applications with security expert Gareth Heyes.
JavaScript Realms - The Blank Spot in Web Application Runtime Security
Explore JavaScript Realms and their impact on web application runtime security, uncovering potential vulnerabilities and mitigation strategies.
JavaScript Obfuscation: It's All About the Packers
Explore JavaScript obfuscation techniques, focusing on packers and their impact on code security and readability in this informative OWASP presentation.
OWASP Juice Shop Project
Explore web application security with OWASP's intentionally vulnerable Juice Shop, learning about common vulnerabilities and how to exploit and defend against them.
Security Does Not Need to Be Fun - Ignoring OWASP to Have a Terrible Time
Explore OWASP's free tools for web application security testing and implementation. Learn to identify issues early and integrate security best practices throughout the software development lifecycle.
Writing Secure JavaScript Code - Avoiding Vulnerabilities and Attacks
Learn secure JavaScript coding practices, including handling vulnerabilities, regular expressions, event loops, and input validation, to protect your applications from common attacks.
ATOR - Authentication Token Obtain and Replace Burp Plugin V3
Streamline complex authentication testing with ATOR v3 Burp Plugin. Automate token handling, OTP validation for JavaScript frameworks. Simplifies configuration and debugging for efficient security assessments.
Breaking and Fixing Web Application Security
Explore web application security challenges, attack vectors, and proactive measures. Learn to identify vulnerabilities, implement secure coding practices, and safeguard user data in the digital realm.
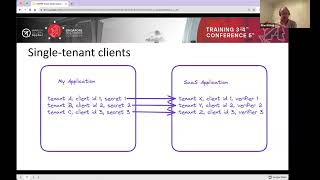
Cross-Tenant Request Forgery Attack in Multi-Tenancy Environments
Unveiling security vulnerabilities in multi-tenant SaaS platforms using OAuth, focusing on the "Cross-Tenant Request Forgery" attack and discussing potential remediations for developers.

HTTP Request Smuggling - Web Application Hacking Techniques
Explore HTTP Request Smuggling techniques for web application security, uncovering vulnerabilities and enhancing your hacking skills.
Enhancing ReactJS Application Security: Cross-Site Scripting and Client-Side Defense
Learn essential techniques to protect ReactJS applications from XSS attacks and other client-side vulnerabilities. Gain actionable strategies to enhance security and safeguard your projects.
OWASP Proactive Controls for Secure Application Development
Explore essential security practices for software development with OWASP Proactive Controls, presented by industry expert Jim Manico.
Web Security: Broken by Default?
Explore web security challenges, focusing on browser vulnerabilities and emerging standards to address these issues. Learn how developers can enhance application security beyond code fixes.