Stable 13 Tales From the Bug Mine Highlights from the Android VRP
Explore highlights from Android's Vulnerability Reward Program, uncovering critical security issues and their impact on mobile device safety.
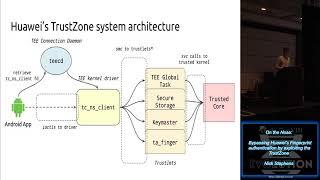
On the Nose - Bypassing Huawei's Fingerprint Authentication by Exploiting the TrustZone
Explore Huawei's TrustZone vulnerabilities and learn techniques to bypass fingerprint authentication through exploiting the secure environment and kernel.
New Wine in an Old Bottle - Attacking Chrome WebSQL
Explore Chrome WebSQL vulnerabilities and a mutation-based fuzzer for discovering SQLite bugs, enhancing web application security against remote attacks.
NVMe Technology in Cloud Service Providers
Discover a pre-auth remote vulnerability in Linux kernel's NVMe implementation. Learn open-source vulnerability research, static code analysis, and NVMe technology. Includes live demos and practical tips.
Introduction to Industrial Control Systems (ICS) Architecture and Security
Dive into industrial control systems fundamentals, architecture, and security research methods while learning to build and test your own ICS lab environment.

Hacking Millions of Modems and Investigating Modem Security Vulnerabilities
Dive into a real-world investigation of modem vulnerabilities, ISP security flaws, and the concerning centralization of broadband infrastructure through a personal hacking incident analysis.
Fuzzing Windows RDP Client for Vulnerabilities - A Research Journey
Explore Windows RDP client vulnerability research: from initial steps to uncovering remote code execution flaws. Learn about fuzzing tools, overcoming challenges, and recommendations for RDP security.
CertifiedDCOM - The Privilege Escalation Journey to Domain Admin with DCOM
Uncover a critical DCOM vulnerability allowing remote privilege escalation to Domain Admin in Windows networks. Learn about DCOM internals and exploit techniques for Active Directory takeover.
Blind VCC Glitching Technique to Bypass the Secure Boot of Qualcomm MSM8916 Mobile SoC
Explore a blind VCC glitching technique to bypass secure boot mechanisms on mobile SoCs, demonstrated on Qualcomm MSM8916/APQ8016. Learn practical application and see a live demo of this effective method.
Searching for RPC Functions to Coerce Authentications in Microsoft Protocols
Automated discovery of RPC functions in Microsoft protocols to find authentication coercion vulnerabilities, with focus on parsing documentation and generating proof-of-concept code.
Unwinding the Stack for Fun and Profit
Explore stack-based buffer overflow exploitation techniques, bypassing modern mitigations by leveraging exception handling mechanisms to resurrect old exploits and achieve successful attacks.
Outlook Unleashing RCE Chaos: Exploiting CVE-2024-30103
Dive into the critical Outlook security vulnerabilities, exploring remote code execution exploits through COM objects, NTLM leaks, and essential mitigation strategies for enterprise protection.
Vulnerability & Exploit Trends - A Deep Look Inside The Data
Explore vulnerability and exploit trends through data analysis, gaining insights into cybersecurity patterns and emerging threats in this comprehensive presentation by industry experts.
Analysis of Real World Apps with Frida
Discover how Frida enhances reverse engineering and vulnerability research for complex applications, boosting your cybersecurity skills and analysis capabilities.
How a Combination of Bugs in KakaoTalk Compromises User Privacy
Uncover critical security vulnerabilities in KakaoTalk messaging app, from account takeover exploits to encryption weaknesses, with practical demonstrations and analysis of protocol flaws.
Leveraging HTTP Request Smuggling for Authentication Bypass and Remote Code Execution
Delve into HTTP Request Smuggling vulnerabilities, exploring real-world cases of authentication bypass and remote code execution in enterprise applications, with practical detection and mitigation strategies.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.
Retro Exploitation - Vintage Computing as a Vulnerability Research Playground
Explore vulnerability research and exploit development through vintage computing, focusing on the Commodore Amiga platform and practical demonstrations of retro software exploitation techniques.
Nine Years of Overlooked MikroTik Pre-Authentication Remote Code Execution Vulnerabilities
Delve into RouterOS's overlooked attack surfaces and discover critical pre-auth RCE vulnerabilities that affected MikroTik devices for 9 years, with insights on detection methodology and security patterns.
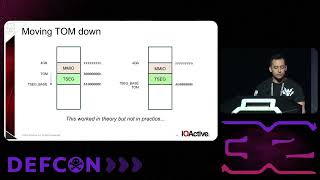
AMD Sinkclose - Universal Ring2 Privilege Escalation in System Management Mode
Delve into AMD processor security vulnerabilities, exploring System Management Mode (SMM), CPU design flaws, and the methodology behind ring-2 privilege escalation exploits.
QuickShell: Remote Code Execution Attack Chain Analysis in Quick Share
Uncover critical security vulnerabilities in Google's Quick Share protocol, including an RCE attack chain, HTTPS MITM techniques, and protocol analysis for both Windows and Android platforms.