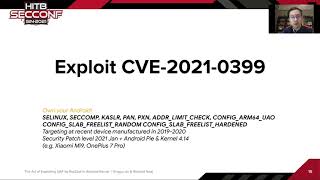
Exploiting UAF by Ret2bpf in Android Kernel
Exploiting a 10-year-old Use-After-Free vulnerability in Android's xt_qtaguid kernel module, demonstrating local privilege escalation on Mi9 device using ret2bpf technique to bypass protections.
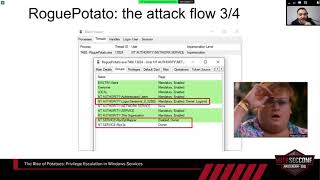
The Rise of Potatoes - Privilege Escalation in Windows Services
Exploring advanced privilege escalation techniques in Windows services, including a new 0day NTLM relay attack. Covers recent methods, Windows Service Hardening, and the RemotePotato0 attack vector.
Drammer - Deterministic Rowhammer Attacks on Mobile Platforms
Explore deterministic Rowhammer attacks on mobile platforms, uncovering vulnerabilities in modern devices and discussing potential security implications for mobile computing.
Bypassing Secure Boot Using Fault Injection
Explore fault injection techniques to bypass Secure Boot in embedded systems, focusing on hardware-based attacks when logical vulnerabilities are absent.
Black-Box Laser Fault Injection on a Secure Memory
Explore vulnerability research on the Microchip ATECC508A secure memory, examining laser fault injection techniques to bypass cryptographic authentication in IoT devices.

Fuzzing and Exploiting Virtual Channels in Microsoft Remote Desktop Protocol for Fun and Profit
Explore coverage-based fuzzing of RDP client virtual channels, targeting complex functionalities like Sound, Graphics, USB, and Filesystem to uncover potential vulnerabilities and crashes.
Project Zero - Five Years of Make 0Day Hard
Explore Project Zero's impact on cybersecurity, its core principles, and the need for such initiatives in the tech industry. Gain insights into vulnerability research and mitigation strategies.
Binee - Complete Emulation of Advanced Malware
Explore advanced malware emulation with Binee, a Windows Process emulator. Learn to create detailed memory models, mimic OS kernels, and gather dynamic analysis data for reverse engineering and vulnerability research.
Exploiting Unpatched iOS Vulnerabilities for Fun and Profit
Discover techniques for exploiting iOS vulnerabilities, including finding new attack vectors, chaining vulnerabilities, and defeating code signing to jailbreak the latest iOS version.
Digging for IE11 Sandbox Escapes Part 1
Explore IE11 sandbox vulnerabilities, focusing on logic bugs and Enhanced Protected Mode. Learn techniques to investigate, analyze, and exploit sandbox weaknesses in Windows 8.1.
Contemporary Automatic Program Analysis
Explore automatic program analysis techniques for vulnerability discovery, from historical context to cutting-edge methods, with practical examples and demos for effective security research.
Java Every-Days - Exploiting Software Running on 3 Billion Devices
Explore Java vulnerabilities, exploitation trends, and security measures in this Black Hat talk. Gain insights into common weaknesses, attack surfaces, and Oracle's responses to protect 3 billion devices.
Fixing - Making Holes in Binaries
Explore techniques for modifying binary files to fix vulnerabilities or create new exploits. Learn about reverse engineering and binary manipulation for security research.
Backdoor Lockpick
Reverse engineering and exploiting cryptographic backdoors in Phicomm routers, demonstrating vulnerabilities and developing tools for unauthenticated root access.
Ghidriff
Explore ghidriff, an open-source Python package for efficient binary diffing using Ghidra. Learn about its command-line interface, function matching heuristics, and markdown output for simplified patch analysis and vulnerability research.

From Patch to Pwnd
Learn to exploit vulnerabilities by analyzing security patches and reverse engineering, with techniques for identifying and leveraging weaknesses in software systems.
Changing What Game - One Future for Information Security
Explore the evolving landscape of information security, covering topics from FBI involvement to personal device vulnerabilities, and learn strategies for effective cybersecurity in various contexts.
Break Me09 Stagefright - Scary Code in the Heart of Android
Explore Android's Stagefright vulnerability, its impact on device security, and potential exploitation techniques in this in-depth analysis of a critical mobile security flaw.
Macs Get Sick Too
Explore Mac security vulnerabilities and threats, learning how to protect Apple devices from malware, exploits, and other cyber risks.
How to KickStart a Drone Jailbreaking Scene
Explore drone jailbreaking, vulnerability research, and counter-drone technologies with insights on ethical considerations and industry developments in unmanned aerial systems.
An Oral History of Bug Bounty Programs
Explore the evolution of bug bounty programs, from early disclosure policies to modern marketplaces, and their impact on cybersecurity and vulnerability research.