MIPS-X - The Next IoT Frontier
Explore MIPS-based IoT device research with a framework for efficient emulation, vulnerability analysis, and exploit development. Gain insights into CPU architectures, virtualization, and cross-compilation techniques.
Fuzzing RDP Client and Server
Exploring innovative techniques to fuzz RDP protocol using WinAFL, uncovering vulnerabilities in both client and server implementations for enhanced remote connection security.
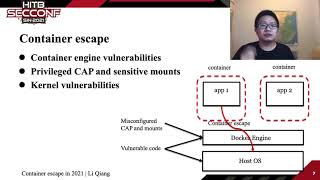
Container Escape in 2021
Explore new methods for escaping privileged runc containers, focusing on cloud security vulnerabilities and innovative exploit techniques in container environments.
Hacking K-12 School Software in a Time of Remote Learning
Análisis de vulnerabilidades en software educativo durante la pandemia, explorando ataques potenciales y sus implicaciones para la seguridad de dispositivos escolares y domésticos.
One Key To Rule Them All
Explore elliptic curve cryptography, Bitcoin wallets, and key management in this security researcher's talk on innovative cryptographic techniques and their applications.
Researching the Unisoc Baseband
Exploring Unisoc baseband security: reverse-engineering and fuzzing LTE protocol stack to uncover vulnerabilities in budget smartphone chipsets, disrupting radio communication.
Reverse Engineering of Black Box Binaries with Symbolic and Concolic Execution Technique
Explore symbolic and concolic execution techniques to simplify reverse engineering of complex binaries. Learn to use the angr framework for efficient crackme solving and deobfuscation.
Neurosurgery for Industrial Routers - Security of Sarian OS
Explore vulnerabilities in industrial routers, focusing on Digi WR21 and Sarian OS. Uncover internal workings, network protocols, and security features of critical infrastructure devices.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
Breaking Formation - From an Error Message to Internal AWS Infrastructure
Explore a critical AWS CloudFormation vulnerability, its impact on cloud security, and the disclosure process. Gain insights into cloud infrastructure vulnerabilities and future research directions.
Finding and Exploiting Bugs in TLS Libraries Used by Smart UPS Devices
Explore zero-click vulnerabilities in smart UPS devices, uncovering potential remote takeover risks and physical threats. Includes demonstration of exploits and discussion on cybersecurity implications.
Bug Hunter Adventures
Discover reconnaissance techniques and tools for finding vulnerabilities in Google's Vulnerability Reward Program. Learn from experienced bug hunters' journeys and insights into this coveted program.
Building Advanced Security Applications on Qiling.io
Explore Qiling.io's sandbox emulator framework for cross-platform binary analysis. Learn to build advanced security tools like fuzzers and malware analyzers using Qiling's flexible architecture and Python API.
Static Analysis-Based Recovery of Service Function Calls in UEFI Firmware
Discover a new tool for automated recovery of service calls and EFI type info in UEFI firmware, simplifying vulnerability hunting and making firmware code resemble original source.
Fuzzing - Finding Your Own Bugs and 0days
Aprende técnicas de fuzzing para descubrir vulnerabilidades y exploits de día cero. Incluye demostraciones prácticas de Buffer Overflow y creación de shellcode para pruebas de penetración.
SpeedPwning VMware Workstation
Discover the journey of reversing VMware Workstation vulnerabilities and developing a VM escape exploit in record time, offering insights into advanced security research techniques and time-pressured exploit development.
#EkoPodcast Episodio 2 | Hablamos con Dan Borgogno sobre vulnerabilidades en tecnología MiFare
Entrevista con Dan Borgogno sobre hallazgos de vulnerabilidades en sistemas SUBE y DNI Digital argentinos, destacando la importancia de reportar fallos de seguridad en tecnología MiFare.
Hacking the Pandemic's Most Popular Software - Zoom
Explore the vulnerabilities in Zoom discovered during Pwn2Own, including the process of finding and exploiting them to gain full control over a victim's system.
De 0 a millones de dólares en un par de paquetes
Descubre cómo vulnerabilidades recientes expusieron millones de dólares en Internet. Aprende sobre exploits públicos que amenazan a grandes empresas y cómo fueron descubiertos y explotados en solo 72 horas tras los parches.
A Journey Into Fuzzing WebAssembly Virtual Machines
Explore WebAssembly VM architecture, attack surfaces, and fuzzing strategies. Learn about bug discovery across multiple projects using various fuzzing techniques and frameworks.

Trace Me if You Can - Bypassing Linux Syscall Tracing
Novel vulnerabilities and exploitation techniques to bypass Linux syscall tracing, even with security measures like seccomp, SELinux, and AppArmor in place. Demonstrates how user-mode programs can evade detection.