DHS Supporting Critical Infrastructure Through Open-Source Software Prevalence Effort
Explore DHS's innovative methodology for identifying and assessing OSS in IT/OT devices, enhancing critical infrastructure cybersecurity through comprehensive vulnerability scoring and risk management.
Top Network Security Interview Questions - Scenario-Based Prep Series
Master scenario-based network security interviews with realistic questions on DDoS mitigation, unauthorized access prevention, VPN security, cloud protection, and more. Enhance problem-solving skills for job success.
Open-Source Vulnerability Management: Use the Source - DevSecOps 2022
Explore open-source vulnerability management techniques using source code analysis for effective security practices in DevSecOps environments.
Every Journey to Securing the Software Supply Chain Starts with a Single Step
Explore NYU's journey in software supply chain security, uncovering challenges, best practices, and a roadmap for enhancing software security.
Proactive Supply Chain Security with GUAC
Explore GUAC, a tool for proactive software supply chain security. Learn about its features, recent release, roadmap, and how to contribute to this OpenSSF project.
CVE Context Matters - Prioritizing Vulnerabilities in Cloud-Native Projects
Explore vulnerability scanning in cloud-native projects, learn to prioritize vulnerabilities, and implement effective scanners. Gain insights on assessing relevance and improving daily workflows.
Startup Security: From First Hire to Post-IPO - An Actionable Plan
Actionable strategies for building and scaling security in startups, from initial hire to post-IPO, with practical advice for thriving as a small security team.
Securing the Gateway and Mitigating Risks in LLM API Integration
Explore strategies for safeguarding LLM API integrations, addressing security vulnerabilities, and implementing robust risk mitigation measures in AI-powered applications.
OWASP DefectDojo - Introduction and Overview
Learn about DefectDojo, an open-source application vulnerability management tool. Discover its features for streamlining security testing workflows and enhancing vulnerability tracking and remediation processes.
Start Covering Your Bases and Stop Chasing APT Headlines
Learn effective cybersecurity strategies to protect against common threats, moving beyond headline-grabbing APTs to focus on fundamental security practices and risk mitigation.
Discovering Hidden Vulnerability Intelligence in CISA's KEV Catalog
Uncover hidden insights in CISA's KEV catalog for effective vulnerability prioritization. Explore exploit intelligence to enhance cybersecurity strategies across industries.
Beyond Whack-a-Mole: Scaling Vulnerability Management by Embracing Automation
Explore automated, risk-oriented vulnerability management strategies using SBOM, CSAF, and VEX to streamline processes and align remediation with genuine risk impacts.
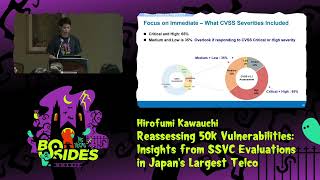
Reassessing 50,000 Vulnerabilities: Insights from SSVC Evaluations in Japan's Largest Telco
Practical vulnerability prioritization using SSVC: Insights from evaluating 50k+ vulnerabilities in Japan's largest telco, improving efficiency and effectiveness over CVSS-based approaches.
Open Source Vulnerability Management for Software Development and Cloud Environments
Explore open source vulnerability management strategies for software development and cloud environments in this IT security conference talk by Stefan Fleckenstein at TROOPERS24.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.
Step-by-Step: Application Security Architecture
Comprehensive guide to application security architecture, covering threat modeling, security controls, and best practices for robust software design and implementation.
The Magic of Application Security Posture Management and Its Future Frontier
Explore ASPM's role in fortifying application defenses, from proactive risk mitigation to predictive analytics, and its future potential with AI and blockchain integration.
OSV and the Life of an Open Source Vulnerability
Explore OSV's role in simplifying open source vulnerability management throughout the software development lifecycle, from database creation to guided remediation.
Intel's Experiences Using OpenSSF Scorecard to Better Secure Software Portfolio
Explore Intel's use of OpenSSF Scorecard to assess and mitigate software risks across their vast portfolio, learning from their experiences and challenges.
Secure Software Supply Chain at IBM
Explore IBM's approach to securing the software supply chain, focusing on key strategies and best practices for enhancing cybersecurity in development processes.
Supply Chain Security with KubeClarity: Introduction and Implementation
Explore supply chain security fundamentals, historical attacks, and KubeClarity tool. Learn about SBOMs, their benefits, and see KubeClarity in action for enhanced software security.