How to Generate VEX Automatically for Your Project
Learn to automate VEX generation for Kubernetes workloads, reducing false positives in security scans and streamlining vulnerability management using Kubescape and a new GitHub Action.
Cyber Resilience Act Impact on Device Manufacturers
Explore the Cyber Resilience Act's impact on device manufacturers, focusing on cybersecurity requirements, vulnerability management, and compliance strategies.
Managing Vulnerabilities in Open-Source Dependencies
Learn strategies to secure open-source dependencies, evaluate software composition analysis tools, and shift from reactive to proactive security postures in product development.
Increase Security Posture in Software Delivery with Red Hat Trusted Software Supply Chain
Enhance software security with Red Hat's Trusted Supply Chain: protect components, predict vulnerabilities, and improve resilience through advanced tools and practices.
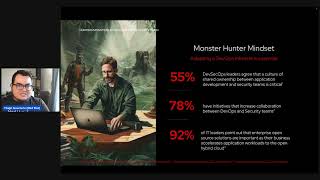
Hunting Down the Monsters Hidden in Your Software Supply Chain
Uncover and mitigate hidden threats in your software supply chain. Learn effective strategies to enhance security and protect against vulnerabilities.
Hyades - Dependency Track for Enterprise Supply Chain Security with SBOM
Enhance enterprise supply chain security using Dependency Track with SBOM in Hyades, a powerful tool for managing software dependencies.
Security Keynote - Open Source Software and Cybersecurity
Explore cybersecurity insights and strategies with Dr. Allen Friedman's keynote address on critical security challenges and solutions in the digital landscape.
Do No Harm: OT-Native Approach for Network Monitoring and Cybersecurity
Explore seven principles of OT cyber-network visibility and monitoring for effective cybersecurity in industrial environments. Learn to implement a tailored approach that protects critical infrastructure while maintaining operational integrity.
Demystifying SBOMs: Strengthening Cybersecurity Defenses
Explore Software Bill of Materials (SBOMs) as a crucial tool for enhancing cybersecurity, identifying vulnerabilities, and managing software supply chain risks in organizations.
Managing Vulnerability Overload with OWASP Tools and Strategies
Discover OWASP's strategies for managing overwhelming security vulnerabilities, enhancing your ability to prioritize and address critical threats effectively.
OWASP Dependency Track - Fortifying the Software Supply Chain
Explore strategies to secure software supply chains using OWASP Dependency Track, a powerful tool for identifying and mitigating vulnerabilities in third-party components.
The Internet is Broken: Breaking Down the Software Supply Chain
Explore modern software vulnerabilities, recent supply chain attacks, and actionable steps to build secure applications in an insecure internet environment.
Dev Ally, Zero-Days Foe - DefCamp Cluj-Napoca 2024
Explore cutting-edge cybersecurity insights with Ali Abdollahi's presentation on developer-friendly approaches to combat zero-day vulnerabilities at DefCamp Cluj-Napoca 2024.
From an OSS-Fuzz Report to LKML Patch Submission - A Hands-on Journey
Hands-on guide to fixing vulnerabilities using OSS-Fuzz reports, from debugging to submitting patches to the Linux Kernel Mailing List. Learn to contribute to open source projects and improve software quality.
Open Software Supply Chain Attack Reference (OSC&R) - OWASP Foundation
Explore the OSC&R framework for software supply chain security, analyzing real-world attacks and improving DevSecOps programs to enhance overall security posture.
Secure Systems from Insecure Components
Explore innovative cryptographic approaches to build resilient systems that withstand compromises, offering practical solutions for authentication and data protection in today's vulnerable digital landscape.
Practical SBOM Management with Zephyr and SPDX
Learn to identify, assess, and manage software components in Zephyr applications using SBOM standards and tools. Enhance security practices and respond effectively to vulnerabilities in embedded systems.
Effective Vulnerability Management for Over 400 Projects at the Eclipse Foundation
Discover how Eclipse Foundation streamlines vulnerability management across 400+ projects, enhancing security practices and reporting processes for researchers and developers.
What Makes a Project Critical? Discovering and Evaluating Popular Open Source Software
Discover criteria for evaluating critical open source projects and learn to assess their impact on infrastructure and society.
OSS-SIRT - Identify Core Services 2
Explore essential core services for open source security incident response teams, enhancing your ability to manage and mitigate security threats effectively.
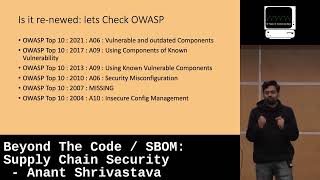
Beyond the Code - SBOM and Supply Chain Security
Explore supply chain security, focusing on Software Bill of Materials (SBOM) and its role in enhancing software transparency and risk management in modern development practices.