How Using Open Source Code Can Leave You Exposed to Hackers
Explore the security risks of open-source code, focusing on the Log4Shell vulnerability and its widespread impact on applications.
Securing the Software Supply Chain: Challenges and Solutions
Learn strategies to secure the software supply chain against attacks, prioritize security measures, and protect your organization from catastrophic data breaches.
Five and a Half Actions to Mitigate Software Supply Chain Threats
Discover five crucial actions to protect your software supply chain from threats, including insights from Commerzbank's use of Google Cloud's Assured OSS.
The Ownership Battle Between Engineering and InfoSec
Explore the ownership dynamics between Engineering and InfoSec teams in DevSecOps, focusing on effective result consumption and action implementation.
DevSecOps Unveiled: Integrating Security in the Development Lifecycle
Explore DevSecOps principles and practices for seamlessly integrating security into the development lifecycle. Learn to foster collaboration, automation, and shared responsibility for proactive vulnerability management.
Software Supply Chain Security - Key Terms, Players, and Projects - Part 2
Explore key terms, players, and projects in software supply chain security. Gain insights on open-source visibility, SBOMs, and initiatives addressing complex security challenges in the open-source pipeline.
Software Supply Chain Security: Definition and Importance - Episode 1
Explore the key pillars of software supply chain security in this comprehensive podcast episode. Gain insights into problem definition, essential terms, and practical implementation strategies for enhancing your organization's security posture.
Defense in Depth: Refocusing on Defensive Security Techniques
Explore defensive product security techniques, emphasizing defense-in-depth and supply chain security. Learn key aspects to consider in your application security strategy.
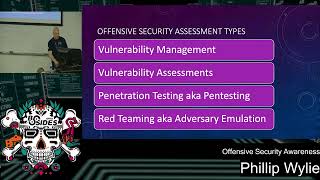
Offensive Security Awareness: Understanding Assessment Types and Methodologies
Demystify offensive security techniques, tools, and assessment types. Gain insights into vulnerability management strategies and learn to choose the right approach for your organization's security needs.
The Iceberg - How to Mitigate Risks in Your OSS Projects
Explore strategies to mitigate risks in open-source software projects and understand the expanding attack surface in modern development environments.
Open Source Supply Chain Security for Enterprises
Explore enterprise-level open source supply chain security strategies with insights from JPMorgan Chase's Product Security Director.
The Myriad Paths to Improving Open Source Security
Explore diverse approaches to enhance open source security with expert insights from Rory McCune at SOOCon23 Security.
Do You Know the Health of Your OSS Dependencies? Introducing OSSF Scorecard API
Explore the OSSF Scorecard API to assess and improve the health of your open-source software dependencies, enhancing overall security.
Modelling Threats Out in the Open Source - SOOCon23 Security
Explore open-source threat modeling techniques to enhance software security and identify potential vulnerabilities in your projects.

Improving FOSS Security
Explore Canonical's security maintenance process and learn strategies for FOSS projects to enhance vulnerability management and disclosure.
CVE Triage, CVE Checker Analysis, and Vendor PR in Yocto Project Security - YPS 2023.11
Explore CVE triage initiatives, SRTool enhancements for CVE Checker analysis, and potential "vendor_pr" system to address package patching recognition in Yocto Project security.
Yocto Project Security: Now and the Future - YPS 2023.11
Explore Yocto Project's 2023 security updates and upcoming 2024 features, including CVE scanning, SBOM generation, and default options.
Hitchhikers' Guide to the Vulniverse
Explore key elements of vulnerability disclosure and management, including CVE, CVSS, CWE, and VEX. Gain insights into communication between security teams and researchers.
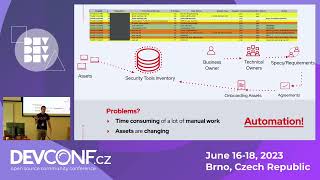
Development of Asset Mapping External Attack Tool
Explore an in-house tool for unified asset visibility, vulnerability mapping, and attack surface analysis in complex multi-cloud environments, tailored for Red Hat standards.
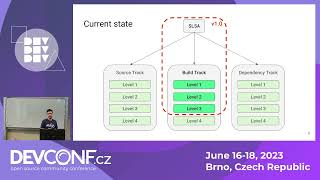
SLSA - A Supply Chain Security Framework
Explore SLSA framework for securing software supply chains, mitigating vulnerabilities, and ensuring code integrity from development to deployment.
The Cyber Resilience Act: Navigating Its Impact on Yocto-Based Products
Explore the Cyber Resilience Act's impact on Yocto-based products, covering key provisions, security compliance, challenges, and best practices for building secure embedded systems.