Embrace the Differences: Securing Open Source Ecosystems Where They Are
Explore efforts to fix the libwebp vulnerability in Python packages, examining interactions between security standards and open source ecosystems.
SBOMs Everywhere - Work in Progress and Challenges Ahead
Explore the progress and challenges of Software Bill of Materials (SBOMs) implementation across industries with insights from a leading expert in dependable embedded systems.
SBOM Everywhere - Understanding Software Bill of Materials
Explore the importance of Software Bill of Materials (SBOM) in securing open source supply chains and learn about its widespread implementation.
What's New in the World of SBOMs?
Explore recent developments in Software Bill of Materials (SBOMs) with industry experts, discussing advancements, challenges, and best practices in software supply chain security.
Matching CVEs and Source Code for Vulnerability Detection
Explore techniques for mapping CVEs to source code, including parsing CVE data and quantifying correspondence statistics. Learn about open-source tools and potential AI applications for vulnerability detection.
An Acronym-Free Introduction to Software Supply Chain Security
Explore principles and practices for securing software supply chains without jargon. Learn about open-source projects, standards, and common terms to enhance your understanding of this rapidly evolving field.
Protecting Your Organisation Against Attacks via the Build System
Explore build system security risks and mitigation strategies, including dependency verification, checksums, vulnerability detection, and build reproducibility. Learn to safeguard your development process.
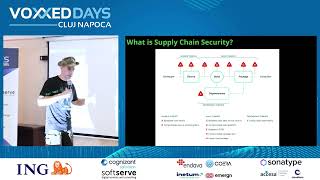
Supply Chain Security for OpenSource Projects
Explore supply chain security for open-source projects, covering potential threats, attack points, free tools, and strategies to protect against cyber attacks in software development.
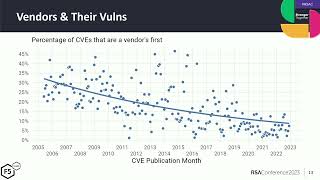
The Evolution of CVEs, Vulnerability Management, and Hybrid Architectures
Explore new research on vulnerabilities, including CVE trends, severity, and exploit code sharing. Learn about implications for vulnerability management in hybrid and multicloud architectures.
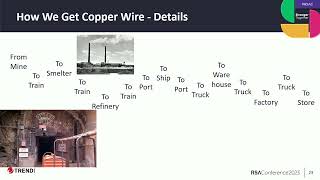
Responding to Supply Chain Vulnerabilities – A Maritime Perspective
Explore cybersecurity risks in ports and shipping, analyzing vulnerabilities and discussing potential solutions for improved detection and response in maritime infrastructure.
Collaborative Penetration Testing With Lair
Explore collaborative penetration testing using Lair, a tool for efficient teamwork in security assessments. Learn about vulnerability management, commands, and scripting for enhanced testing workflows.
GitHub Actions - Vulnerabilities, Attacks, and Counter-measures
Explore GitHub Actions vulnerabilities, attacks, and countermeasures. Learn about runner risks, potential misuse by attackers, and security measures to protect your CI/CD pipeline.
What Is Going On In Your Source Code? Understanding Software Component Analysis in Plain Language
Gain insights into software supply chain security concepts like SBOM, VEX, and SLSA, understanding their importance in protecting organizations from emerging security threats.
Novel Sandboxing Techniques for Open Source Libraries Using eBPF and KRSI
Discover how to implement advanced sandboxing techniques for open source libraries using eBPF and KRSI technologies to enhance security and protect against vulnerabilities and exploits.
Understanding Linux Kernel CVEs and Their Recent Surge
Understand how the Linux kernel community manages CVE assignments, their new structured approach to vulnerability reporting, and best practices for handling security updates.

Use Cases for Digital Twin Technology in Multi-Cloud and Hybrid Environments
Discover how network digital twins enable multi-cloud visibility, service assurance, and automated compliance while enhancing vulnerability management and end-to-end network control.
Make Better Risk Decisions to Prevent Future Cyber Attacks
Discover proactive cybersecurity strategies for better risk decisions, focusing on preventative measures over reactive controls. Learn to identify vulnerabilities, assess business impact, and implement effective risk mitigation techniques.
Complexity for Complexity's Sake: The Bane of Cybersecurity Programs
Discover how to simplify cybersecurity approaches by avoiding tool overload and focusing on effective, streamlined solutions for better threat management and user experience in modern security programs.
Everything You Didn't Want to Know About CVE - Understanding Vulnerability Disclosure Challenges
Dive into the complexities of vulnerability disclosure and CVE processes, exploring recent events that highlight systemic issues and their impact on security professionals' ability to manage threats effectively.
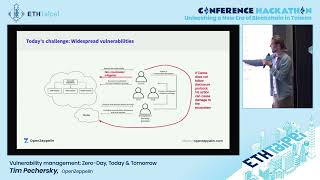
Vulnerability Management: Zero-Day, Today and Tomorrow
Dive into modern vulnerability management strategies, exploring zero-day threats and future security challenges in blockchain systems with insights from OpenZeppelin's expertise.
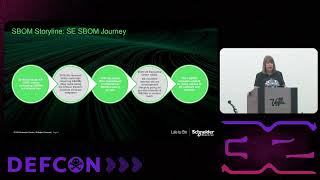
The Missing Link: How to Collect and Leverage Software Bill of Materials (SBOMs)
Discover how Schneider Electric efficiently manages software security through SBOM collection and implementation, with real-world examples from Log4j and OpenSSL vulnerability responses.