
The Darkest Side of Bug Bounty - Understanding Problems and Solutions in Bug Bounty Programs
Uncover the hidden challenges, secrets, and realities of bug bounty programs through expert insights on navigating relationships between hunters, clients, and platforms.
Secure Your Stack with Ubuntu
Explore Ubuntu's security features, vulnerability management, and enterprise-grade support for secure open-source adoption. Learn how Linux distributions protect systems from threats.
Everything Old Is New Again - Protecting Legacy Systems with Modern Security
Explore strategies for securing legacy systems in critical infrastructure when modern security practices are unavailable. Learn to integrate older technologies into a robust security posture.
Securing Your Supply Chain with an Open Source Ecosystem
Explore open-source tools and best practices for securing software supply chains across creation, build, deployment, and runtime stages. Learn to leverage automation and DevSecOps to reduce vulnerabilities.
Mastering Web Security - Myths, Strategies and Challenges
Debunking security myths and exploring effective strategies for web application protection. Practical insights on vulnerabilities, defense mechanisms, and organizational approaches to enhance cybersecurity.

Vulnerability Management in the World of AI
Explore AI and LLM security, ensuring ethical adherence and robust protection for your organization's AI models and deployments.
From Standards to Practice: The Journey to Container Maturity
Discover how Yelp manages container security at scale, from implementing vulnerability tracking to developing maturity models that guide thousands of engineers in maintaining robust Docker and Kubernetes deployments.
Strategies for Patching Critical CVEs in Open Source Software - Best Practices and Tools
Master strategies for handling critical CVEs in open source packages, from patching container images with Copacetic to building projects from scratch, while learning best practices for software supply chain security.
Working Together to Improve Security Visibility in Kubernetes
Discover how Kubernetes security teams collaborate on CVE management, dependency vulnerabilities, and release processes while exploring future improvements for enhanced security visibility across the platform.
Exploring ChatGPT's Capabilities on Vulnerability Management
Explore ChatGPT's effectiveness in vulnerability management through comprehensive analysis of 6 key tasks, examining its potential and limitations in security-related code analysis.
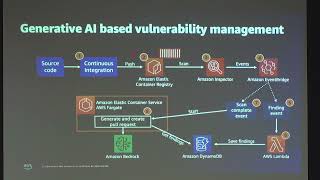
Applying Generative AI to Container CVE Remediation in CI Pipelines
Discover how to leverage generative AI for automating container vulnerability remediation in CI pipelines, with practical demonstrations and implementable solutions for efficient security management.
Strengthening Defenses Against CI/CD Security Threats - Understanding and Mitigating Pipeline Vulnerabilities
Dive into essential CI/CD pipeline security, exploring OWASP's top risks, attack methodologies, and practical defense strategies to fortify your development infrastructure.
Risk-Based Vulnerability Management for Cloud Networks - A Proof of Concept on Vulnerability Prioritization Model
Explore an AI-powered vulnerability prioritization model for cloud networks that reduces remediation workload by 3x through intelligent risk assessment and threat analysis.
ONAP's Recipe for Managing CVEs and Securing Open Source Software
Discover ONAP's effective strategies for managing CVEs, securing open-source dependencies, and implementing automated vulnerability management processes in software development.
Secure and Govern Custom AI Built on Azure AI and Copilot Studio
Discover essential strategies for securing and governing custom AI applications, focusing on data security, compliance controls, vulnerability management, and protection against emerging AI threats.
Beyond Manual: Enhancing and Scaling Security with Automation
Discover how to scale security operations through automation, focusing on practical strategies and tools to enhance your organization's security posture efficiently.

Fortifying AIOps with CSAF and VEX Integration for Enhanced Security Management
Discover how to enhance AIOps security through CSAF and VEX integration, enabling real-time vulnerability management and improved threat response for server and storage infrastructure.
Strengthening Supply Chain Security - A DevSecOps Perspective
Explore modern supply chain security challenges and solutions through DevSecOps principles, focusing on emerging threats, operational complexities, and practical defensive strategies for today's digital landscape.
Future Use of SCAP and SBOM for Software Supply Chain Security
Explore the comparison between SCAP and SBOM methodologies for enhancing software supply chain security, understanding their features and future applications in risk management.
Linux Distributor's Role for Supply Chain Security
Explore how Linux distributions can enhance software supply chain security through centralized access, trusted SBOM delivery, and improved vulnerability management mechanisms.
Maturing Your Application Security Program - A Practical Guide to Next Steps
Discover practical steps to advance your AppSec program through three maturity levels, with actionable strategies for immediate security posture improvements based on experience with 300+ companies.