Fortify Your Code: Secure Your Supply Chain with Scorecard
Discover how to assess and strengthen open-source software security using Scorecard, gaining practical insights into dependency risk management and implementing robust supply chain protection measures.
Back to Security Basics: Evaluating, Consuming, and Contributing Open Source Software
Discover essential strategies for evaluating and securing open source software through maintenance assessment, vulnerability management, and community engagement practices for safer implementation.
Phantom Dependencies in AI and ML Projects - Managing Hidden Software Dependencies
Discover how phantom dependencies impact AI/ML projects and learn effective strategies for identifying, managing, and securing these hidden software dependencies in your applications.
Lessons Learned on Following Security Best Practices in Zephyr
Discover how the Zephyr project implemented security best practices in IoT, including CVE management, PSIRT team formation, and vulnerability handling over 8 years of open-source development.
Secure Code, Safe Future: Mastering Security in Critical Software Development
Discover practical secure coding techniques and strategies for developing robust software, including vulnerability management, SBOM implementation, and hands-on security practices for critical infrastructure projects.
Closed Loop Vulnerability Mitigation - Automated OS Updates and Patch Management
Discover automated OS upgrades and patch management strategies with integrated vulnerability intelligence and risk scoring for enhanced network security management.
Security in Google Kubernetes Engine - GKE Security Posture and Threat Detection
Discover how Google Cloud enhances Kubernetes security through automated vulnerability management, threat detection, and compliance tools, making complex environments safer and more manageable.
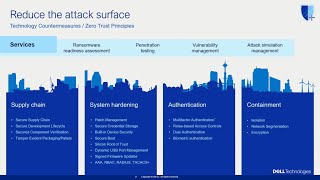
Reducing the Attack Surface: Cybersecurity Strategies and Best Practices
Discover effective strategies and best practices for minimizing cybersecurity vulnerabilities, from silicon root of trust to endpoint security and supply chain management.
Recovery from Firmware Vulnerabilities in TPM - Securing Hardware Roots of Trust
Discover how new TPM specification APIs enable firmware vulnerability recovery and self-attestation capabilities, enhancing hardware security and trust restoration mechanisms.
Maturing Your Application Security Program - A Practical Guide to Next Steps
Discover practical steps to advance your AppSec program through three maturity levels, with actionable strategies for immediate security posture improvement based on experience with 400+ companies.
Using EPSS for Better Vulnerability Management
Discover how to implement EPSS for vulnerability management, leveraging data-driven insights to predict and prioritize exploit risks in CI/CD pipelines and system patching processes.
Handling Security Vulnerabilities in Eclipse Projects - A Guide for Project Maintainers
Learn how to effectively handle security vulnerabilities in your projects, from initial reporting through resolution, using Eclipse Foundation's processes and new security management tools.
Understanding Software Component Analysis (SCA) in Plain Language
Gain insights into software supply chain security concepts like SBOM, VEX, and SLSA, demystifying their importance for protecting organizational assets and code integrity.
What it Takes to Patch High Impact Vulnerabilities: A Retrospective on WebP CVE
Explore WebP CVE vulnerabilities in Flutter, assess impact across Android apps, and learn effective strategies for staying updated and implementing robust security measures.
Cracking the Code of Cloud Security - DevSecOps and Container Security
Explore cloud security challenges, container vulnerabilities, and DevSecOps strategies. Learn automated vulnerability management, configuration best practices, and network segmentation for enhanced protection.
Mapping the Minefield of Open Source Software Risks - DevOps 2024
Explore open source software risks, vulnerabilities, and remediation strategies. Learn about software composition analysis, reachability, and semantic versioning for effective dependency management.
SBOMs Go Global: Current State and Emerging Trends
Explore the global impact and emerging trends of Software Bill of Materials (SBOMs) with insights from industry expert Kate Stewart.
Secure Your Software Supply Chain with Go
Learn to detect and remediate vulnerabilities in Go dependencies using the new vulnerability management system, enhancing software supply chain security.
Ensuring Cloud Resource Health: Addressing Software Vulnerabilities and Identity Risk
Learn to address software vulnerabilities and identity risks in cloud environments using Security Command Center's new capabilities for strengthening overall risk posture.
SBOM: The Inescapable Way of Tracking Dependencies
Explore SBOM's role in preventing cyber-attacks, its formats, and implementation across the software development lifecycle. Learn to generate, manage, and monitor SBOMs for enhanced security.
Cover Your Apps: The Three Pillars of Application Security
Explore the three foundational pillars of Application Security (AppSec) to enhance your software development practices and create safer solutions.