OSTrICa - Open Source Threat Intelligence Collector
Explore OSTrICa, an open-source framework for automated threat intelligence collection and visualization. Learn about its plugin-oriented architecture and applications in cybersecurity and incident response.
Lessons Learned from the CISA COVID Task Force & Healthcare Attacks
Insights from CISA's COVID Task Force and healthcare cybersecurity efforts, exploring challenges, strategies, and lessons learned in protecting critical infrastructure during the pandemic.
What Does an LLM-Powered Threat Intelligence Program Look Like?
Explore the impact of large language models on cyber threat intelligence programs, focusing on expanded capabilities and potential return on investment for organizations.
SOC Panel Keynote
Explore insights from security operations center experts in this panel discussion, covering best practices, challenges, and emerging trends in cybersecurity management.
Of Flags, Frogs, 4chan, OPSec vs Weaponized Autism
Explore the clash between online anonymity and collective intelligence in 4chan communities, examining OPSEC strategies and the power of crowdsourced investigations.
RBN Reloaded - Amplifying Signals from the Underground
Explore how combining SIGINT and HUMINT enhances threat intelligence, providing deeper insights into adversary tactics, intent, and vulnerabilities for improved cybersecurity decision-making.
Catching Malware En Masse - DNS and IP Style
Innovative strategies to detect and mitigate malware at DNS and IP levels, including botnet tracking, AS graph analysis, and IP range investigation. Includes a 3D visualization engine for effective threat intelligence.
Threat Intelligence Library - A New Revolutionary Technology to Enhance the SOC Battle Rhythm
Explore the evolution of cyber threat intelligence and its impact on SOC operations. Learn about threat libraries, their importance in managing IOCs, and strategies for enhancing adversary hunting workflows.
The New Scourge of Ransomware - A Study of CryptoLocker and Its Friends
Explore the evolution of ransomware, focusing on CryptoLocker and its impact. Learn about threat intelligence responses, infrastructure tracking, and lessons for managing emerging cyber threats.
From Attacks to Action - Building a Usable Threat Model to Drive Defensive Choices
Translating threat intelligence into actionable defensive strategies using community-driven approach. Explores evolution of threat modeling and its integration with risk management frameworks.
End-to-End Analysis of a Domain Generating Algorithm Malware Family
Comprehensive analysis of a Domain Generating Algorithm malware family, covering deobfuscation, DGA analysis, sinkholing, and attribution of the malware's author and accomplices.
Z - MAKE TROY NOT WAR - Case Study of the Wiper APT in Korea, and Beyond
Análisis detallado del ataque "Wiper" en Corea del Sur en 2013, explorando el vector de infección inicial, examinando muestras de malware y estableciendo conexiones con otros casos de APT desde 2009.

State of the Onion - Security Onion Conference 2019
Explore the latest developments and future roadmap of Security Onion, a powerful open-source security monitoring platform, presented by its creator at the annual conference.
Multiplying Threat Intelligence
Strategies for maximizing threat intelligence to enhance cybersecurity defenses, focusing on creative approaches to generate and apply intelligence for breakthrough discoveries in attack detection.
Collecting Underpants to Win Your Network
Discover strategies for network penetration testing, focusing on information gathering techniques and exploiting vulnerabilities to gain unauthorized access.
Exploiting the Zeroth Hour - Developing Your Advanced Persistent Threat to Pwn the N
Explore advanced persistent threat development techniques to enhance your cybersecurity skills and understand sophisticated attack methodologies for improved network defense.
Developing an Open Source Threat Intelligence Program
Learn to build an open-source threat intelligence program with expert insights on gathering, analyzing, and utilizing cybersecurity data to enhance organizational defenses.
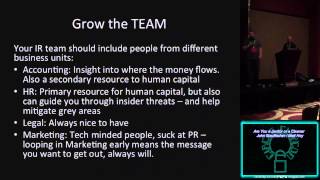
Are You a Janitor or a Cleaner
Explore incident response lifecycle, attack patterns, and effective strategies for cybersecurity preparedness and response in this insightful presentation on organizational security challenges.
Open Source Threat Intelligence - Developing a Threat Intelligence Program Using Open Source Tool
Develop a comprehensive threat intelligence program using open-source tools. Learn to identify potential threats, enhance monitoring, and implement effective incident response strategies.
Seeing Purple - Hybrid Security Teams for the Enterprise
Explore hybrid security teams for enterprises, covering red teaming, blue teaming, and purple teaming strategies to enhance threat detection and response capabilities.
Real World Threats
Explore real-world cybersecurity threats and defense strategies with expert insights from Russ Ward's presentation at BSides Huntsville 2015.