How I've Broken Every Threat Intel Platform and Settled on MISP
Exploring challenges in threat intelligence platforms and advocating for event-based approaches. Discusses experiences with various systems and settling on MISP for effective correlation and analysis of cyber threats.
MISP Introduction and New Features - 2017 Summit
Introduction to MISP and its latest features, exploring threat intelligence sharing capabilities, data models, and collaborative analysis tools for improved cybersecurity.
MISP New Features and Development Evolution - 2016 Summit
Explore MISP's latest features and development progress in this presentation by Andras Iklody from CIRCL, highlighting advancements in threat intelligence sharing and analysis.
Meet Operational Challenges with MISP on an Air-Gapped Network
Explore strategies for implementing MISP on air-gapped networks to address operational challenges in secure environments.
Visualizing Threat Intelligence: MISP to Power BI Integration
Explore MISP to Power BI integration for enhanced threat intelligence visualization and analysis, empowering cybersecurity teams with actionable insights.
MISP Workflow - An Improved Way to Support CTI Pipelines
Enhance CTI pipelines with improved MISP workflow techniques. Learn efficient strategies for threat intelligence management and streamline your cybersecurity processes.
Introducing HAMISPA - High Availability MISP in AWS
Learn to deploy a highly available MISP (Malware Information Sharing Platform) in AWS for enhanced threat intelligence sharing and collaboration.
WHIDS Integration with MISP
Explore WHIDS integration with MISP for enhanced threat intelligence sharing and incident response capabilities in cybersecurity operations.
The New Indicator Scoring Method Introduced in MISP 2.4.116
Explore the updated indicator scoring system in MISP 2.4.116, enhancing threat intelligence analysis and improving decision-making for cybersecurity professionals.
Visualizing MISP and ATT&CK Data in Maltego
Explore techniques for visualizing threat intelligence data from MISP and ATT&CK frameworks using Maltego, enhancing cybersecurity analysis and decision-making.
MISP Project - One Year of Improvements
Explore recent advancements in the MISP threat intelligence platform, including enhanced features, improved performance, and expanded capabilities for cybersecurity professionals.
Central Intelligence Vetting Platform - MISP Summit 2018
Explore the Central Intelligence Vetting Platform presented at MISP Summit 2018. Learn about innovative approaches to intelligence analysis and information sharing in cybersecurity.
Quantitatively Comparing APTs with MISP - MISP Summit 2018
Explore quantitative methods for comparing Advanced Persistent Threats using MISP, enhancing threat intelligence analysis and cybersecurity strategies.
Master of Clusters - MISP Summit 2018
Explore advanced clustering techniques for threat intelligence data analysis and visualization in MISP, enhancing cybersecurity insights and decision-making processes.
From Twitter to MISP - Catching and Qualifying IOCs
Explore a method for capturing and qualifying Indicators of Compromise (IOCs) from Twitter and integrating them into MISP for enhanced threat intelligence.
Building a Security Ecosystem with MISP and McAfee
Explore the integration of MISP and McAfee technologies to enhance threat intelligence sharing and create a robust security ecosystem for improved cybersecurity.
The Holy Grail for STIX and MISP Format - MISP-STIX
Explore MISP-STIX integration for enhanced threat intelligence sharing, focusing on data conversion and interoperability between MISP and STIX formats.

CTI Operational Procedures with Jupyter Notebooks and MISP
Learn to enhance Cyber Threat Intelligence operations using Jupyter Notebooks and MISP. Explore practical techniques for data analysis, visualization, and threat information sharing.
MISP Updates - Hack.lu 2023
Explore the latest updates and enhancements to MISP, the open-source threat intelligence platform, presented by Andras Iklody at Hack.lu 2023.
Connecting CTI and SOC Teams - MISP42
Explore strategies for bridging the gap between Cyber Threat Intelligence and Security Operations Center teams, enhancing collaboration and threat response capabilities.
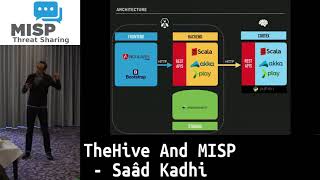
TheHive and MISP
Explore TheHive and MISP integration for enhanced threat intelligence sharing, analysis, and incident response capabilities in cybersecurity operations.