The Log4J Rollercoaster - From an Incident Response Perspective
Insights from the frontlines of Log4J incident response: preparing for unknown vulnerabilities, leveraging threat intelligence, and aiding the community during a major cybersecurity crisis.

SOARing with Security Onion
Explore how Security Onion integrates with automation tools for enhanced incident response, enabling faster threat detection and improved security operations efficiency.
The Future of Security Isn't Preventing Attacks
Explores shifting security focus from prevention to detection and remediation. Discusses building threat intelligence and preparing for inevitable system compromises.
Droned Out - Surveilling the Noise in the Russian War in Ukraine
Explore the evolving cybercriminal landscape since Russia's invasion of Ukraine, analyzing threat actor activities and dark web engagements to provide measurable insights on current and future trends.
REvil - Riches to Rags – The Rise and Takedown of a Cybercrime Empire
Explore the rise and fall of REvil, a notorious ransomware group, through years of research. Learn about cybercriminal empire building, takedown processes, and the impact of public/private partnerships in combating ransomware.
When Everything Is Critical, Nothing Is - ISA and Mitigation Prioritization
Learn Infrastructure Susceptibility Analysis (ISA) to prioritize cyber vulnerabilities and focus mitigation efforts on critical weaknesses most likely to be exploited, enhancing organizational security.
Profiling Malicious Actors
Explore techniques for identifying and understanding malicious actors in cybersecurity, including profiling methods, frameworks, and analytical tools for threat assessment.
DarkComet From Defense To Offense - Identify Your Attacker
Explore DarkComet's vulnerability to gain insights into attacker campaigns, extract valuable information, and potentially identify the attacker's personal details and infrastructure.
Connecting the Dots - A Beginner's Experience of Threat Actor Tracking
Explore threat actor tracking through a beginner's perspective, covering setup, tools, and techniques for identifying and analyzing malicious activities.
The Work of Cyber in the Age of Mechanical Reproduction
Explore how advanced threat actors systematize and scale malware operations, and learn to analyze relationships between campaigns, malware families, and threat actors in this cybersecurity deep dive.
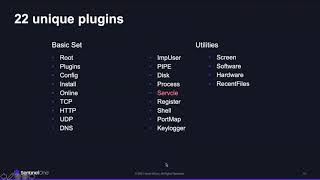
SHADOWPAD - Chinese Espionage Malware-as-a-Service
Comprehensive analysis of SHADOWPAD malware: its origin, usage patterns, and business model. Explores its impact on Chinese cyber espionage and the evolving threat landscape.
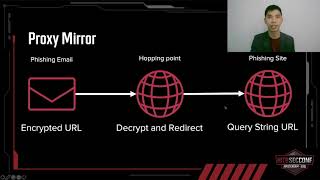
Dissecting Phishing Techniques of CloudDragon APT
Análisis detallado de las sofisticadas técnicas de phishing del grupo APT norcoreano CloudDragon, incluyendo casos reales, métodos para evadir la autenticación de dos factores y propagación a sistemas Android.

Techniques to Gather Threat Intel and Track Actors
Discover 24 techniques for gathering threat intelligence and tracking actors, illustrated with 30 real-world cases. Learn about crimeware vulnerabilities, C&C misconfigurations, and underground marketplaces.
Fast Chat with Austin Murphy - CrowdStrike’s VP & GM - Falcon Complete
Explore the evolving ransomware threat landscape and learn effective defense strategies from CrowdStrike's VP & GM of Falcon Complete.
The Kitten that Charmed Me - The 9 Lives of a Nation State Attacker
Uncover how operational security errors of a state-sponsored threat group revealed details of their entire operation, targeting high-profile individuals and compromising sensitive information.
MITRE ATT&CK - The Play at Home Edition
Learn how various cybersecurity teams can leverage MITRE ATT&CK framework to enhance threat tracking and protection strategies, with practical insights for immediate implementation.
Operation Chimera - APT Operation Targets Semiconductor Vendors
Analysis of APT attacks on semiconductor industry, focusing on Taiwan. Explores threat actors, campaigns, and security status, highlighting potential global supply chain impacts.
Adversary Detection Pipelines - Finally Making Your Threat Intel Useful
Learn to maximize your threat intelligence program's value, enhancing security across teams with practical strategies for effective adversary detection and intel utilization.

Automated Extraction of Configuration and Payloads from Sophisticated Malware
Automated malware analysis system for extracting payloads, configurations, and indicators from sophisticated malware, reducing time and skill requirements for threat intelligence.

The Frugal Girl’s Guide to Threat Intelligence
Learn cost-effective threat intelligence strategies to enhance your organization's security posture. Discover open-source tools, free resources, and integration techniques for incident prevention and response.
Sharing is Not Caring - Proliferation of GitHub Code in Real Attacks
Explore the consequences of open-source malware deployment, analyze attacker toolkits, and learn about defender opportunities in this insightful cybersecurity talk.